Solution · Identity and access
Identity that runs inside your own cloud.
For companies whose data cannot leave their boundary: AuthFI runs in your AWS, Google Cloud, Azure or Oracle account, or your own data centre.
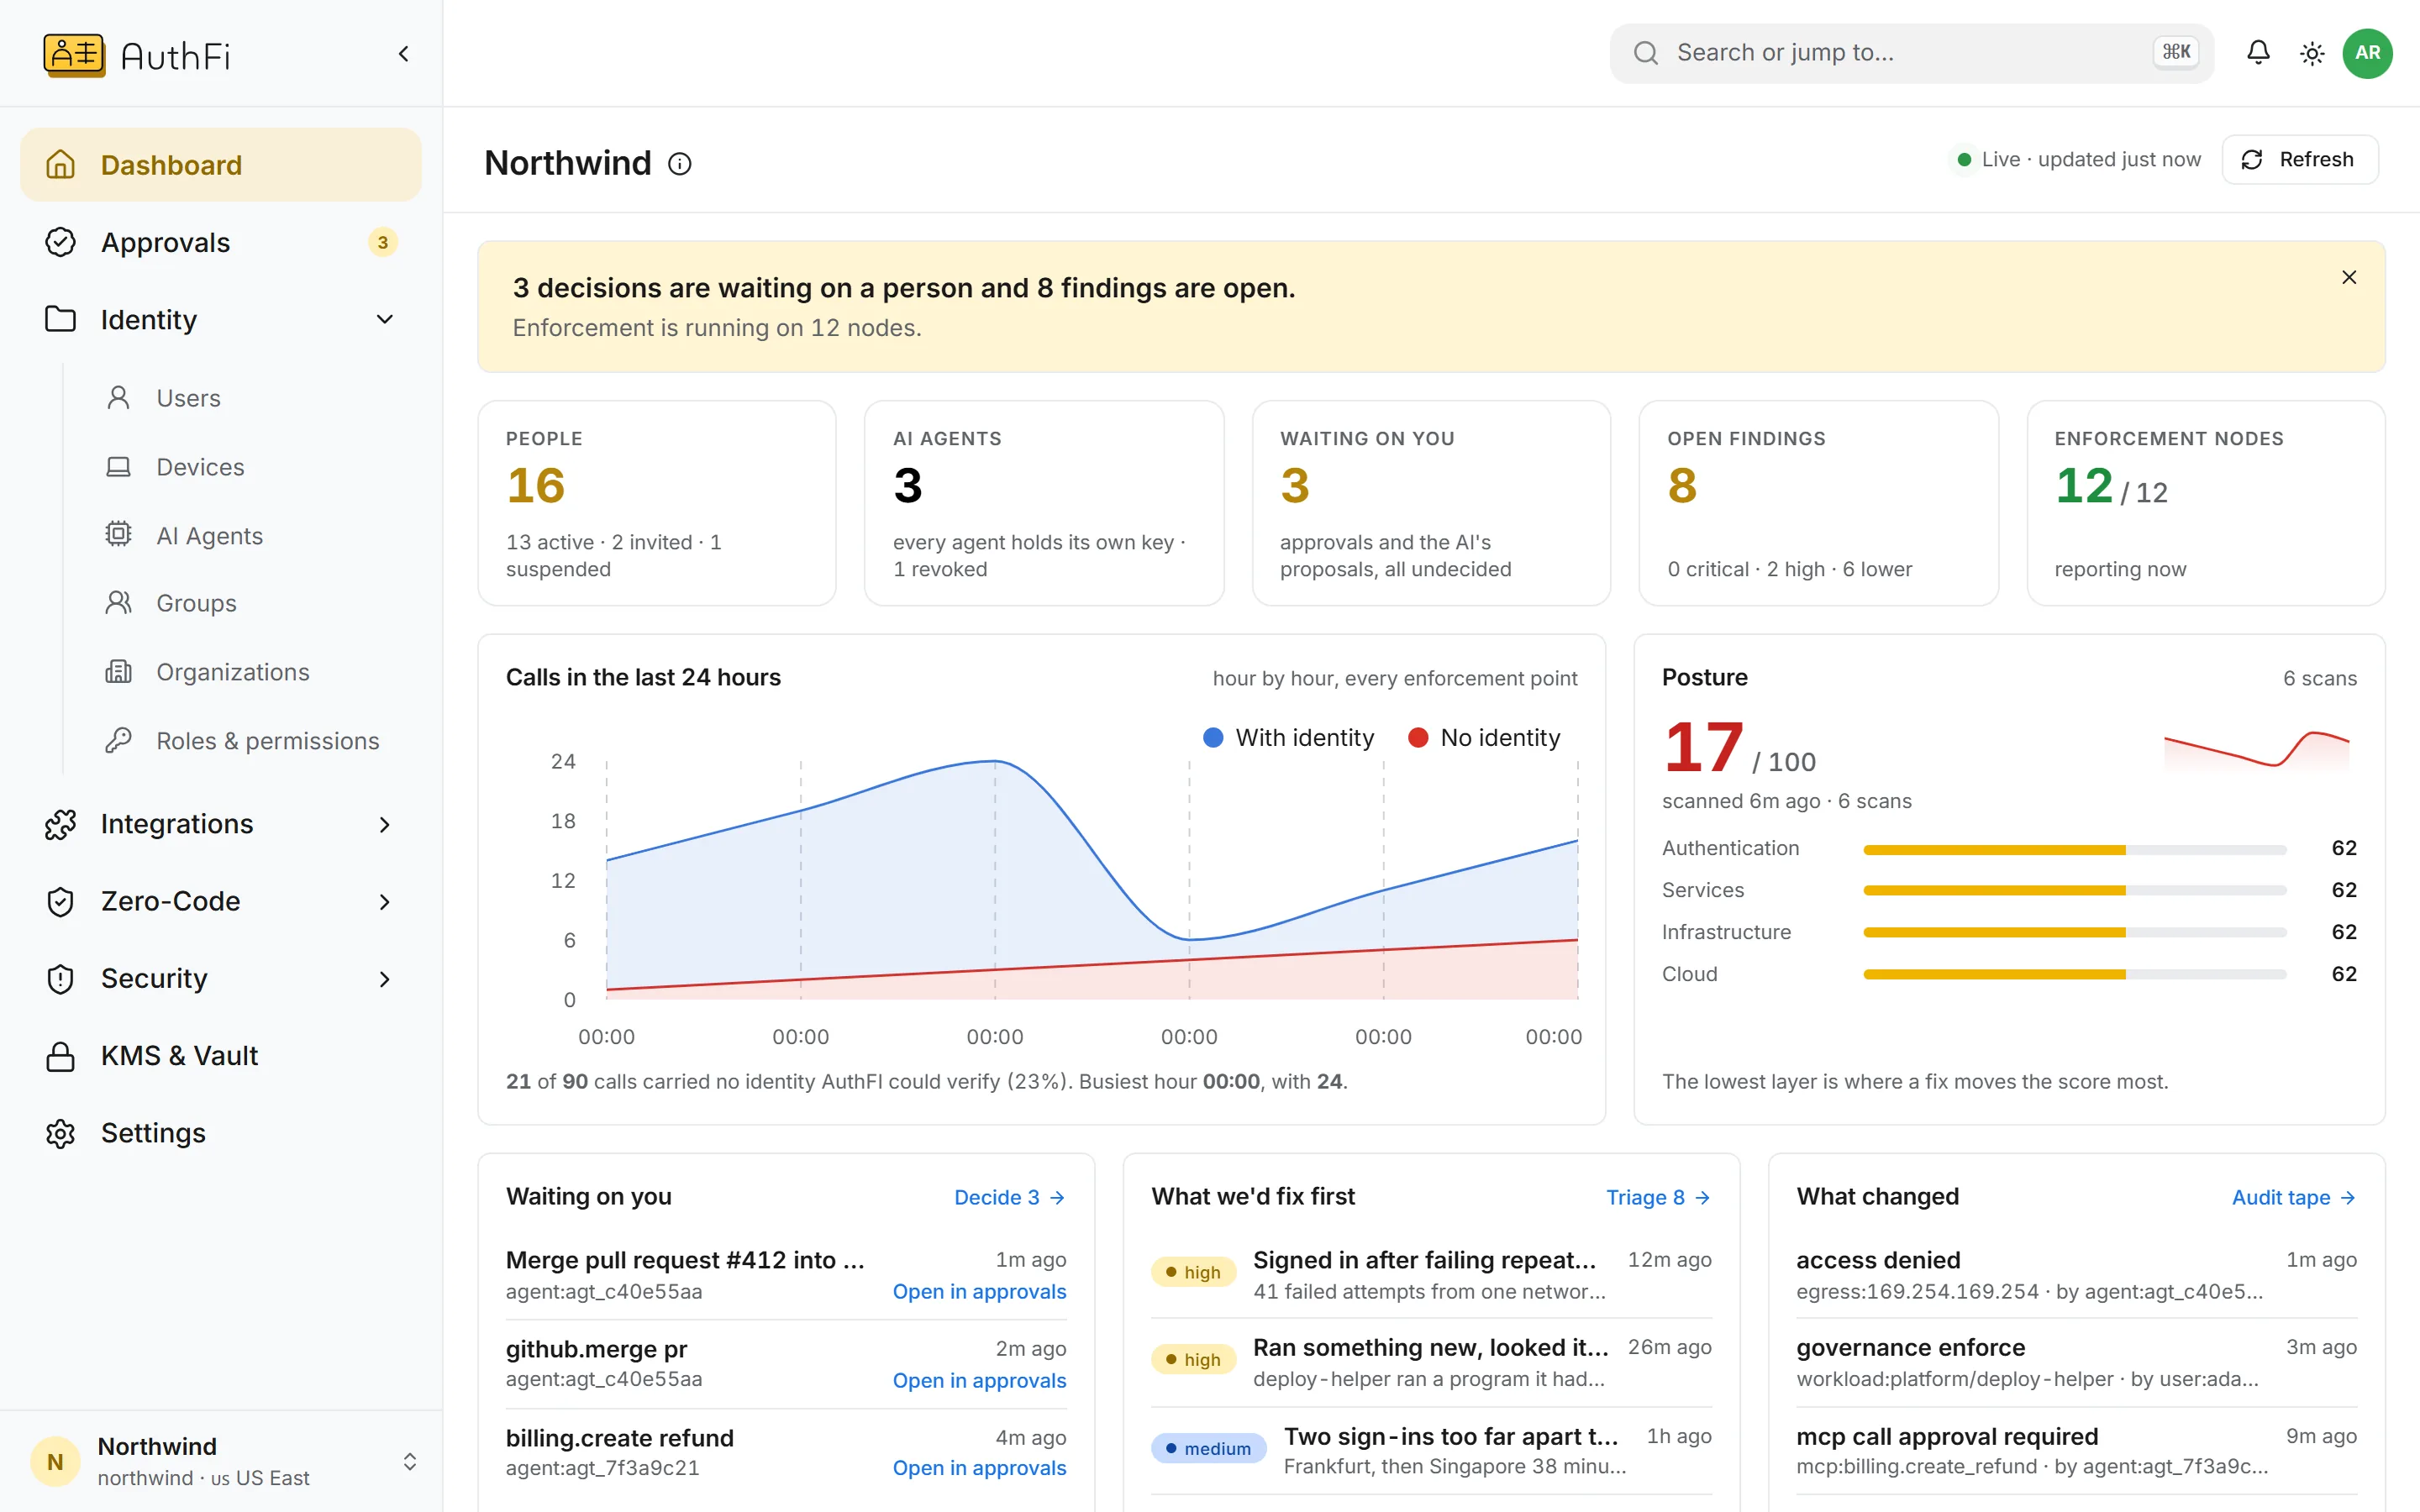
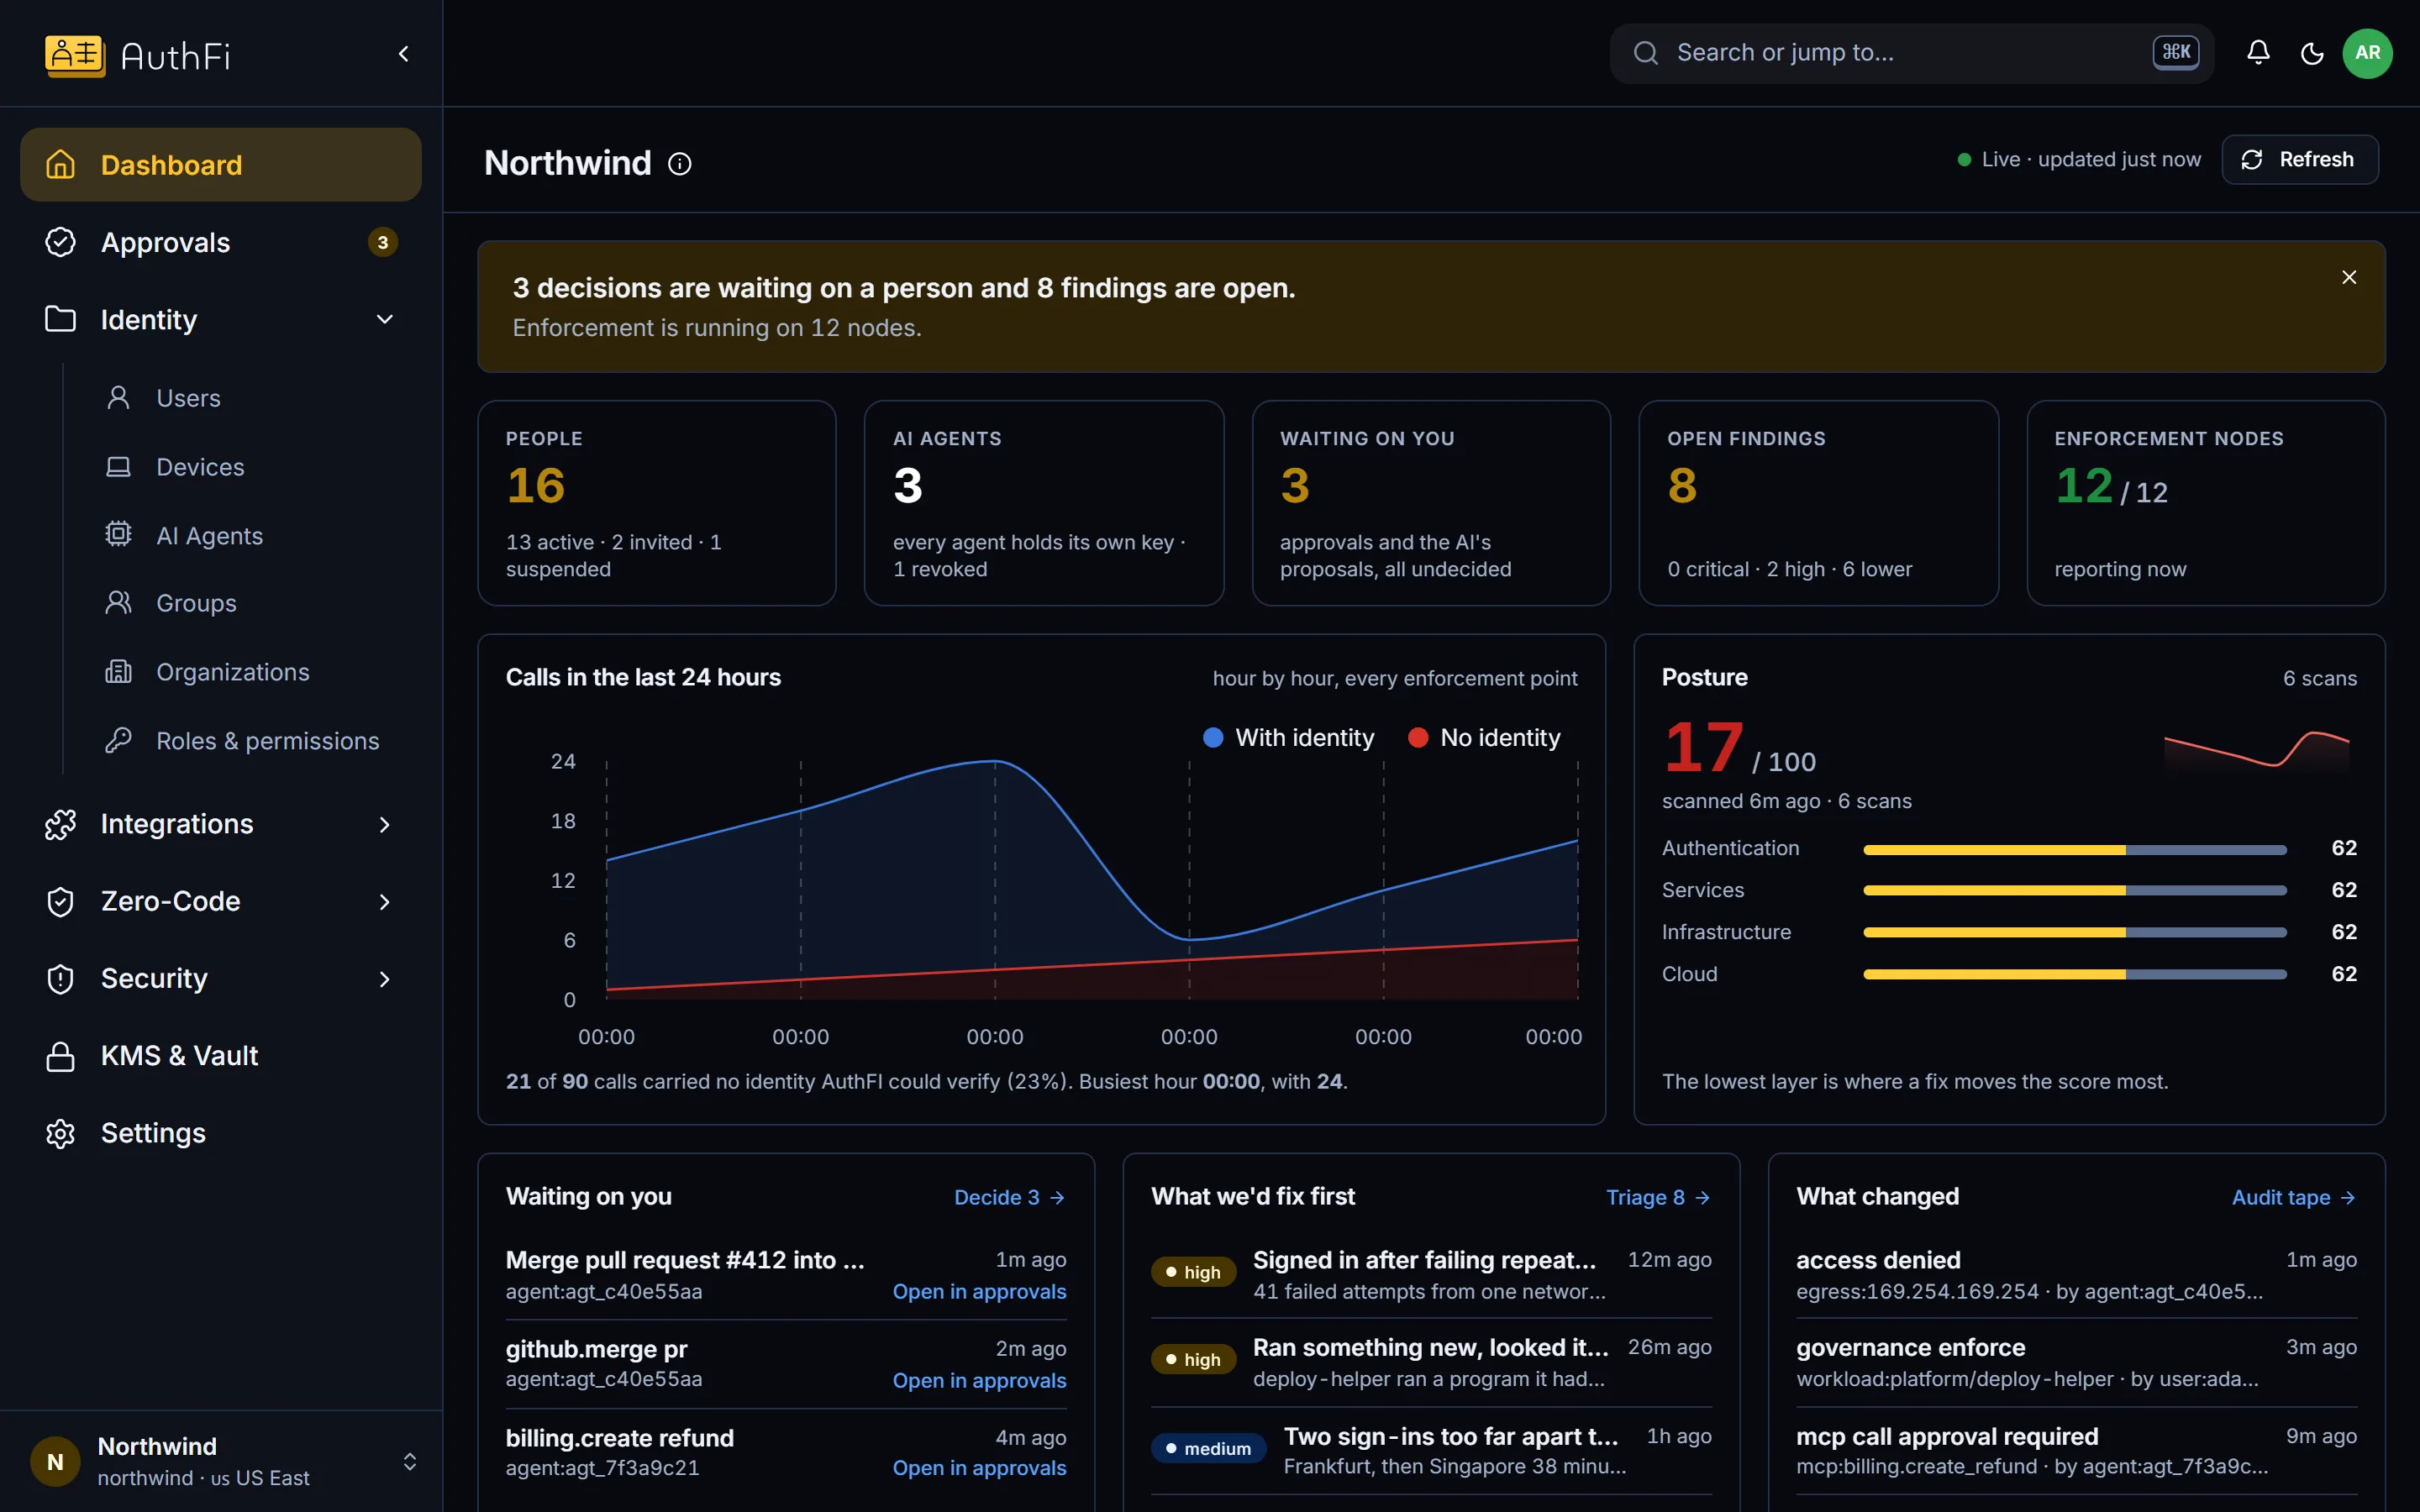
What changes
The problem as most companies have it today, and the same thing with AuthFI.
How it works
Each step, on the screen you would use.
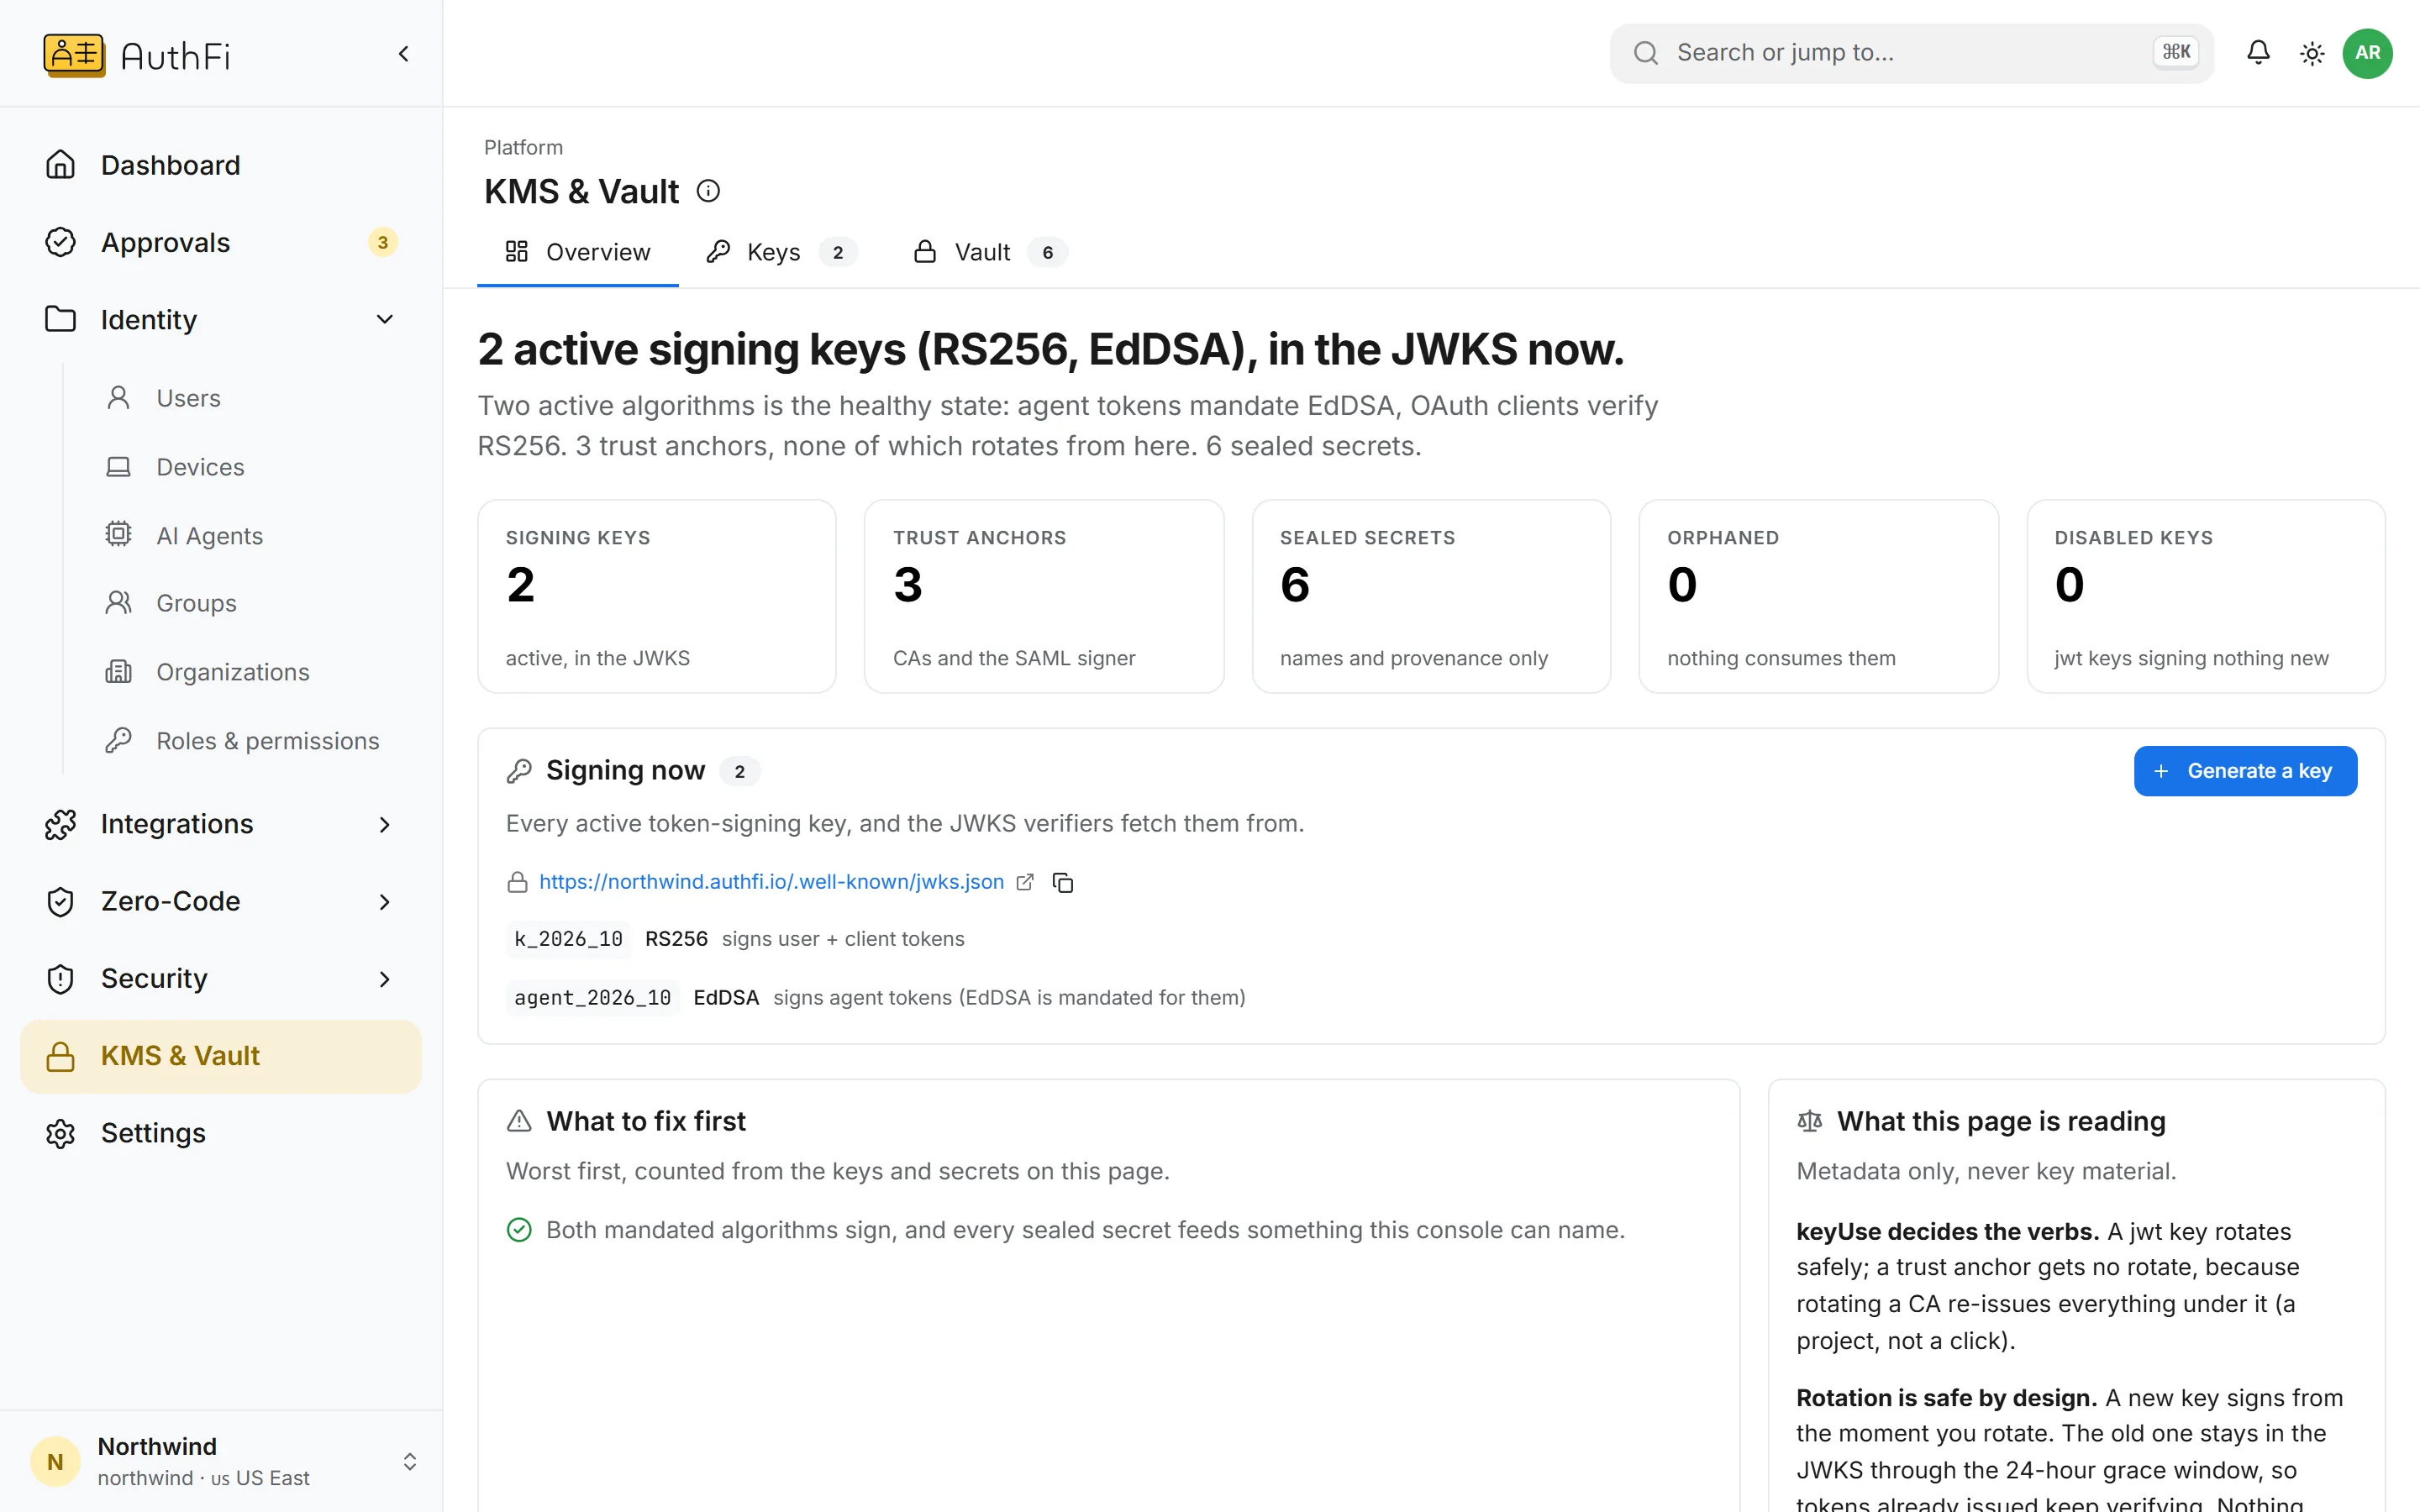
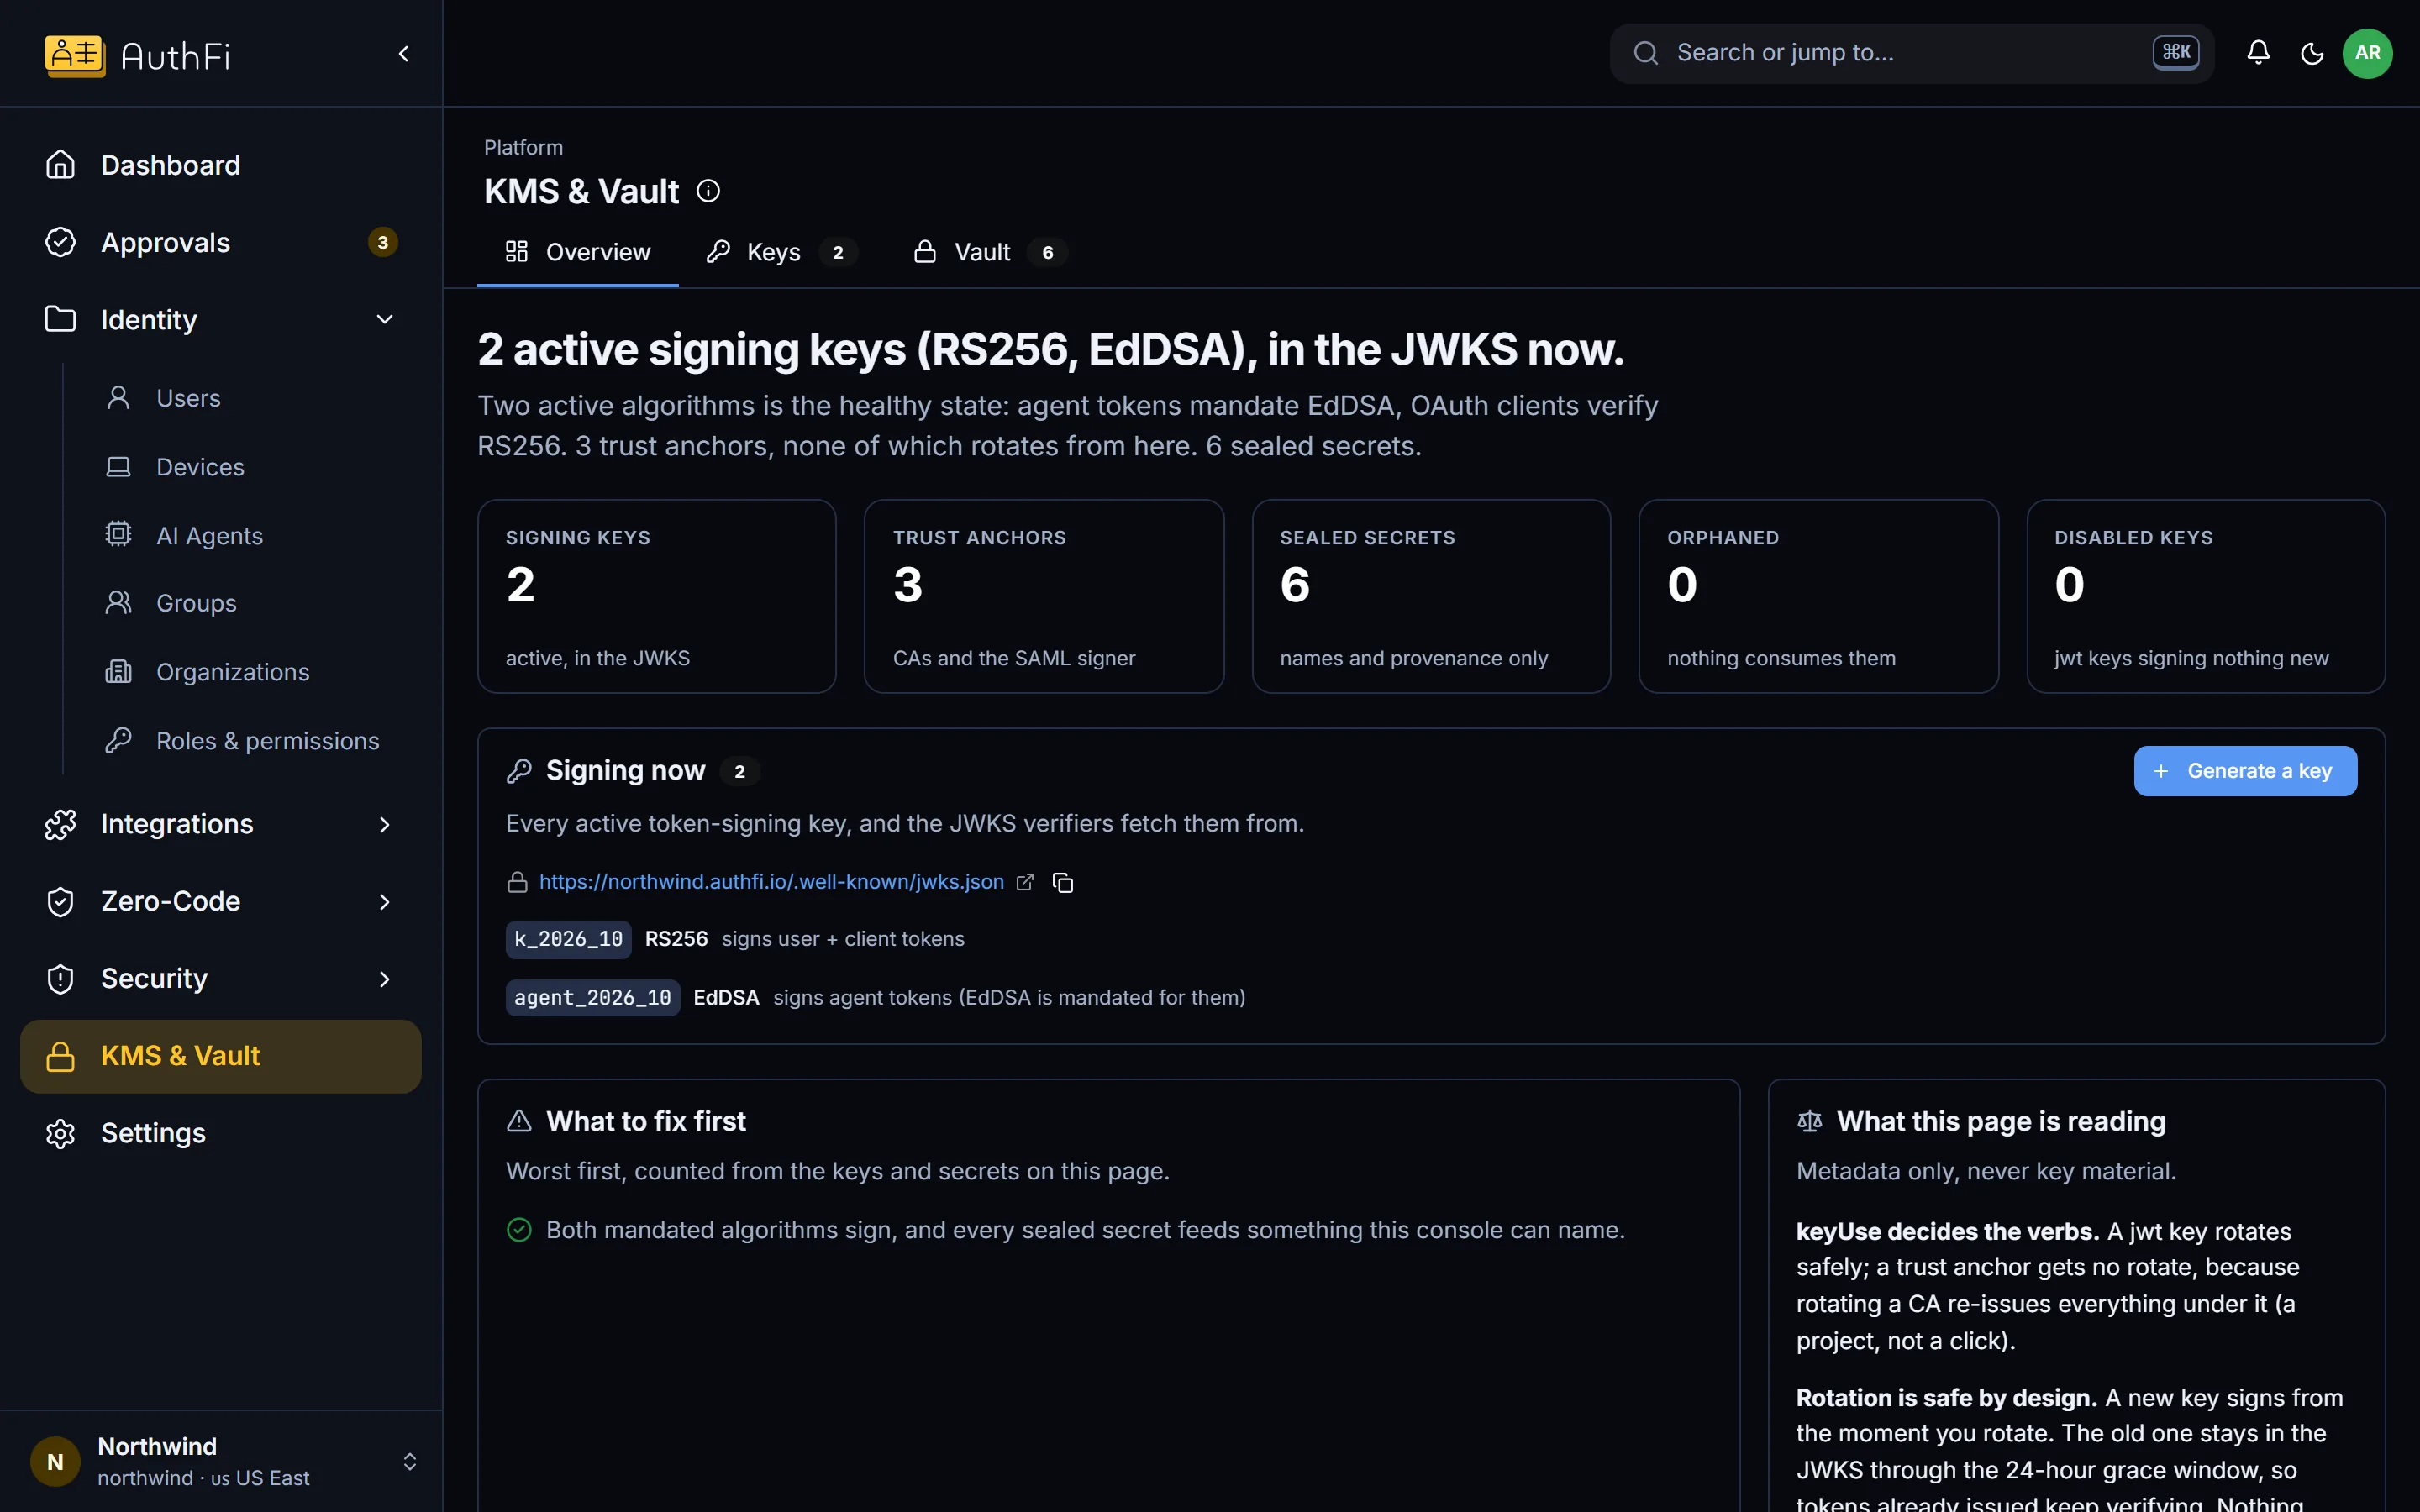
Keys
Your keys, in your region.
Every project has its own signing keys. Rotating one does not sign anybody out.
Keys per project
Rotation with no sign-out
Secrets sealed on arrival
Our region
Virginia, USA
AWS, US East
us-east-1Our region
Mumbai, India
Google Cloud, Mumbai
asia-south1Your own cloud
Any cloud
AWS, Google Cloud, Azure, Oracle, or your own data centre. Run by you, or by us inside your boundary.
EnterpriseRead on
Running in your own cloud is part of the Enterprise plan.
Pricing
Deployment options in the plan builder
OpenKeys and secrets
Signing keys per project
OpenPrivacy
What is kept, and where
OpenMore in Identity and access
Zero-Code: sign-in for services, with no code
Zero-Code puts sign-in and access rules in front of services you already run.
See howWorkforce identity: a modern IdP
Single sign-on, provisioning, passkeys and devices, on open standards, with users included in the plan.
See howCloud and server access with no stored keys
Short-lived cloud roles and server sessions, granted by group.
See how