Solution · by industry
Identity for healthcare, where every access has a name.
For hospitals, labs and health software companies: one account per person, access by role, and a record of every access and every refusal.
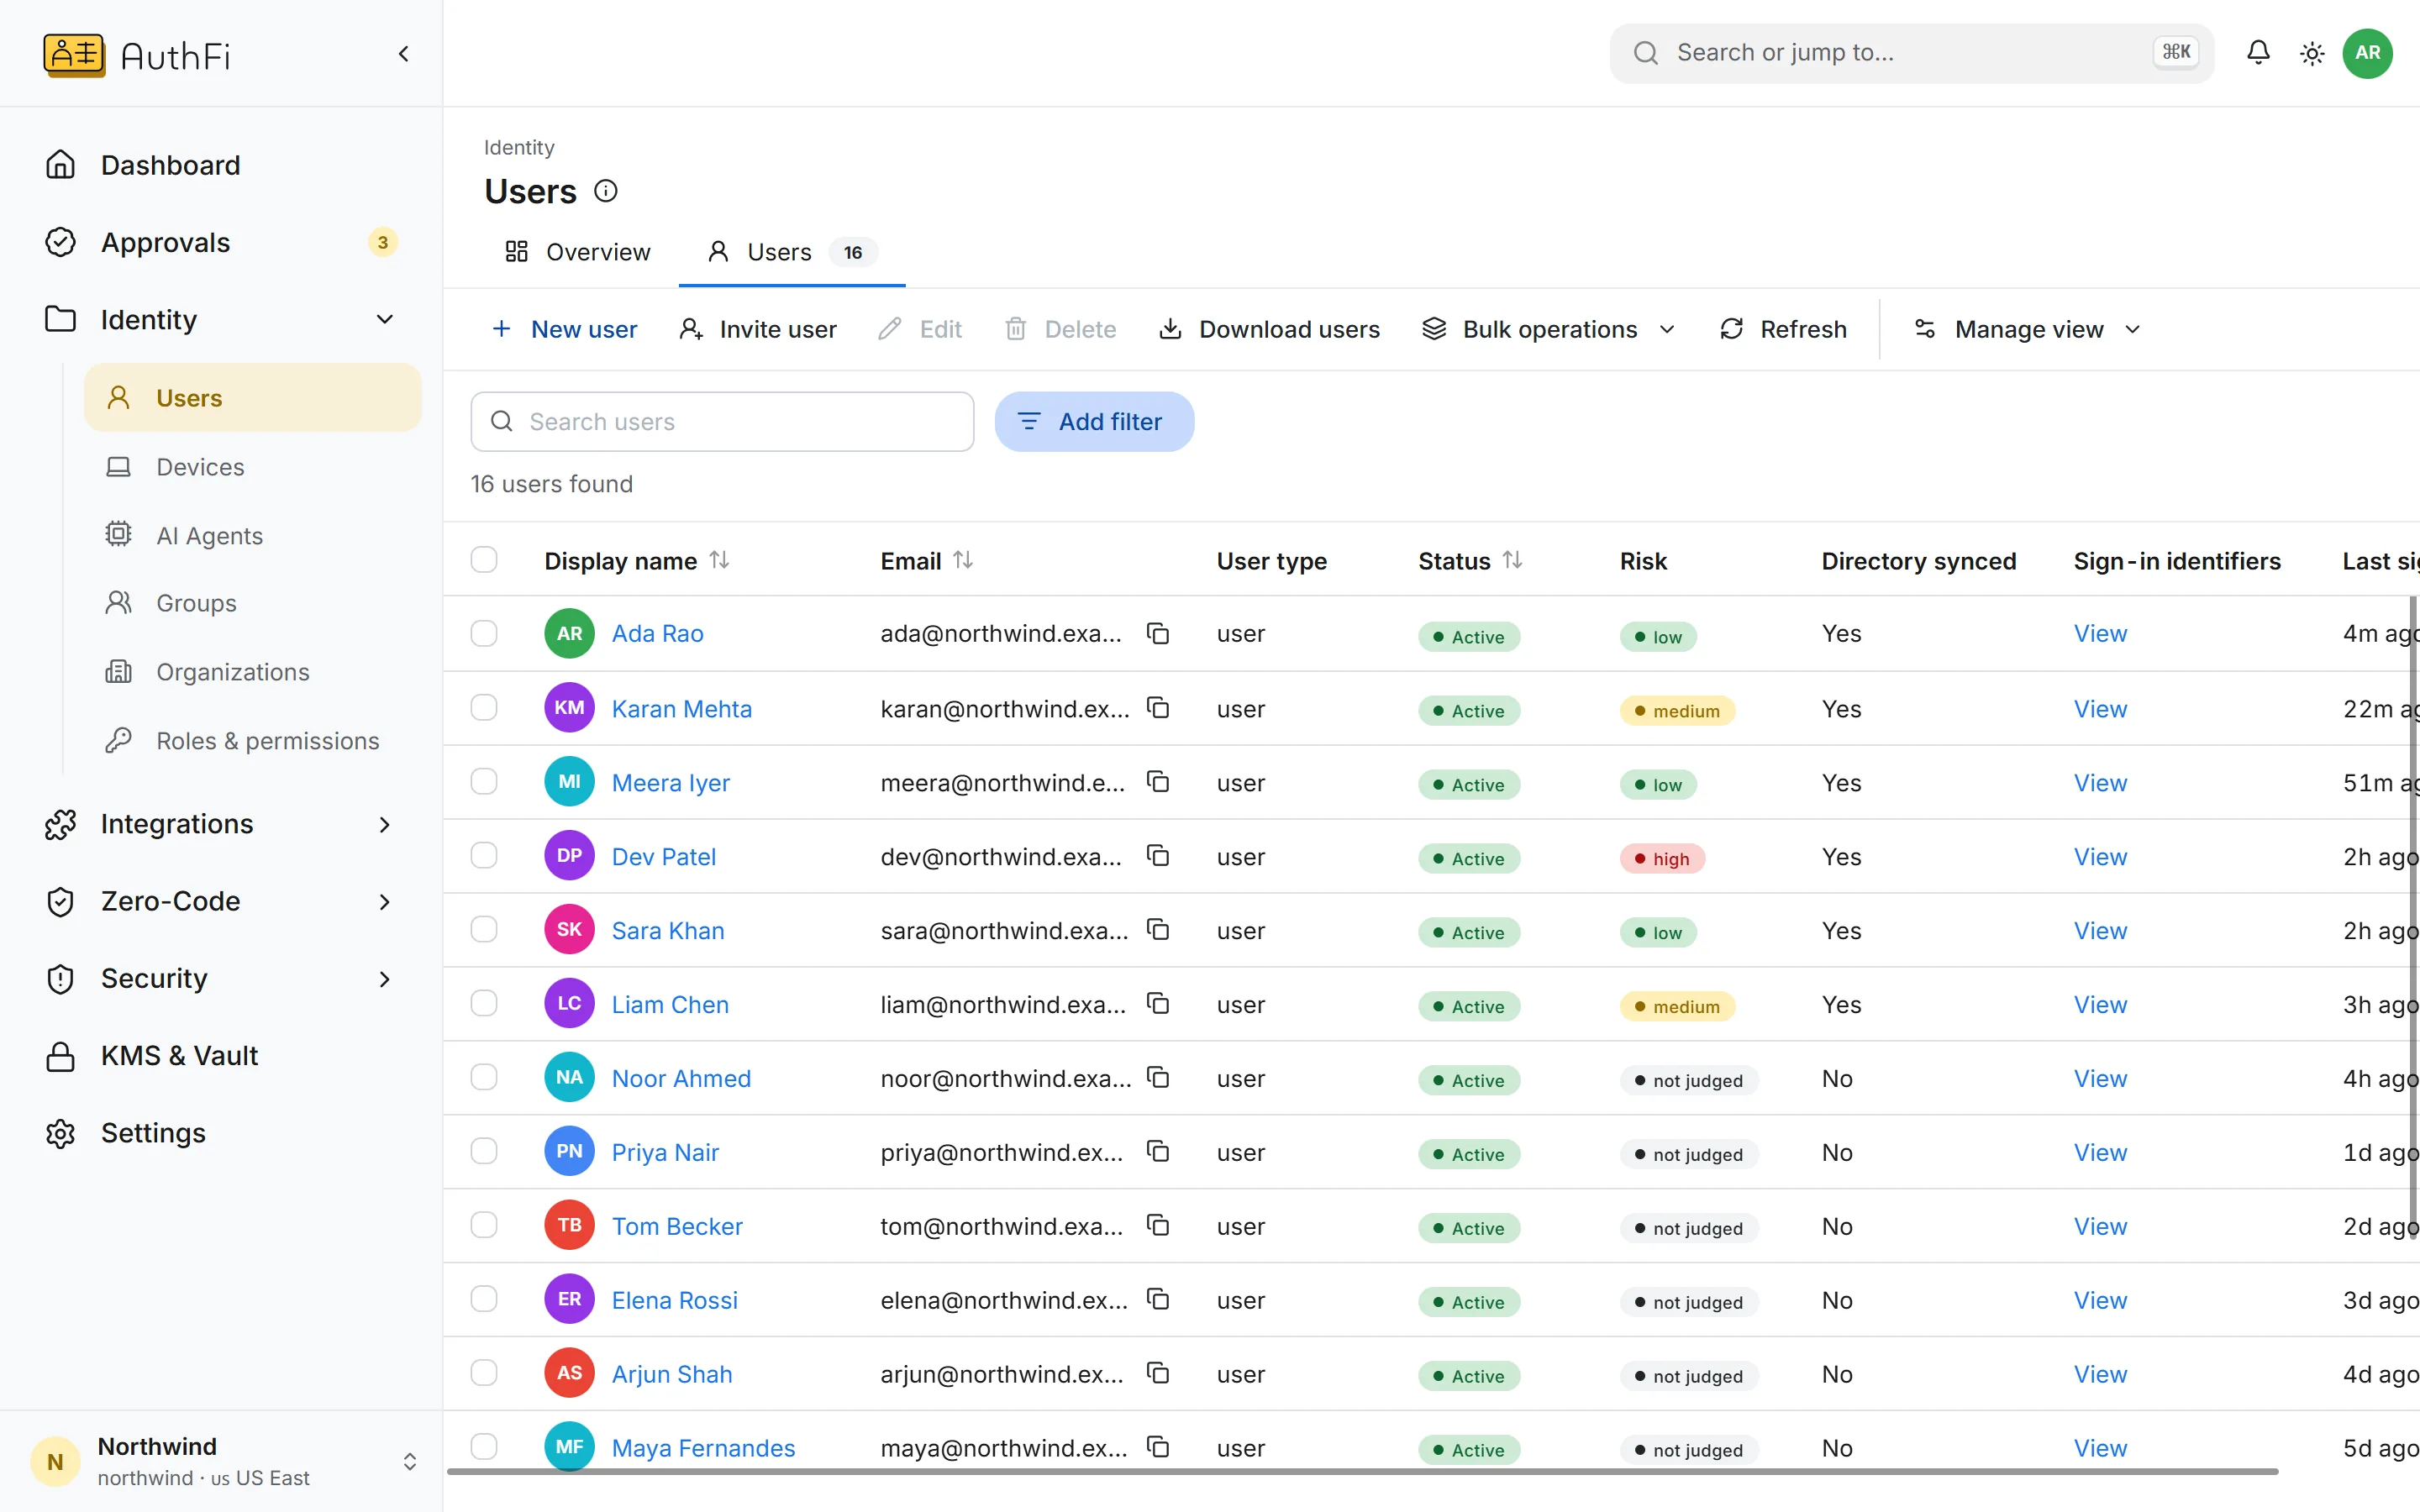
Everyone with an account
Each person with their status, the risk their last sign-ins carried, and whether they came from your directory.
What changes
Where organisations like yours usually start, and where AuthFI takes them.
How it works
Each step, on the screen you would use.
People
One account per person, kept in step with HR.
Connect your directory. People are added, changed and removed as it changes, and their groups decide what they can open.
Provisioning over SCIM
Access by group, not by hand
Sessions that can be listed and ended
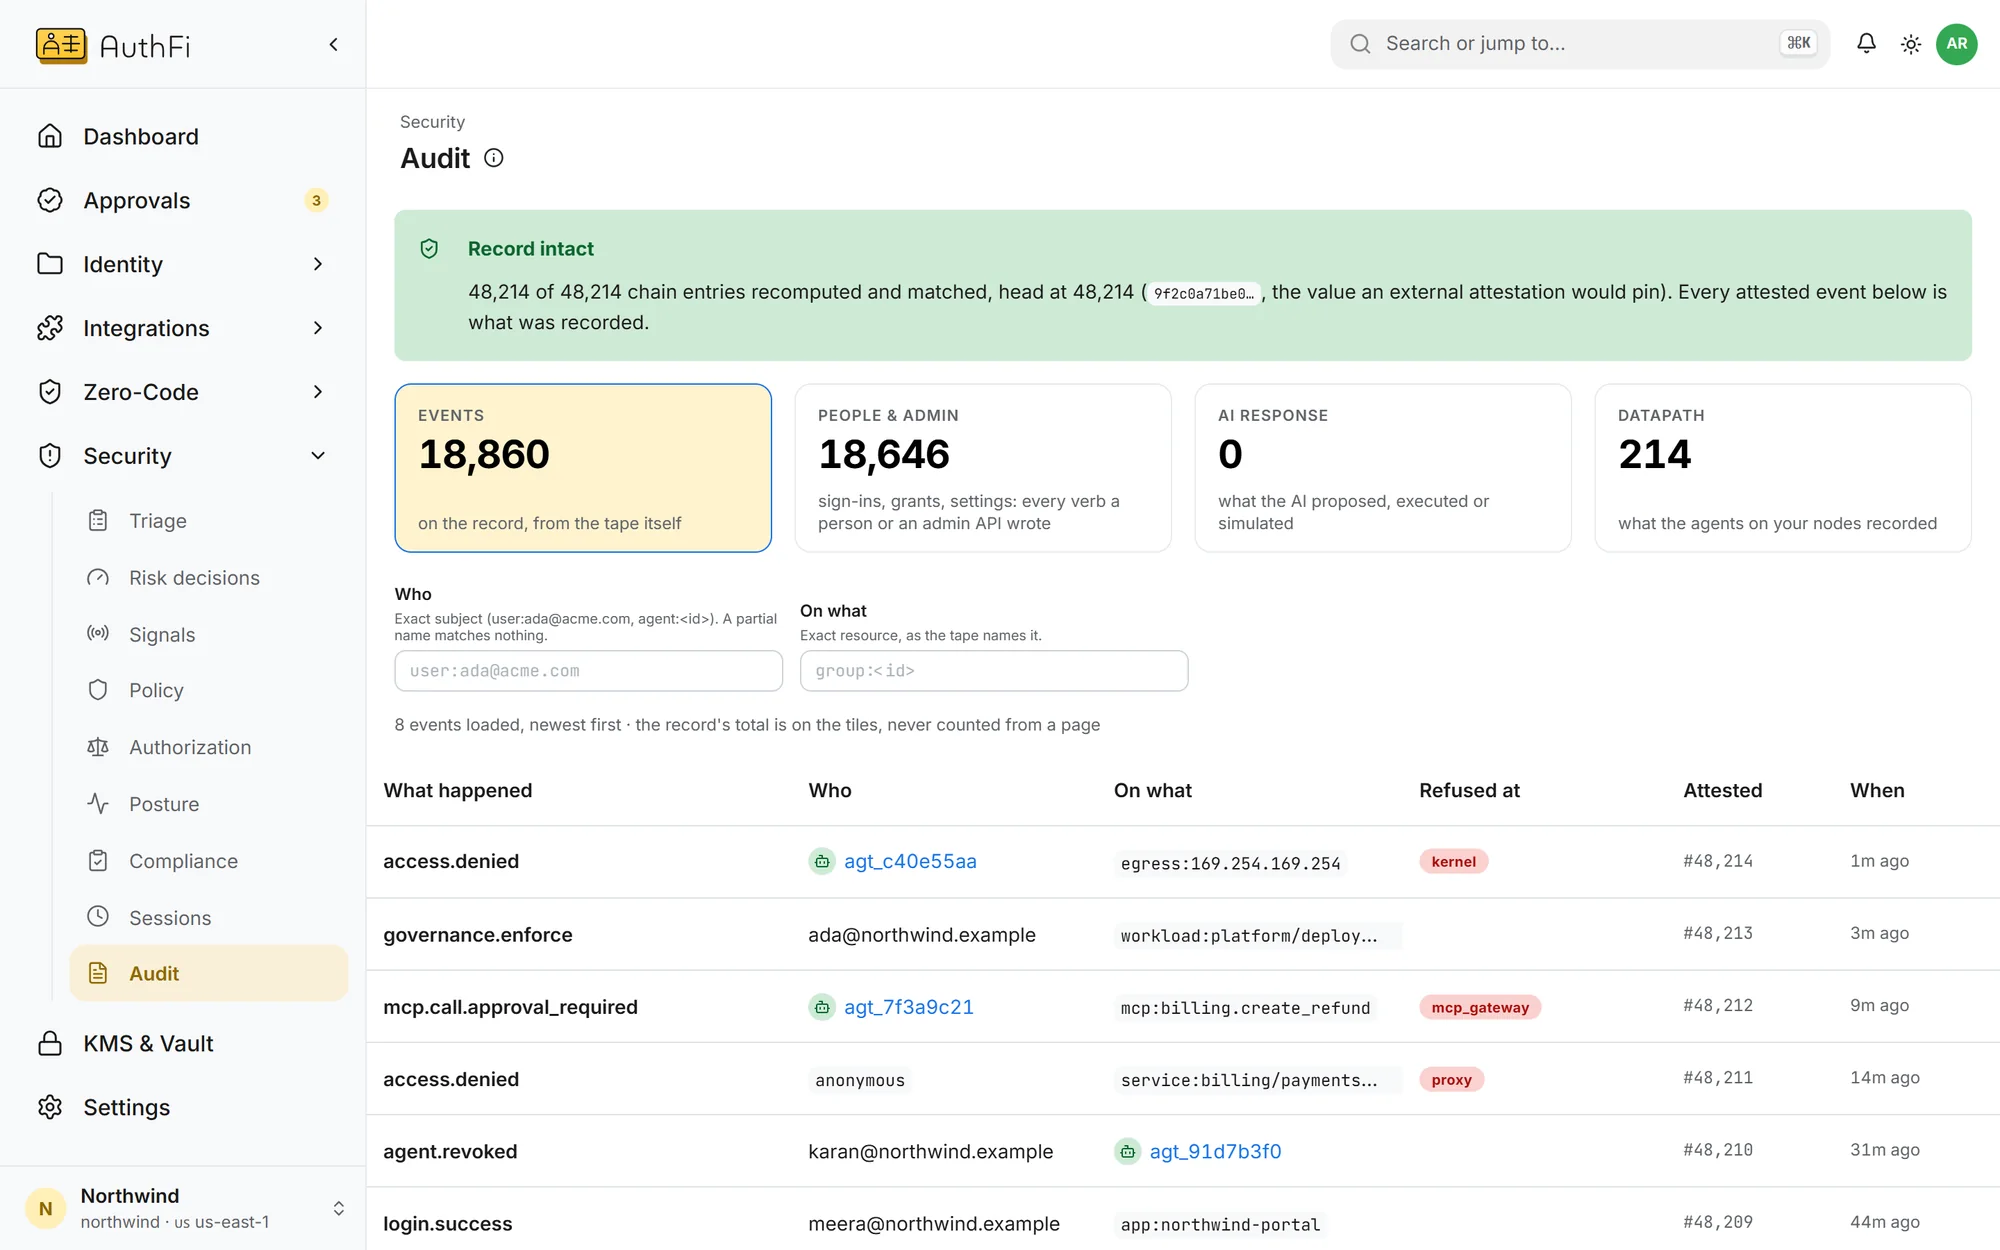
Record
Who opened what, and who was refused.
Every sign-in and every refusal is on one record, for people and for AI assistants alike.
Filter by person, action or layer
Refusals are recorded, not only successes
Export to your log tools
Our region
Virginia, USA
AWS, US East
us-east-1Our region
Mumbai, India
Google Cloud, Mumbai
asia-south1Your own cloud
Any cloud
AWS, Google Cloud, Azure, Oracle, or your own data centre. Run by you, or by us inside your boundary.
EnterpriseWhat you are asked for
The questions a regulator, an auditor or a customer's security team puts to you, and what in AuthFI answers each.
A unique identity for every user
One account per person, with passkeys and a second step
Workforce identityAccess removed when people leave or move
Provisioning from your directory over SCIM, and one group change removes access everywhere
Workforce identityData kept where the law requires
A region you choose, or your own cloud account or data centre
Your own cloudControl over AI tools that touch records
Each AI agent has an owner, limits, approvals and an off switch
Govern AI agentsRead on
This page describes controls the product has. It is not a statement of certification. Ask us for our current security documentation.
Workforce identity
A modern IdP for staff
OpenGovern AI agents
Owners, limits and approvals
OpenTalk to us
Ask for our security documentation
OpenOther industries
Financial services
For banks, fintechs and insurers: every action on the record, and data that stays put.
See howSoftware and AI companies
Enterprise-ready sign-in for your product, and control of the agents inside it.
See howPublic sector and regulated India
Identity that runs in India, or inside your own data centre.
See how