Solution · Identity and access
Accounts that follow your directory, in and out.
With SCIM 2.0 your directory creates, updates and removes people in AuthFI, and AuthFI does the same in the applications that need accounts.
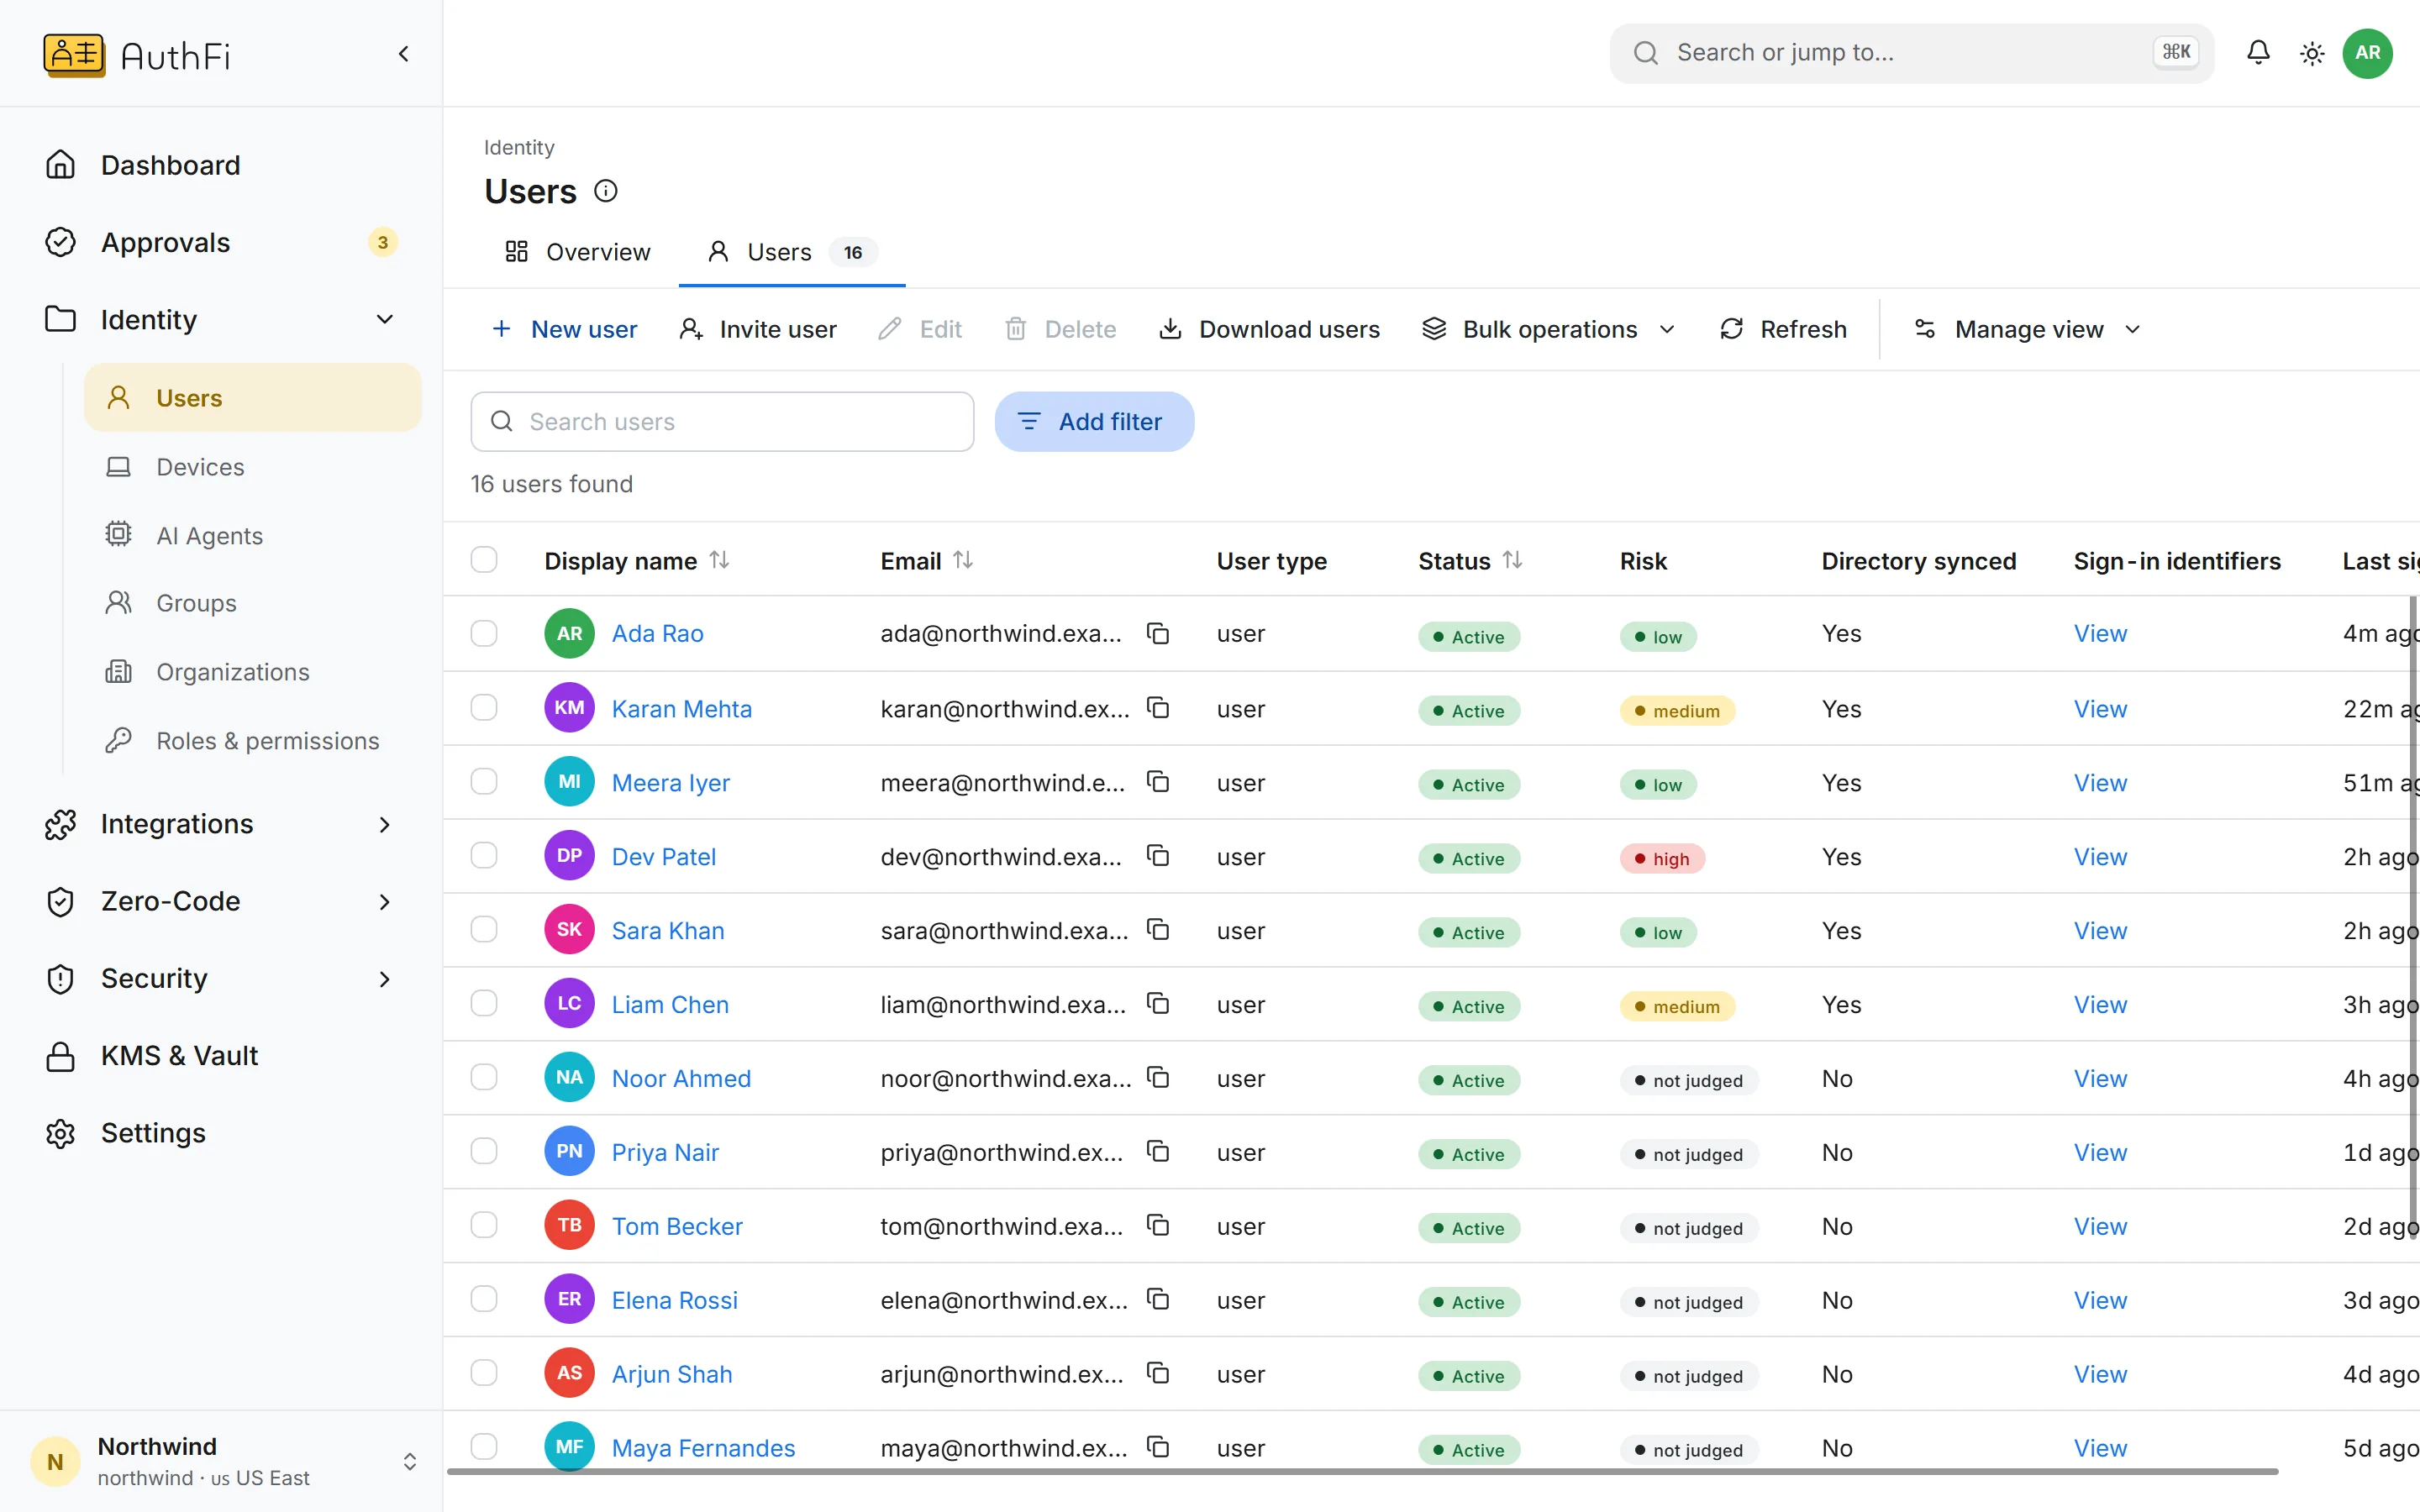
Everyone with an account
Each person with their status, the risk their last sign-ins carried, and whether they came from your directory.
What changes
The problem as most companies have it today, and the same thing with AuthFI.
How it works
Each step, on the screen you would use.
Inbound
Your directory provisions into AuthFI.
Point your identity provider's SCIM connector at your project. People and their groups arrive and stay current.
SCIM 2.0
People and groups
A token you issue and can replace
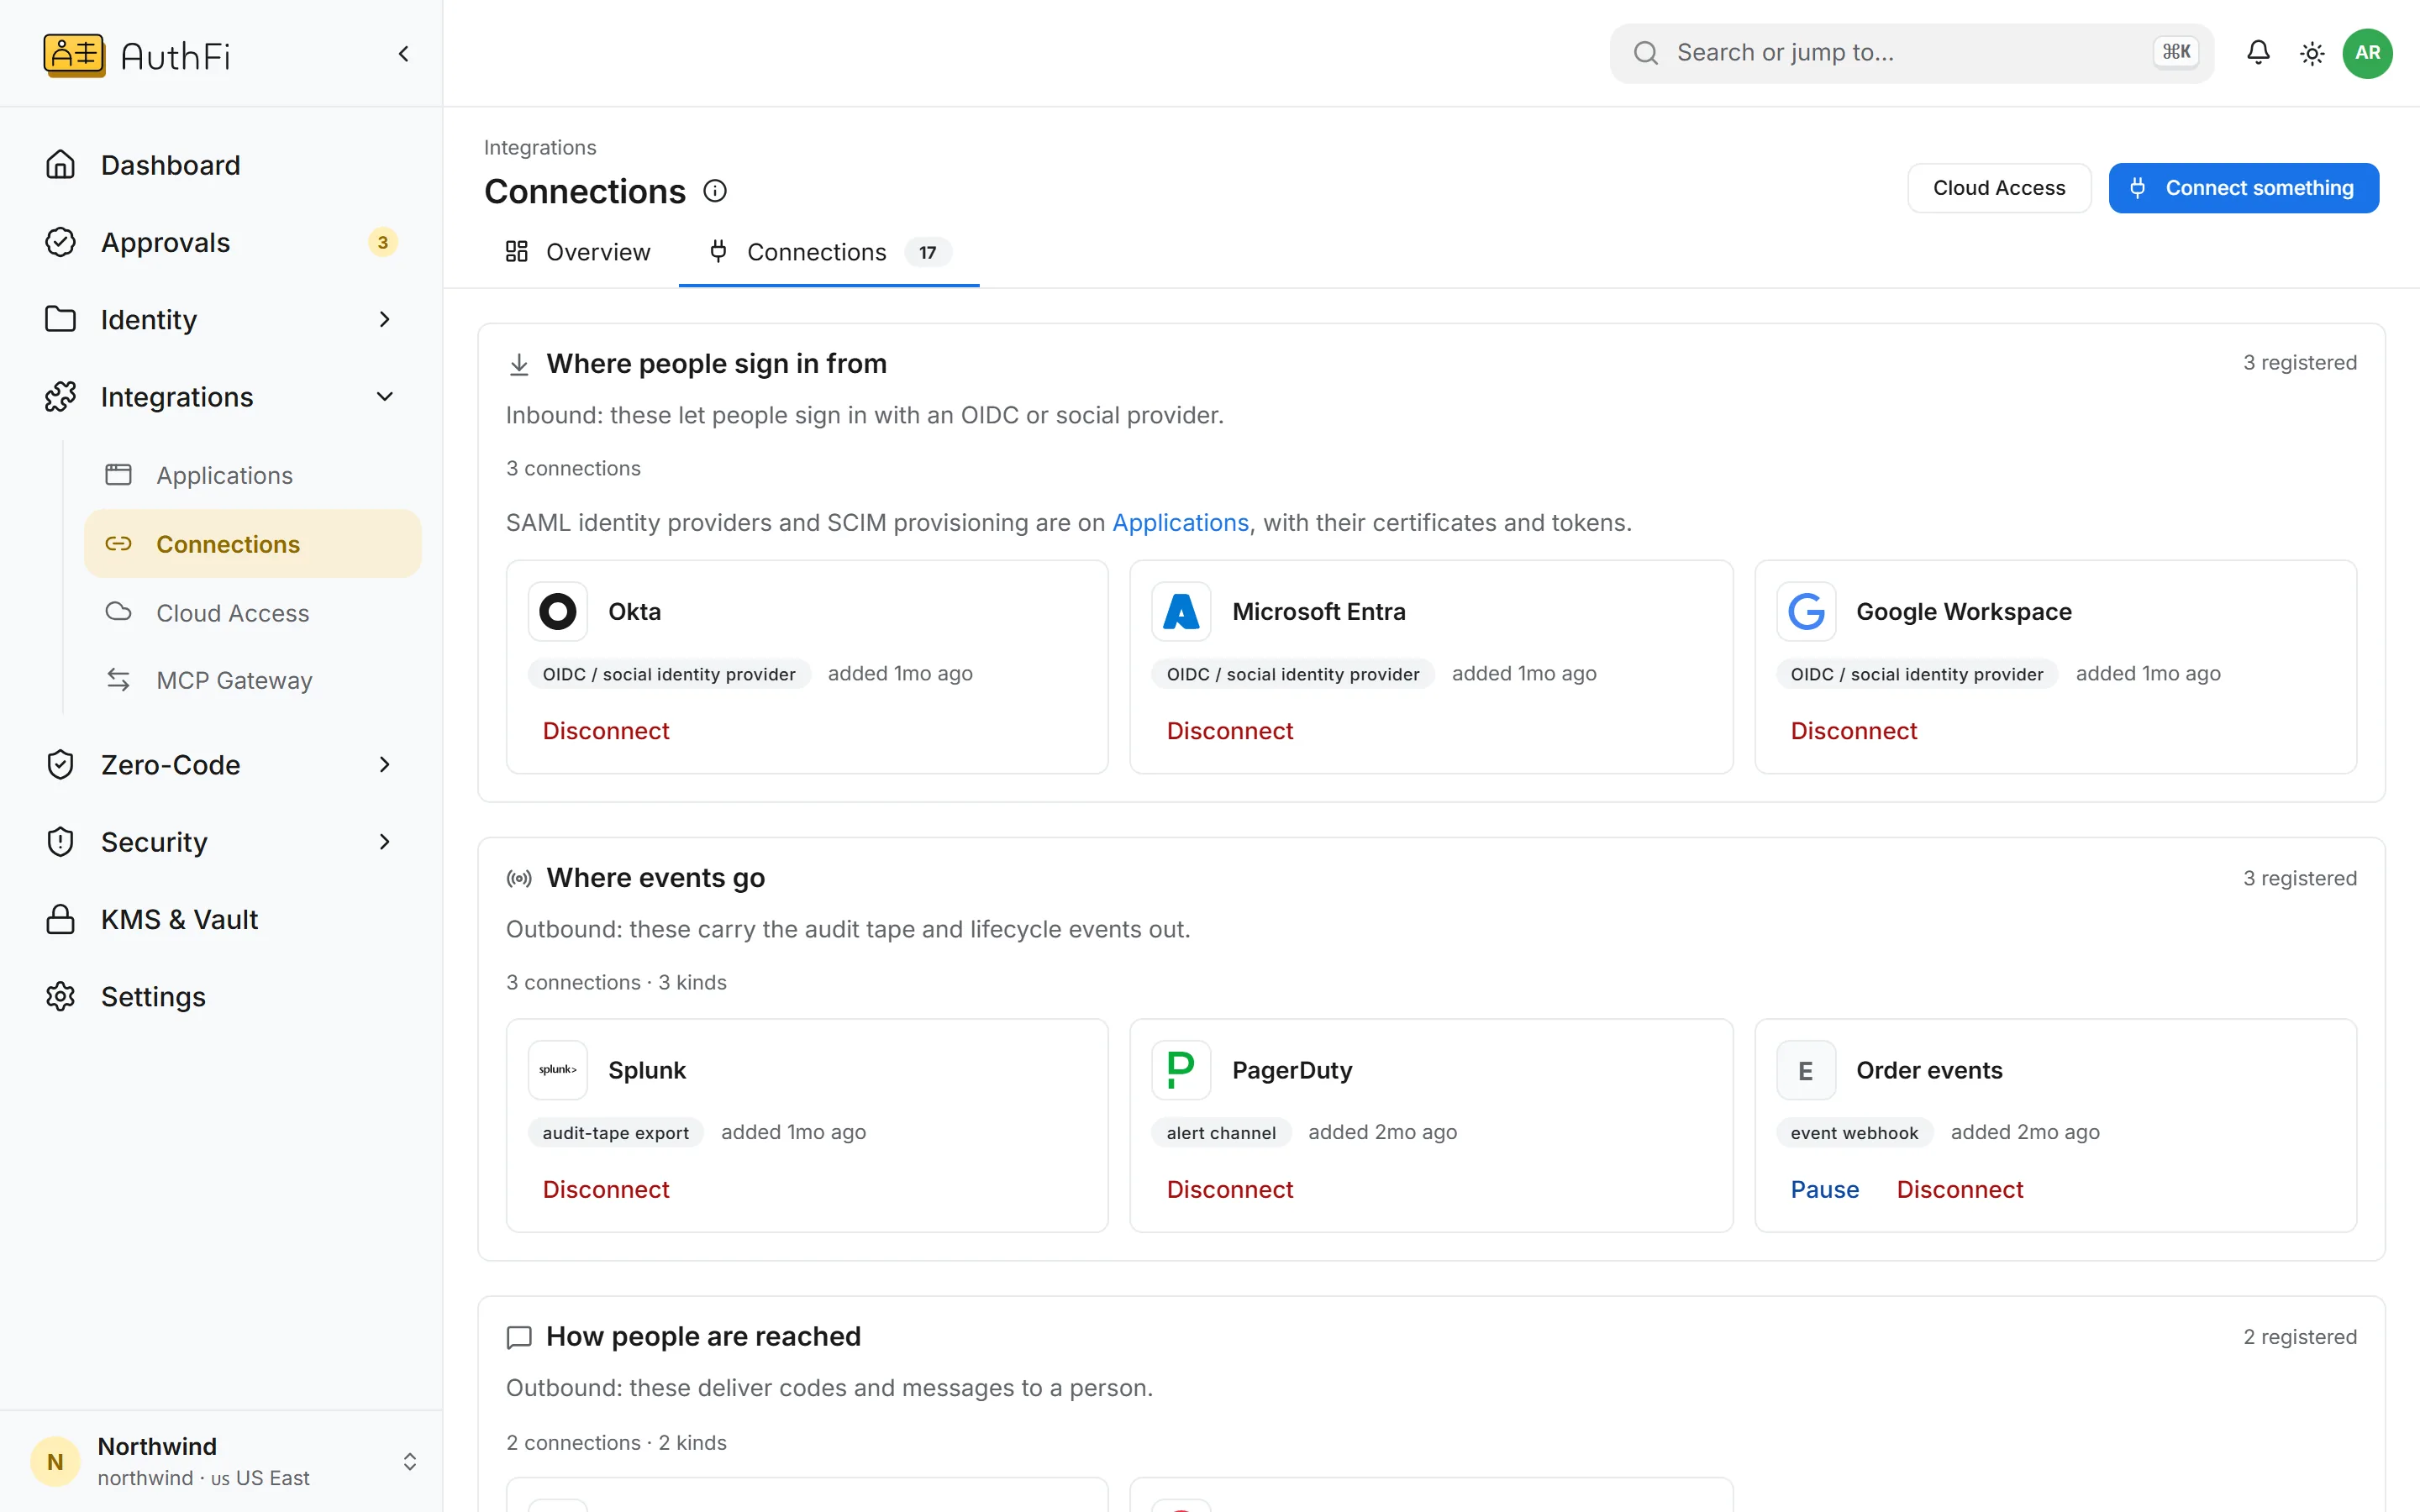
Outbound
AuthFI provisions into your apps.
For applications that keep their own accounts, AuthFI creates, updates and removes them as people change.
Create, update and deactivate
The result of each sync on the record
A dead credential is reported, not retried forever
Read on
The parts of the product behind this.
Workforce identity
Provisioning and the protocols beside it
OpenSAML single sign-on
One sign-in for every app
OpenA modern IdP
The whole workforce story
OpenMore in Identity and access
Zero-Code: sign-in for services, with no code
Zero-Code puts sign-in and access rules in front of services you already run.
See howWorkforce identity: a modern IdP
Single sign-on, provisioning, passkeys and devices, on open standards, with users included in the plan.
See howCloud and server access with no stored keys
Short-lived cloud roles and server sessions, granted by group.
See how