Solution · Identity and access
Reach your clouds and servers with no stored keys.
Engineers and pipelines get cloud roles and server sessions on credentials that last minutes, instead of keys that sit in files for years.
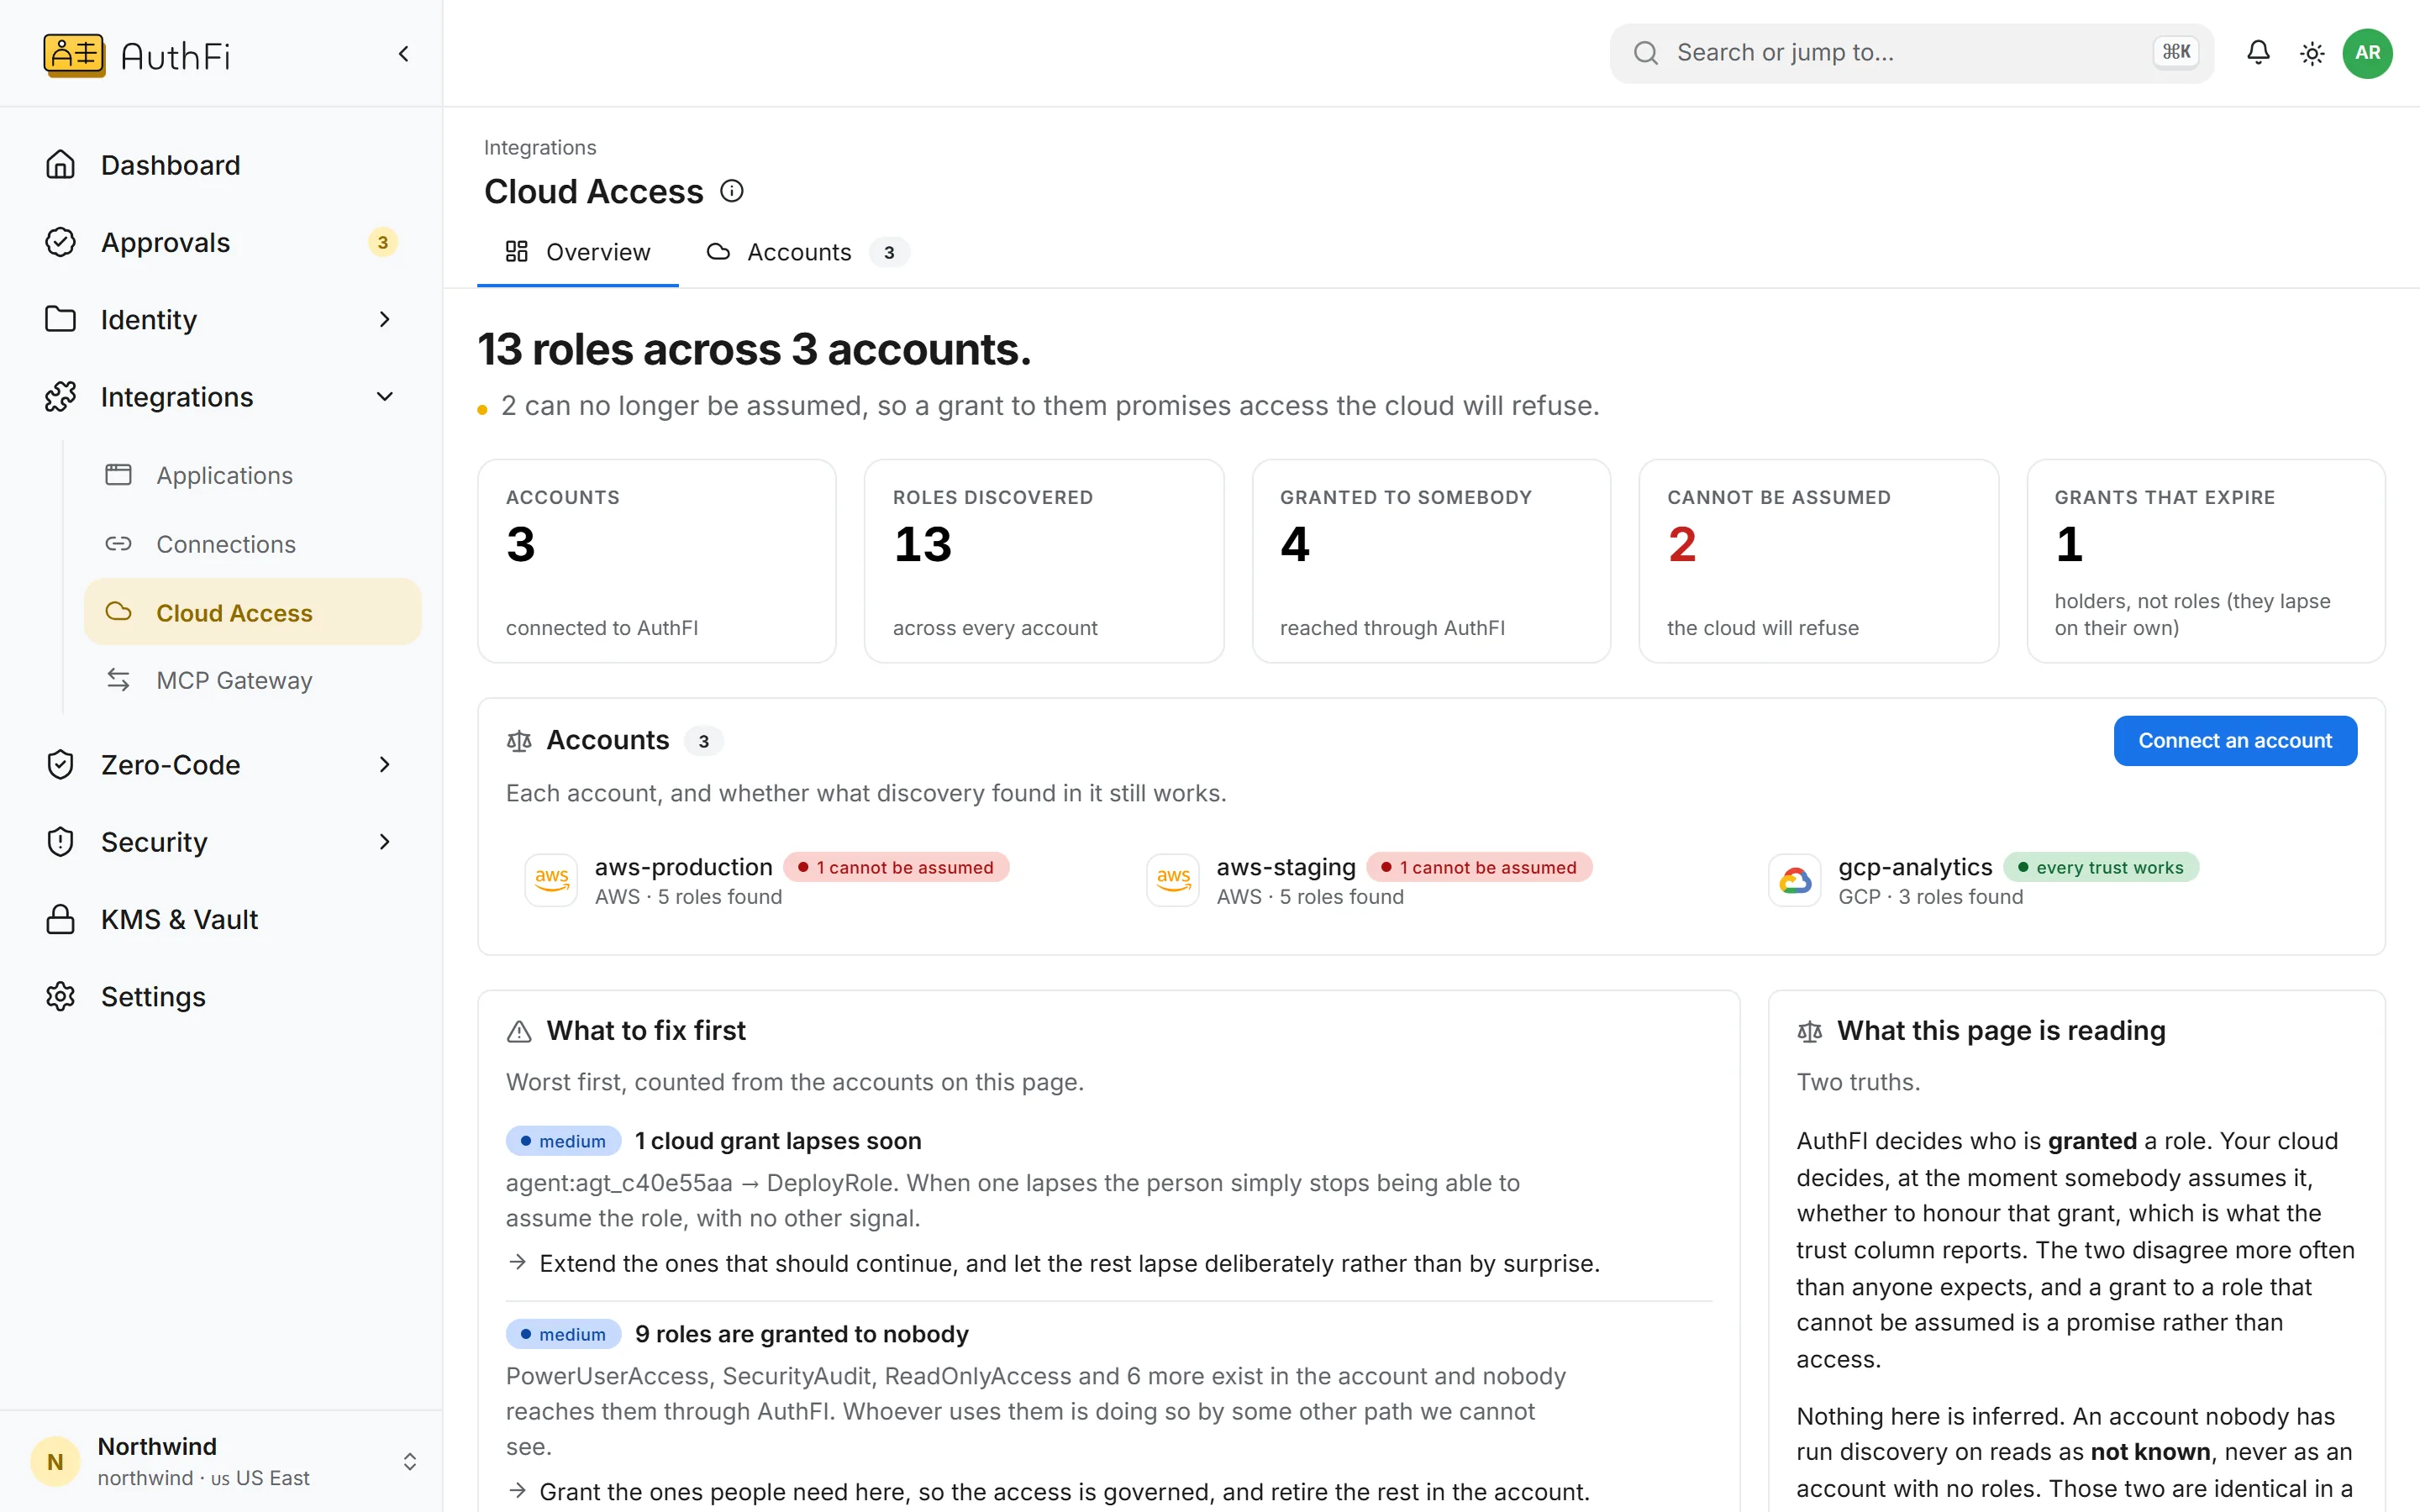
Cloud roles, with no stored keys
AuthFI decides who is granted a role. The cloud decides, when the role is assumed, whether to honour it. This page shows where the two disagree.
What changes
The problem as most companies have it today, and the same thing with AuthFI.
How it works
Each step, on the screen you would use.
Cloud
Cloud roles, granted to groups.
Connect an AWS or Google Cloud account. AuthFI finds its roles, and you grant them to groups.
AWS and Google Cloud
No access key is created or stored
A grant follows the group
Servers
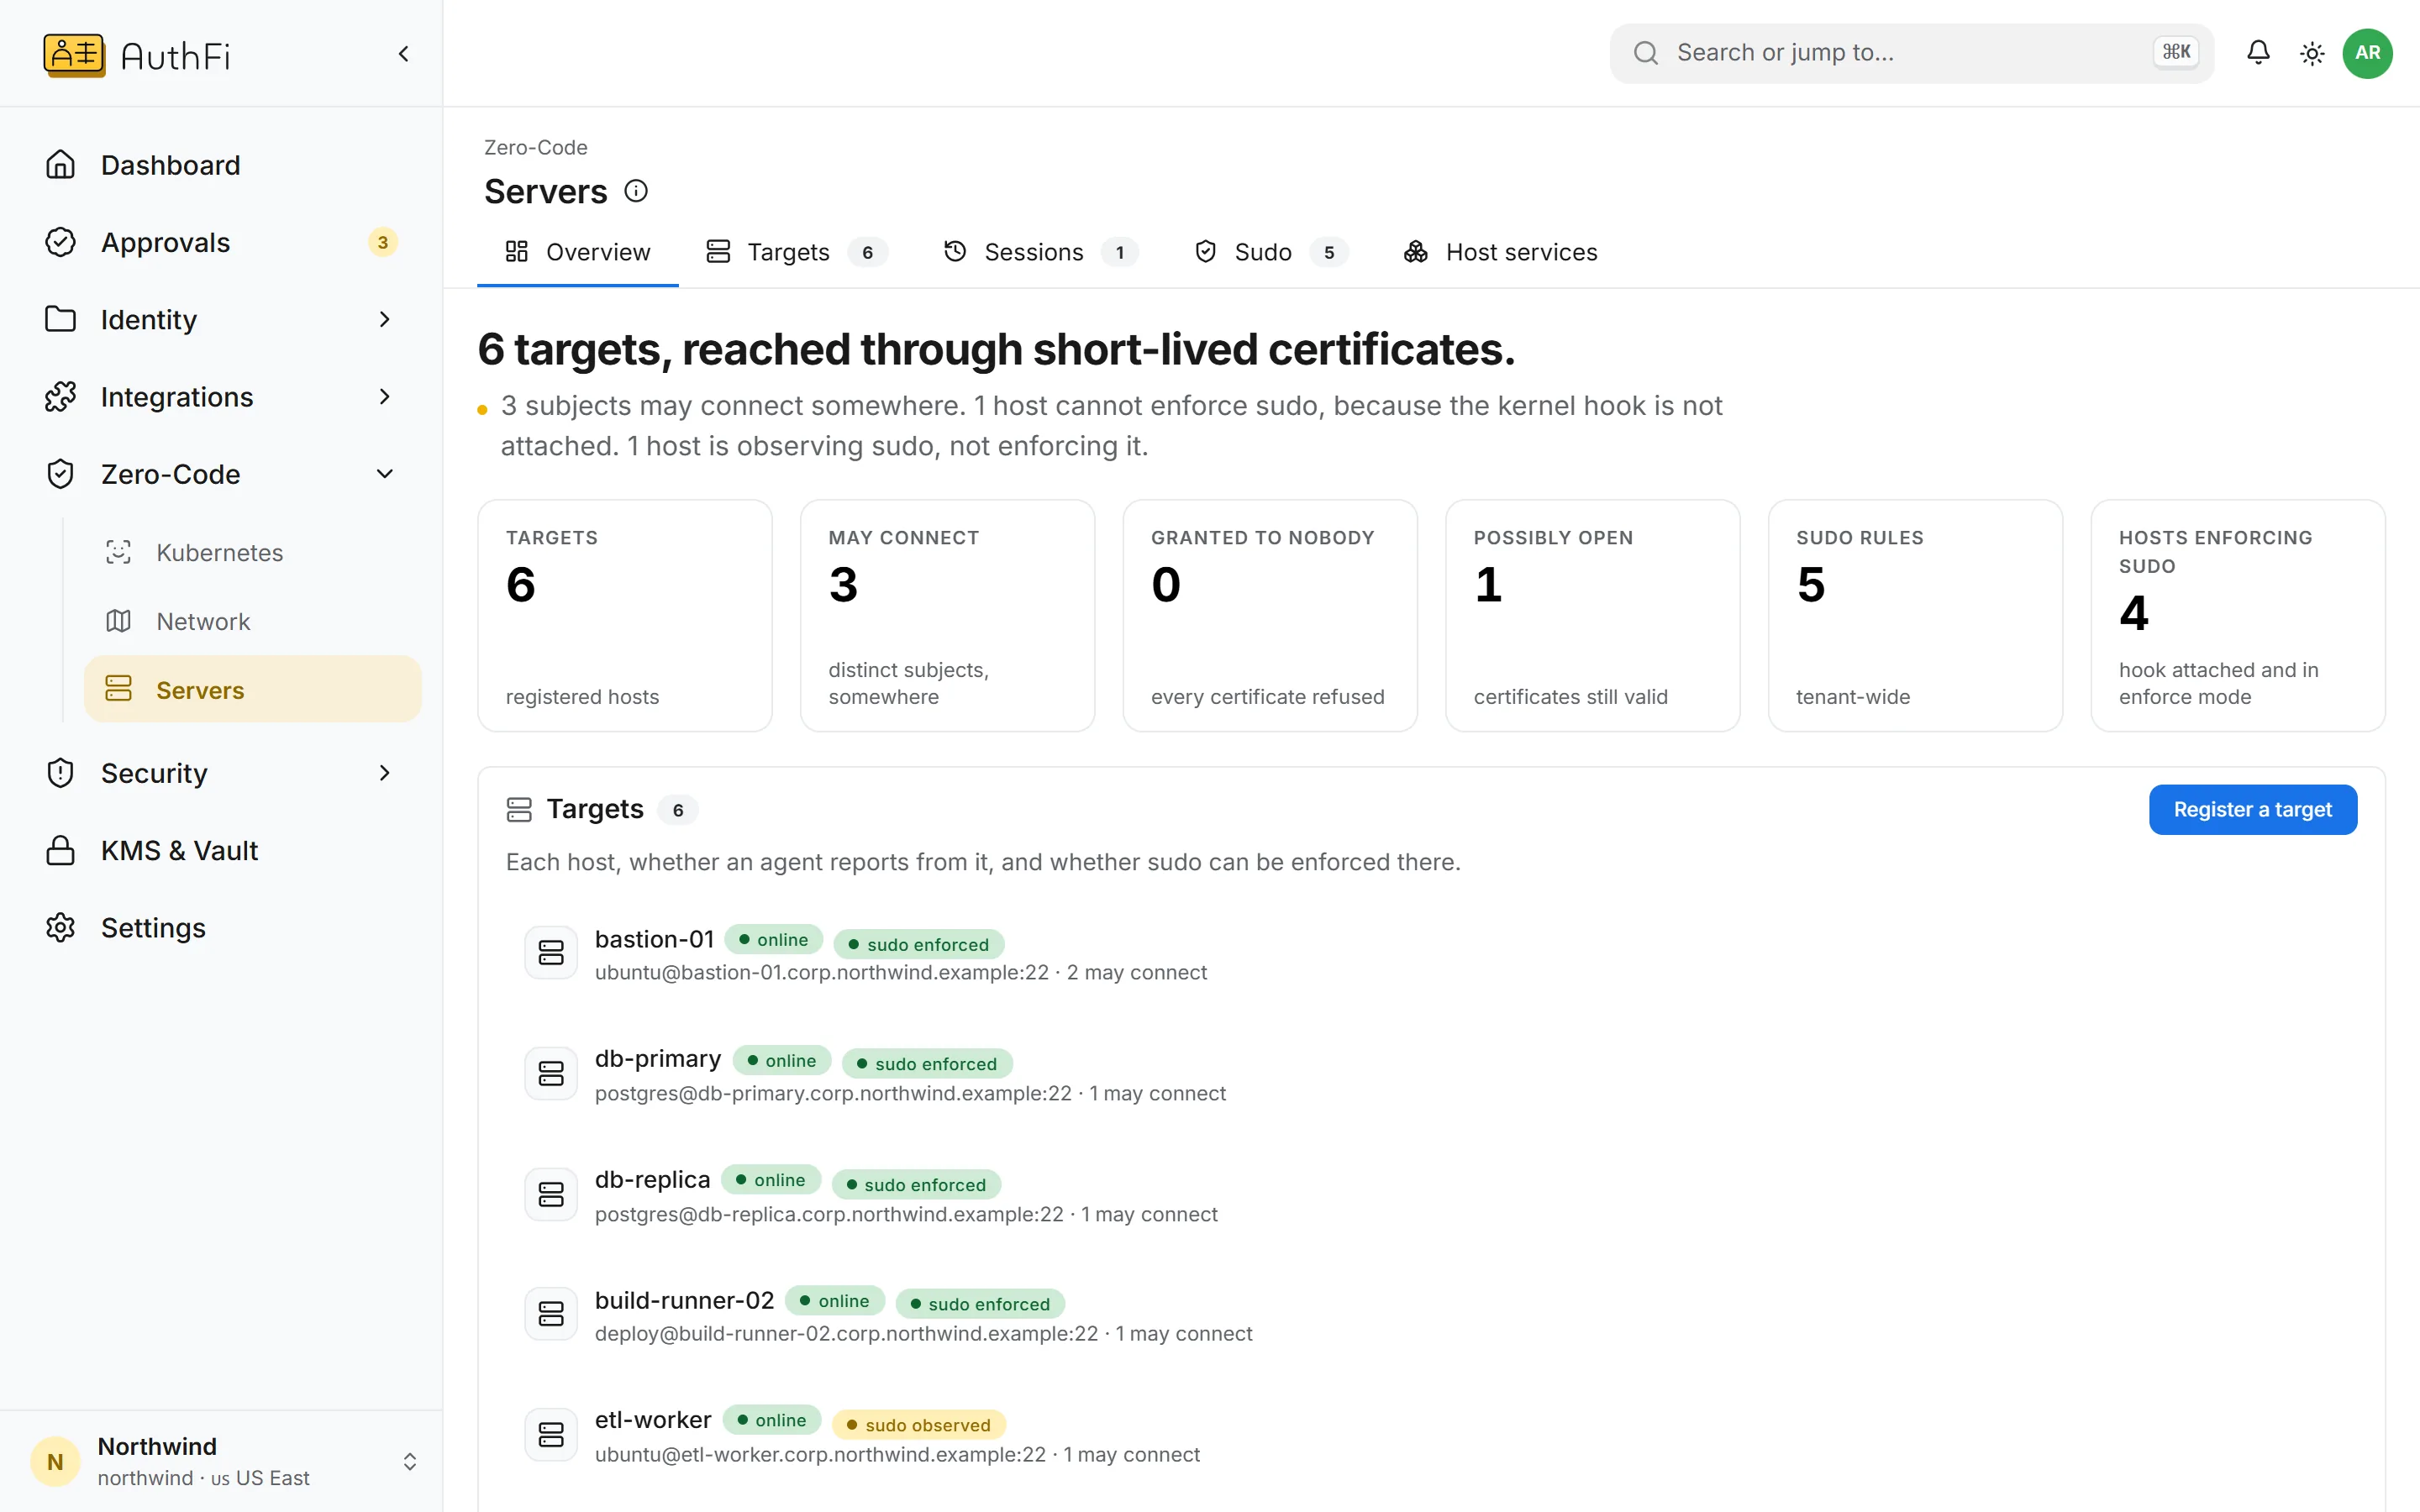
Servers without standing keys.
People sign in to a server with a certificate issued for that session. There is no key to leak and none to revoke.
Certificates that last five minutes
Access by group
Every session recorded as an event
Keyless roles on
Read on
Cloud roles are available for AWS and Google Cloud. Rules for privileged commands are in pilot.
Apps and cloud access
Clouds, servers and connections
OpenKeys and secrets
Signing keys and sealed secrets
OpenSecurity and audit
The record of who did what
OpenMore in Identity and access
Zero-Code: sign-in for services, with no code
Zero-Code puts sign-in and access rules in front of services you already run.
See howWorkforce identity: a modern IdP
Single sign-on, provisioning, passkeys and devices, on open standards, with users included in the plan.
See howSign-in for the product you sell
A hosted sign-in page under your brand, with organizations for your customers.
See how