Solution · AI enforcement
Control every tool your agents can call, from one MCP gateway.
Agents reach MCP tools through AuthFI. Each call is checked against what that agent was granted, and the tool's own credential never reaches the agent.
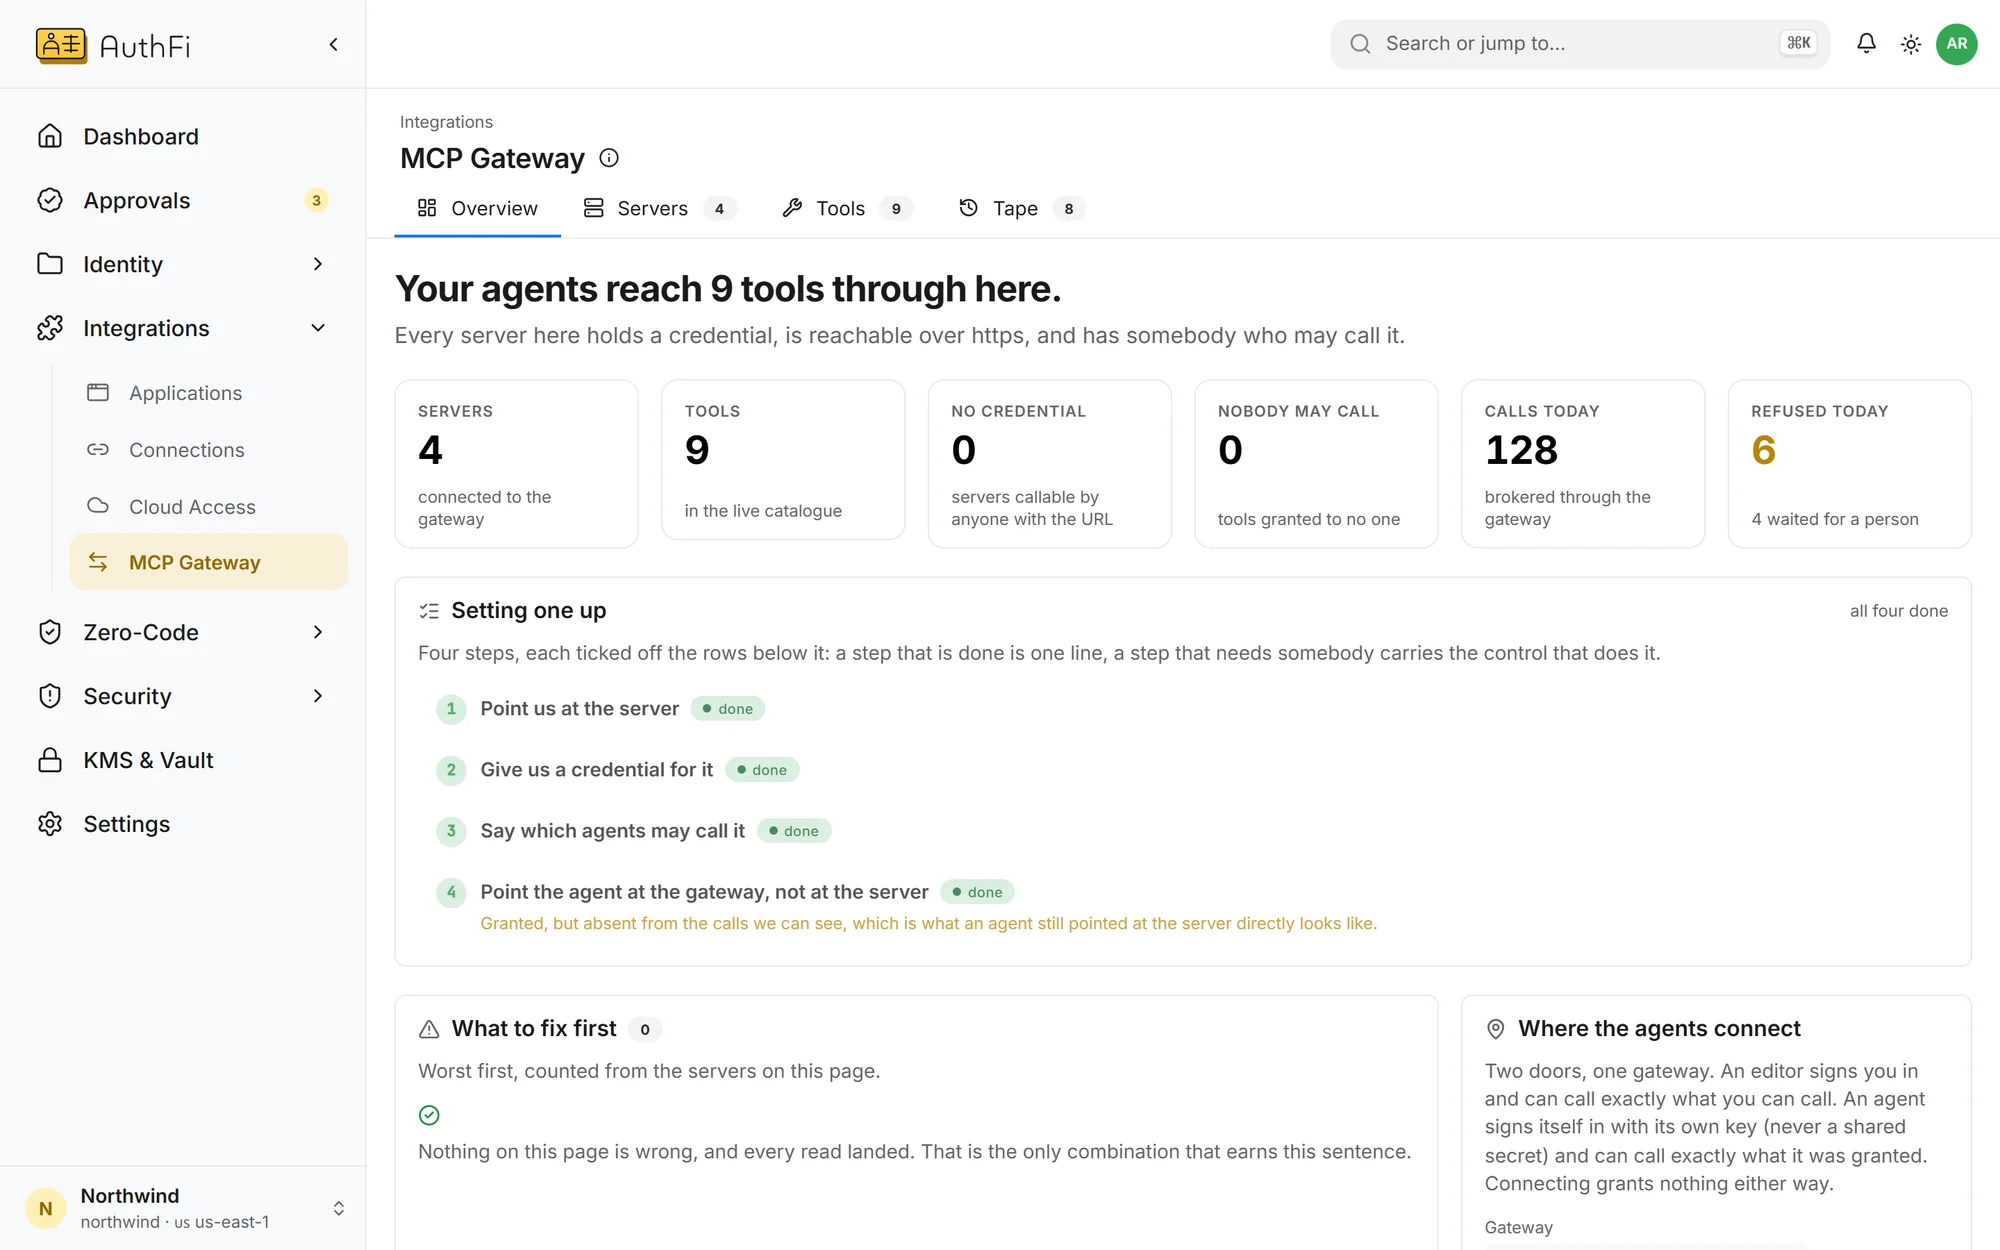
The MCP gateway
One address for every tool your agents use. Each call is checked with its arguments, and the tool’s own credential never leaves the gateway.
What changes
The problem as most companies have it today, and the same thing with AuthFI.
How it works
Each step, on the screen you would use.
Grants
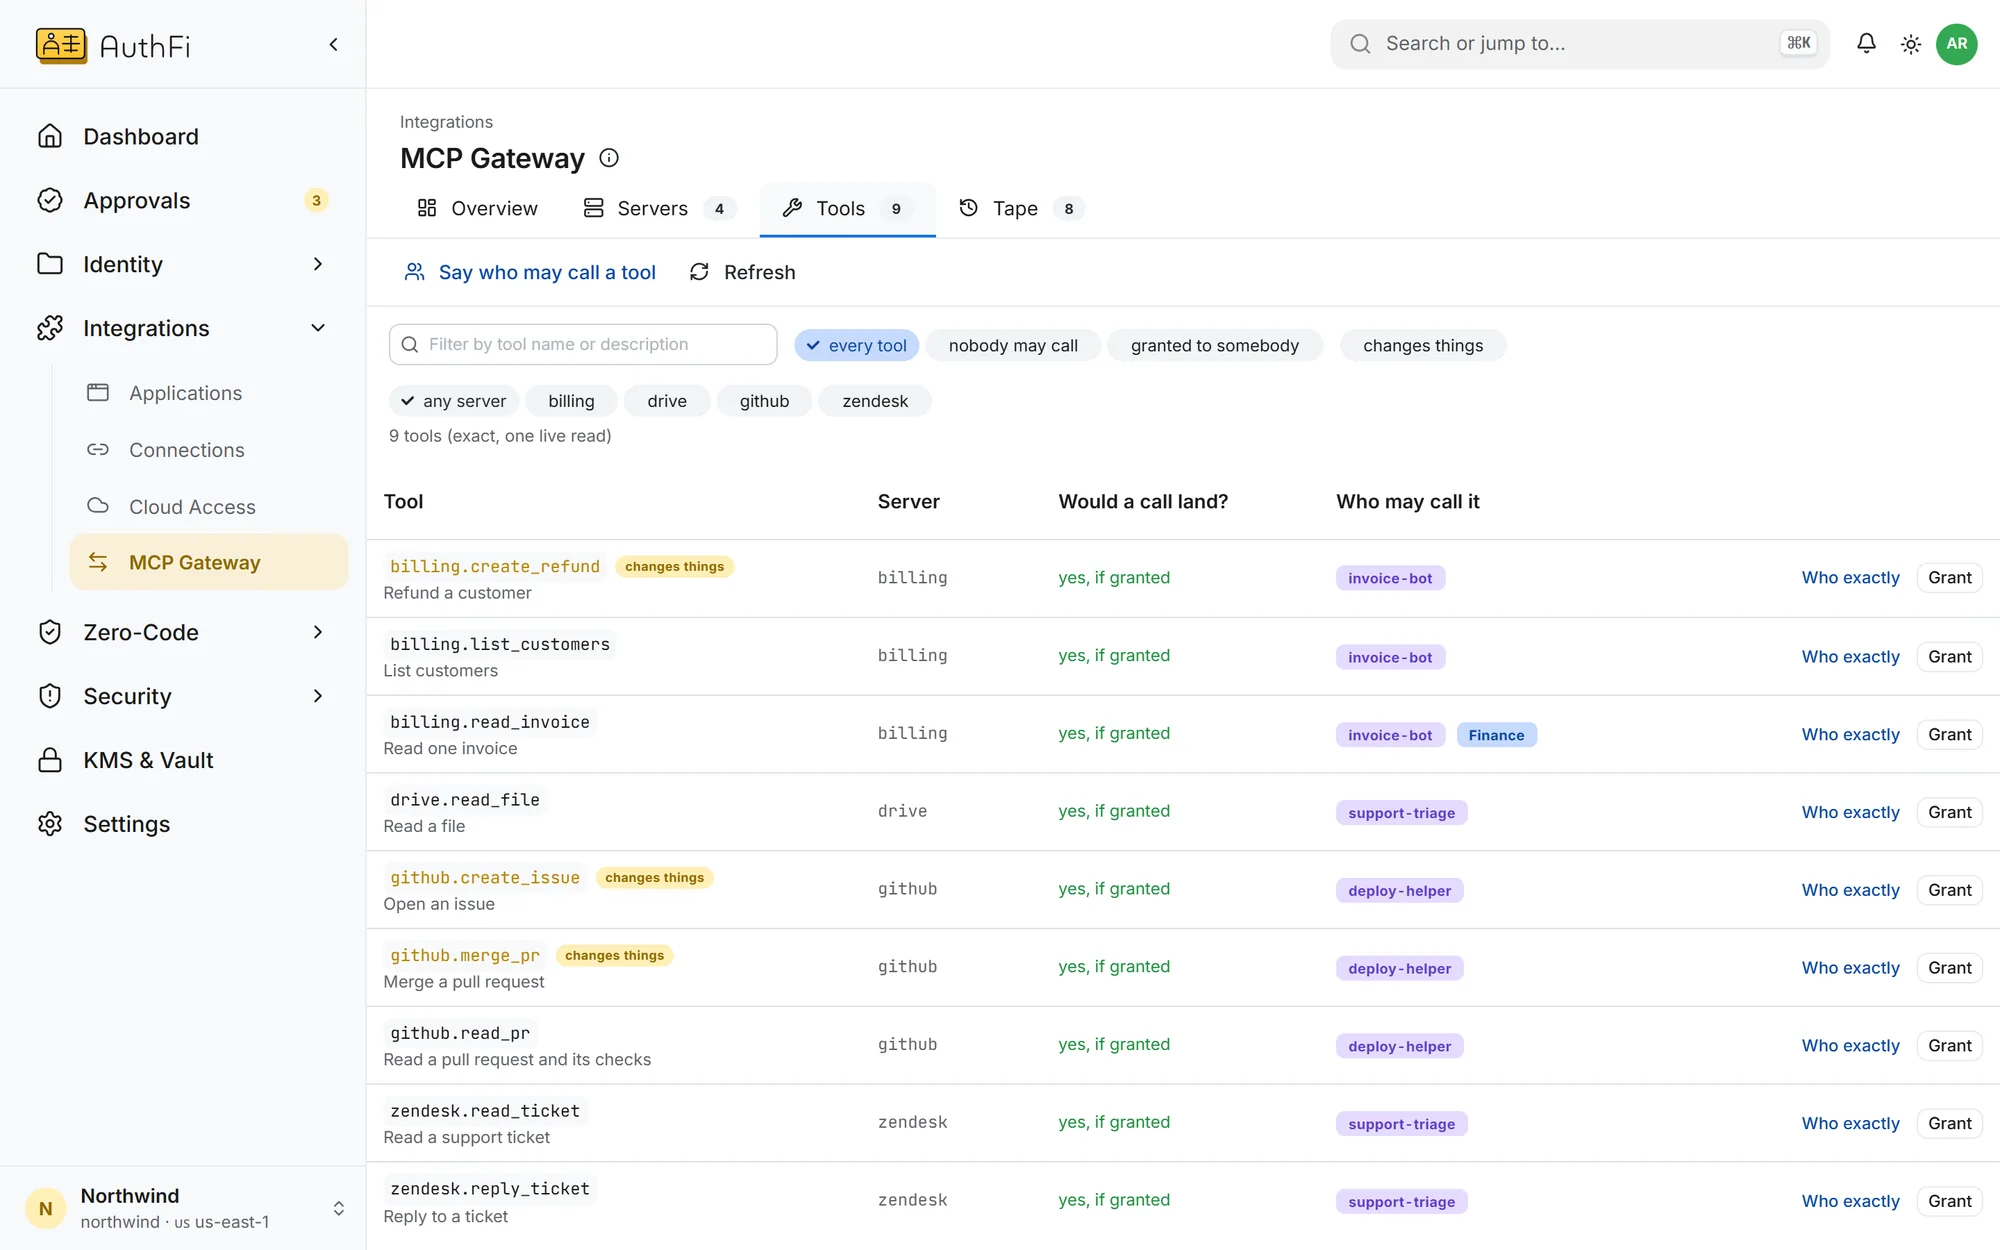
Grant tools one at a time.
Add a tool server once. Each tool is marked with what this agent may do, and a tool it was not granted is refused.
Per-tool, per-agent grants
Each listed tool says whether this agent may call it
Removing a grant takes effect on the next call
Record
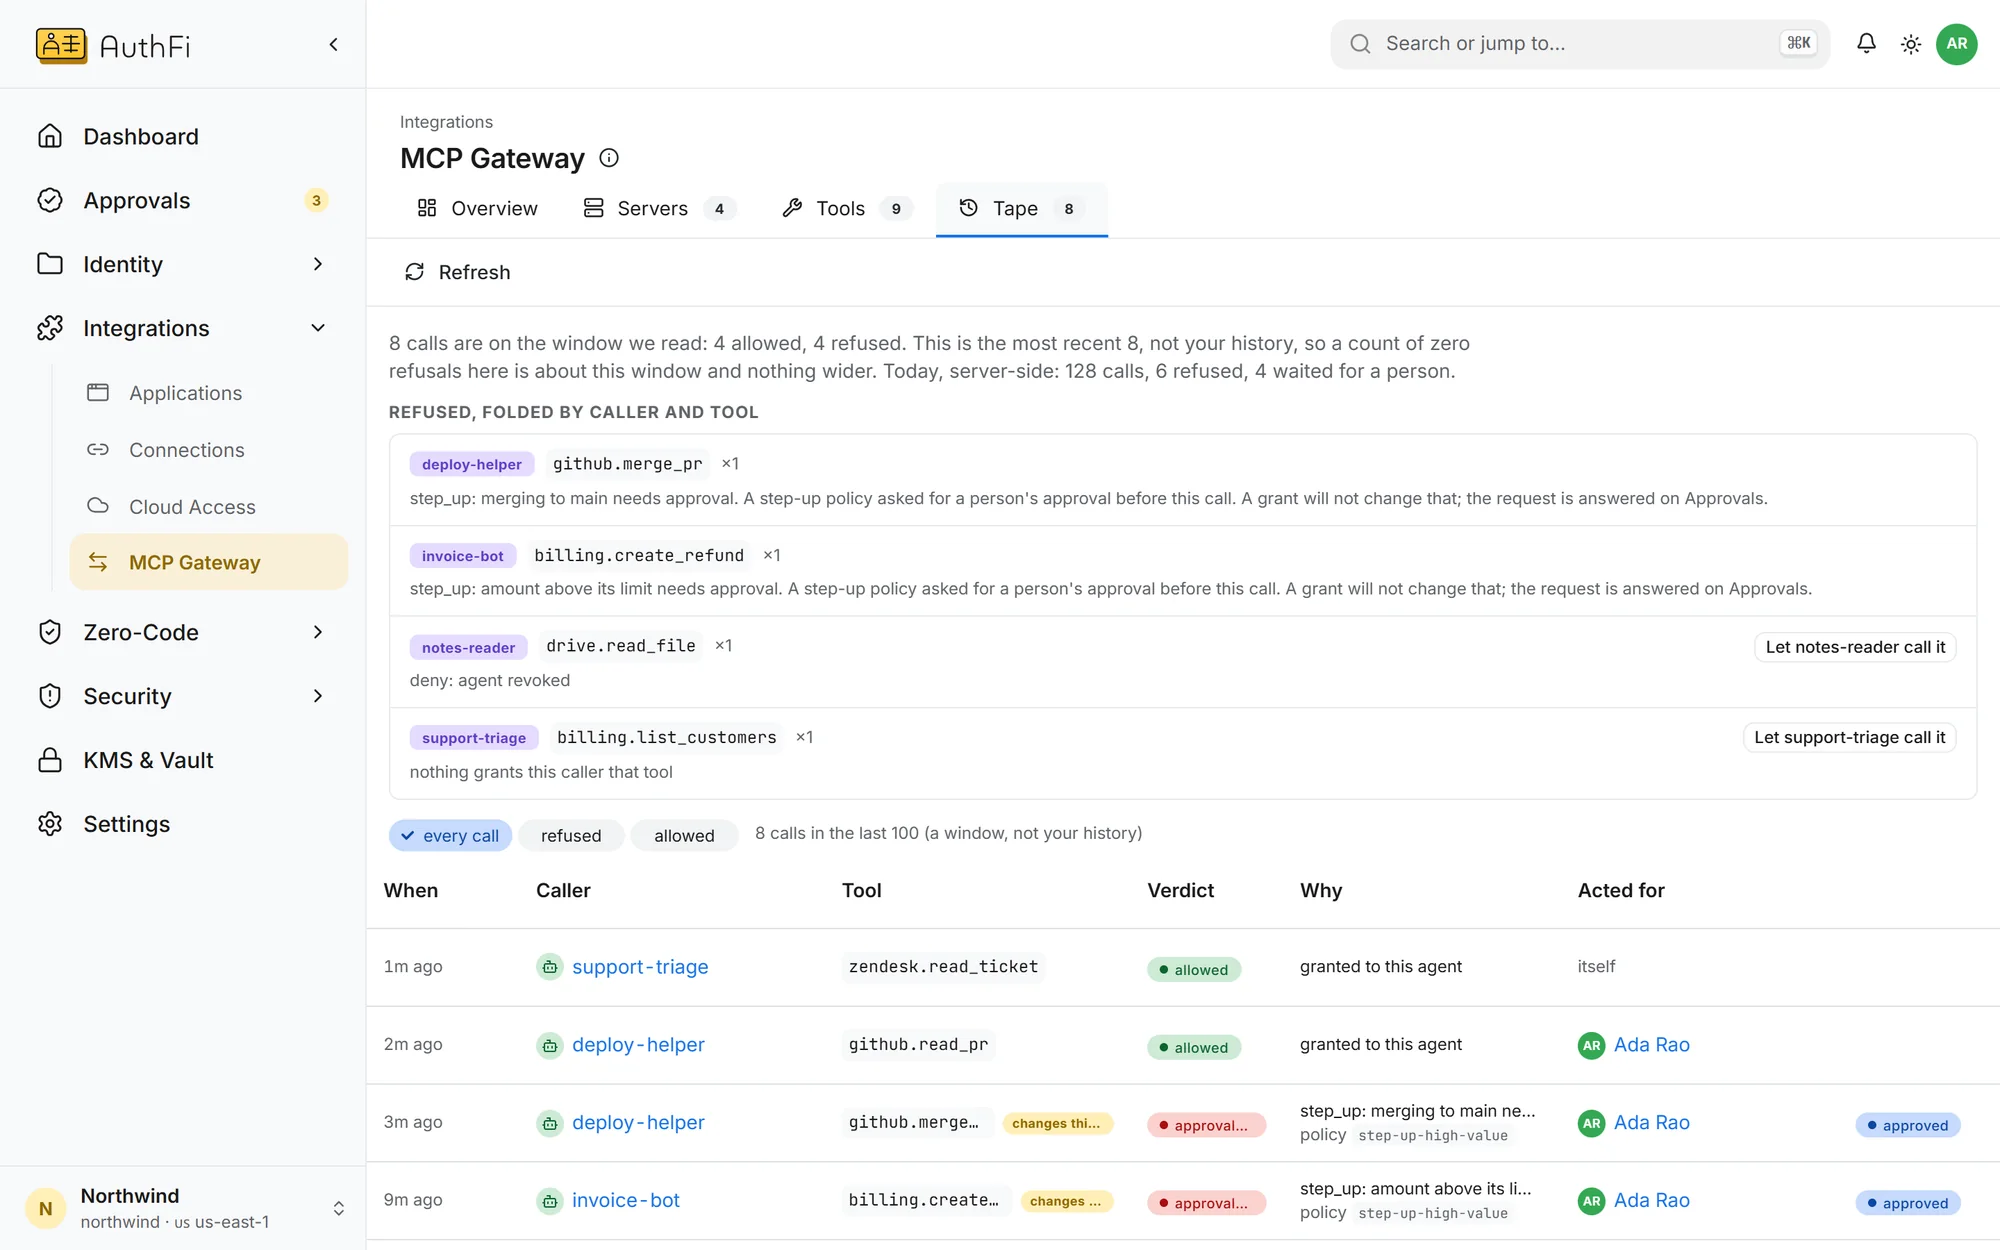
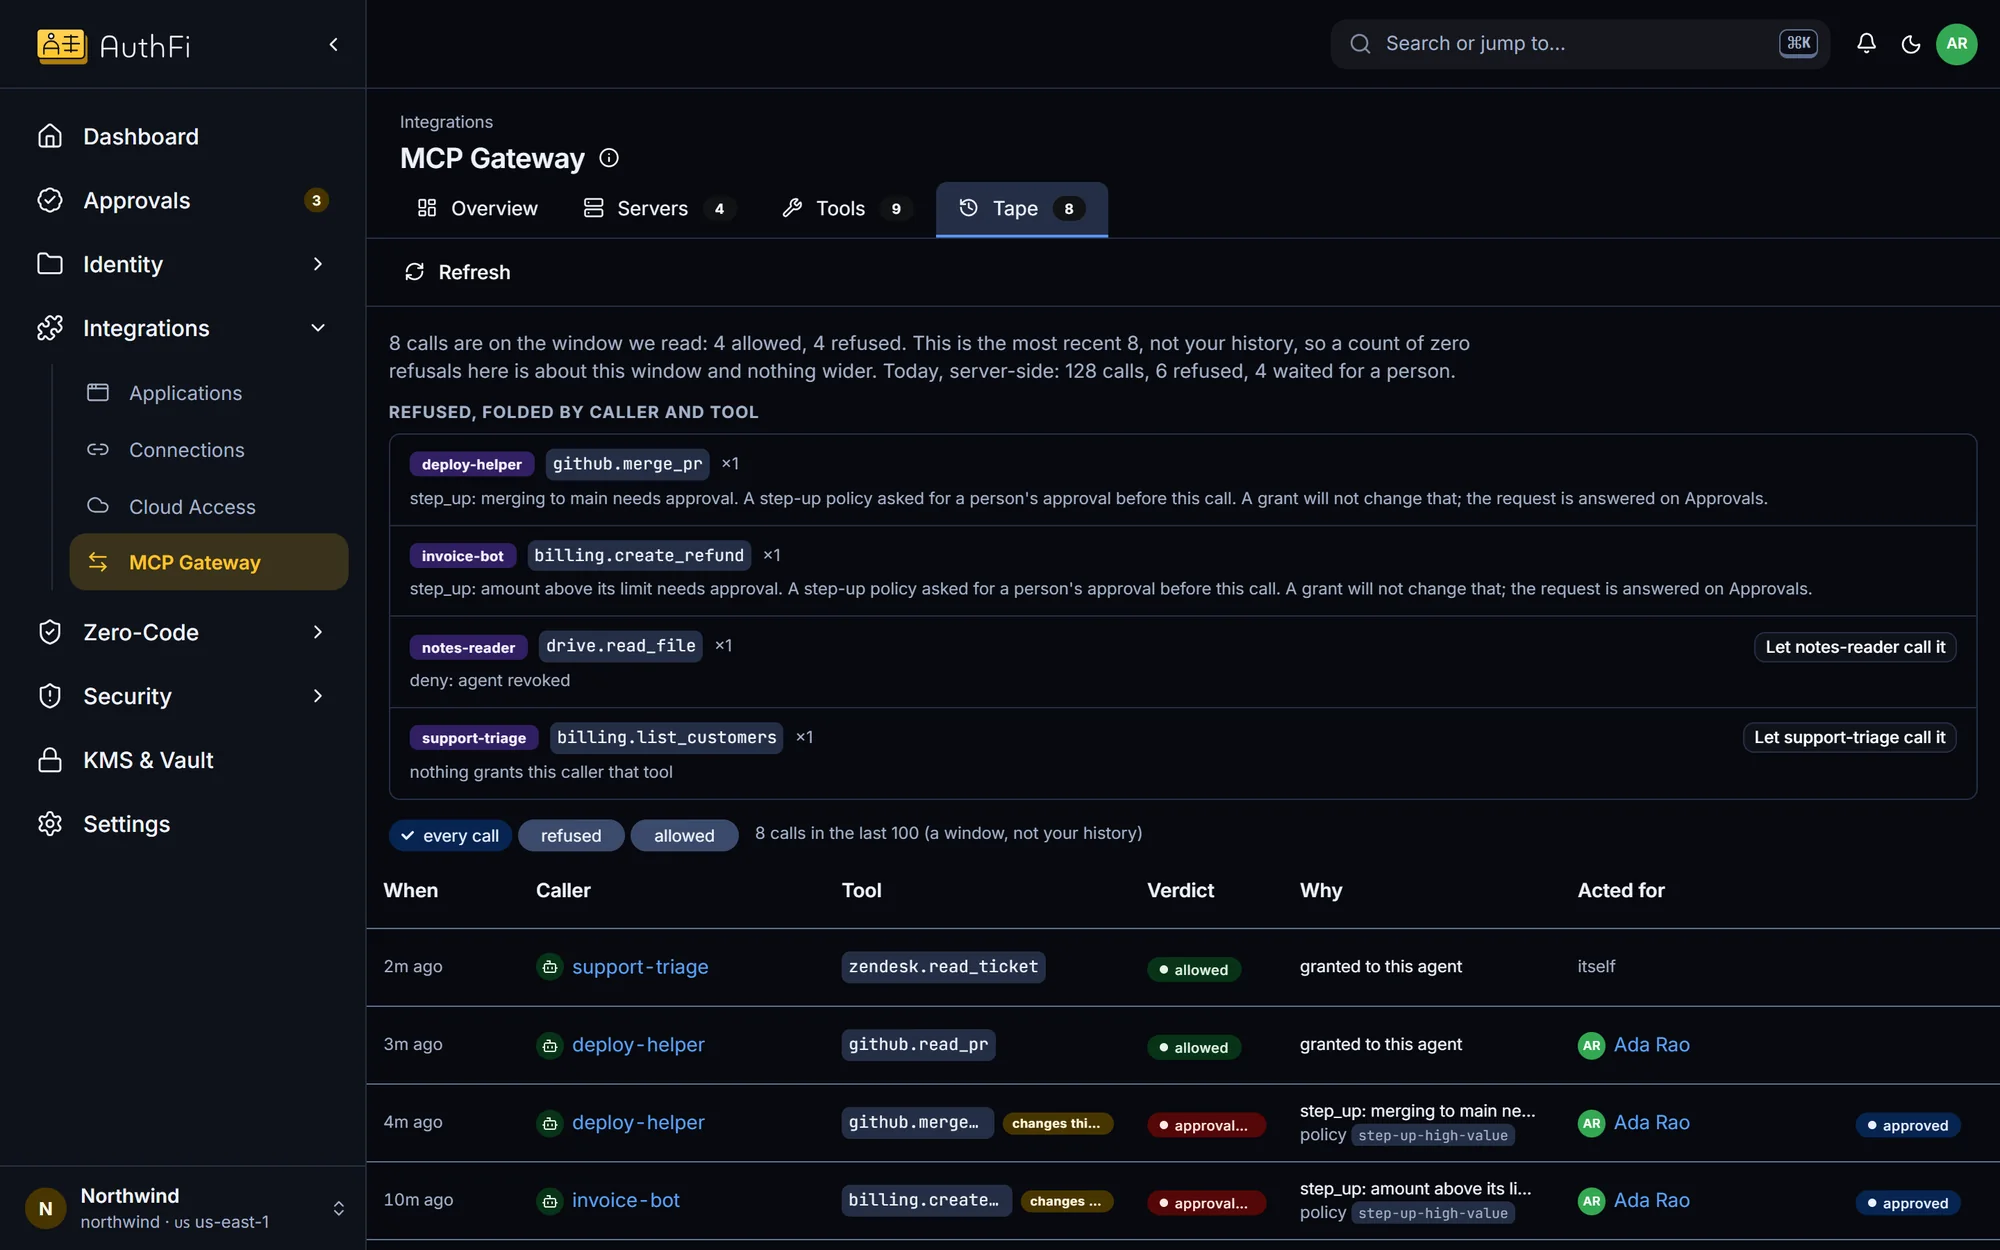
Every call, allowed or refused.
The gateway records who called which tool, with what result, and why a call was refused.
Allowed, refused, or waiting for a person
The reason for each refusal
Agents acting for a person show both names
Read on
The gateway accepts agent access tokens. An MCP client that can only sign a person in through a browser needs an agent identity in front of it.
Tool gateway quickstart
Call tools through the gateway
OpenAI Auth
The gateway in the whole picture
OpenAgent approvals
When a tool call needs a person
OpenMore in AI enforcement
AI Auth: govern AI agents in production
AI Auth gives every agent an identity, limits and an off switch, on open standards.
See howGive an agent a boundary it cannot leave
On the machine it runs on, an agent reaches only what you granted. Enforced in the kernel.
See howCIBA approvals: a person decides for the agent
Sensitive agent actions wait for a named person, out of band, over OpenID CIBA.
See how