Solution · Security
Show how your cluster stands, and close each gap.
Score a Kubernetes cluster against the frameworks you answer to, see exactly which workloads fail which control, and export the rule that fixes each as a Kyverno policy.
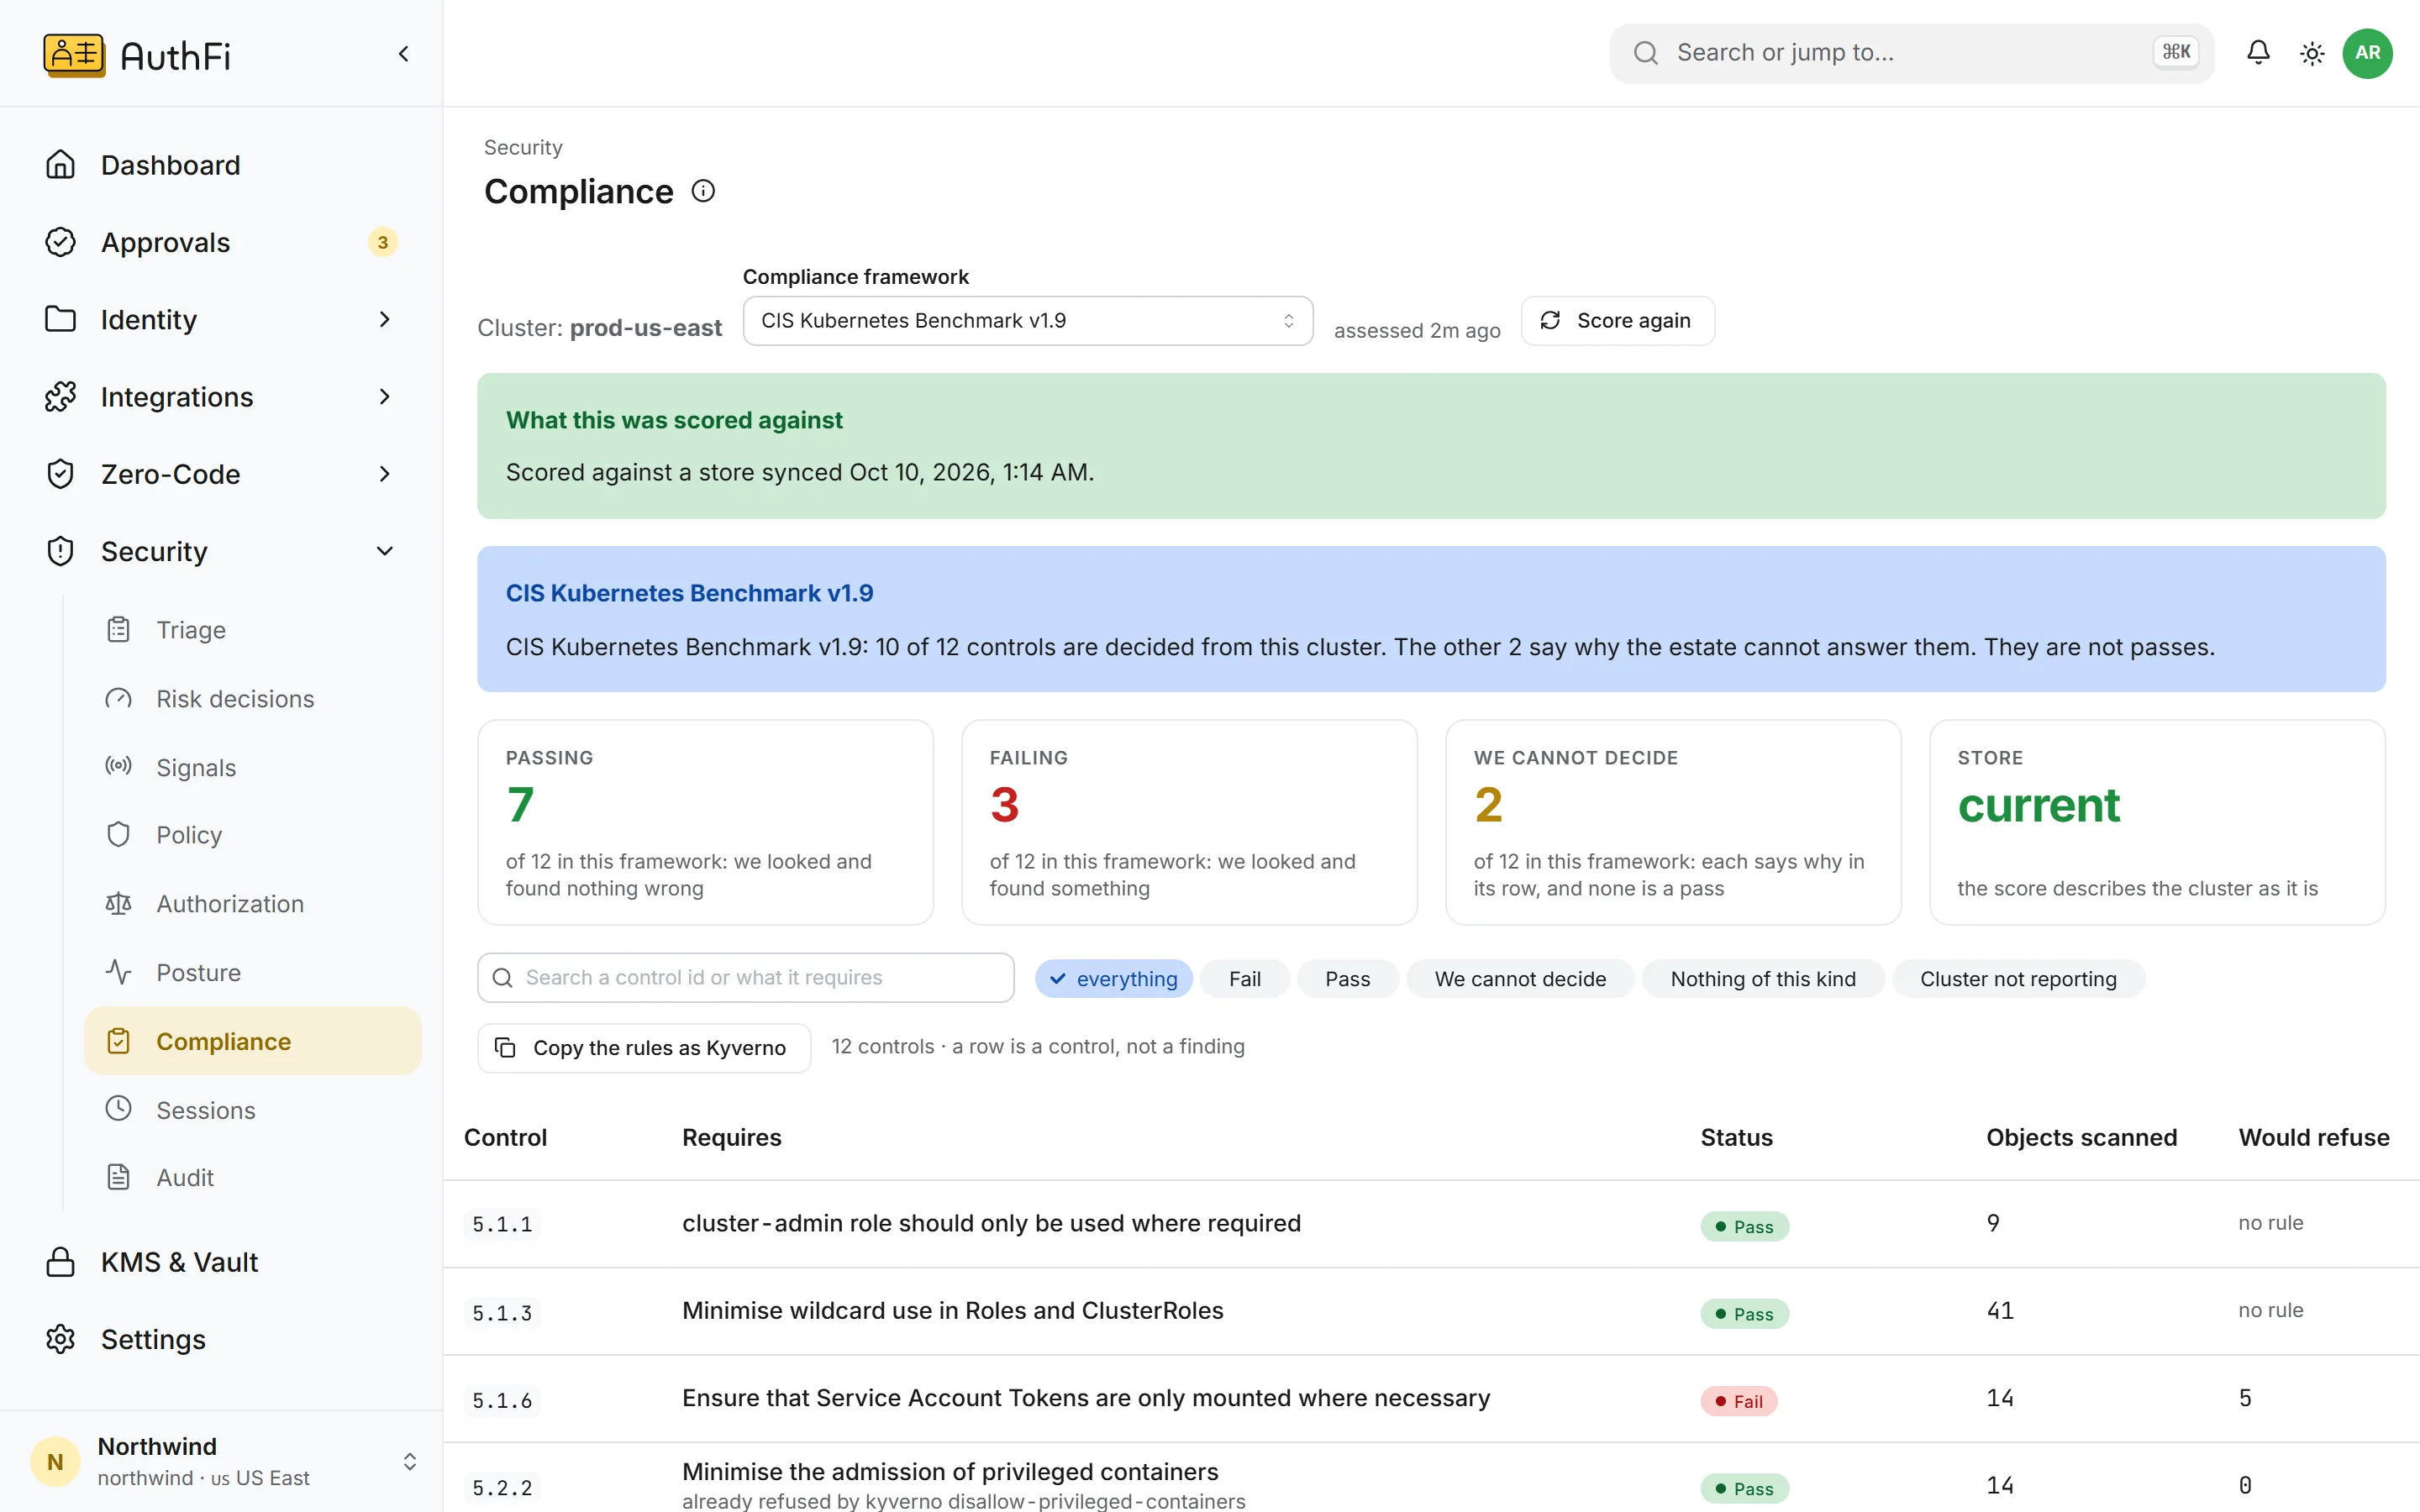
A cluster, scored
One cluster against a framework's controls. Only a pass is a pass; a control that cannot be decided says why.
What changes
The problem as most companies have it today, and the same thing with AuthFI.
How it works
Each step, on the screen you would use.
Score
Nine frameworks and AuthFI's AI baseline, one scan.
CIS Kubernetes Benchmark, SOC 2, ISO 27001, NIST 800-207, PCI DSS, HIPAA, three OWASP lists and AuthFI's AI baseline, scored from the objects in your cluster.
Each finding names the object and what failed
Objects scanned shown beside every answer
Says when the cluster's report is stale
Kyverno
Reads your Kyverno, and writes what is missing.
Controls your own Kyverno policies already refuse are marked as guarded. For the rest, copy a complete policy in Audit mode and enforce it when you are ready.
Audit mode is not counted as protection
Complete ClusterPolicy, ready to apply
Untranslated rules are named, not assumed
Read on
A score is evidence about your cluster's technical controls. It is not a certificate, and it does not replace an audit.
Policy and compliance
The frameworks, the answers and the limits
OpenRules in force
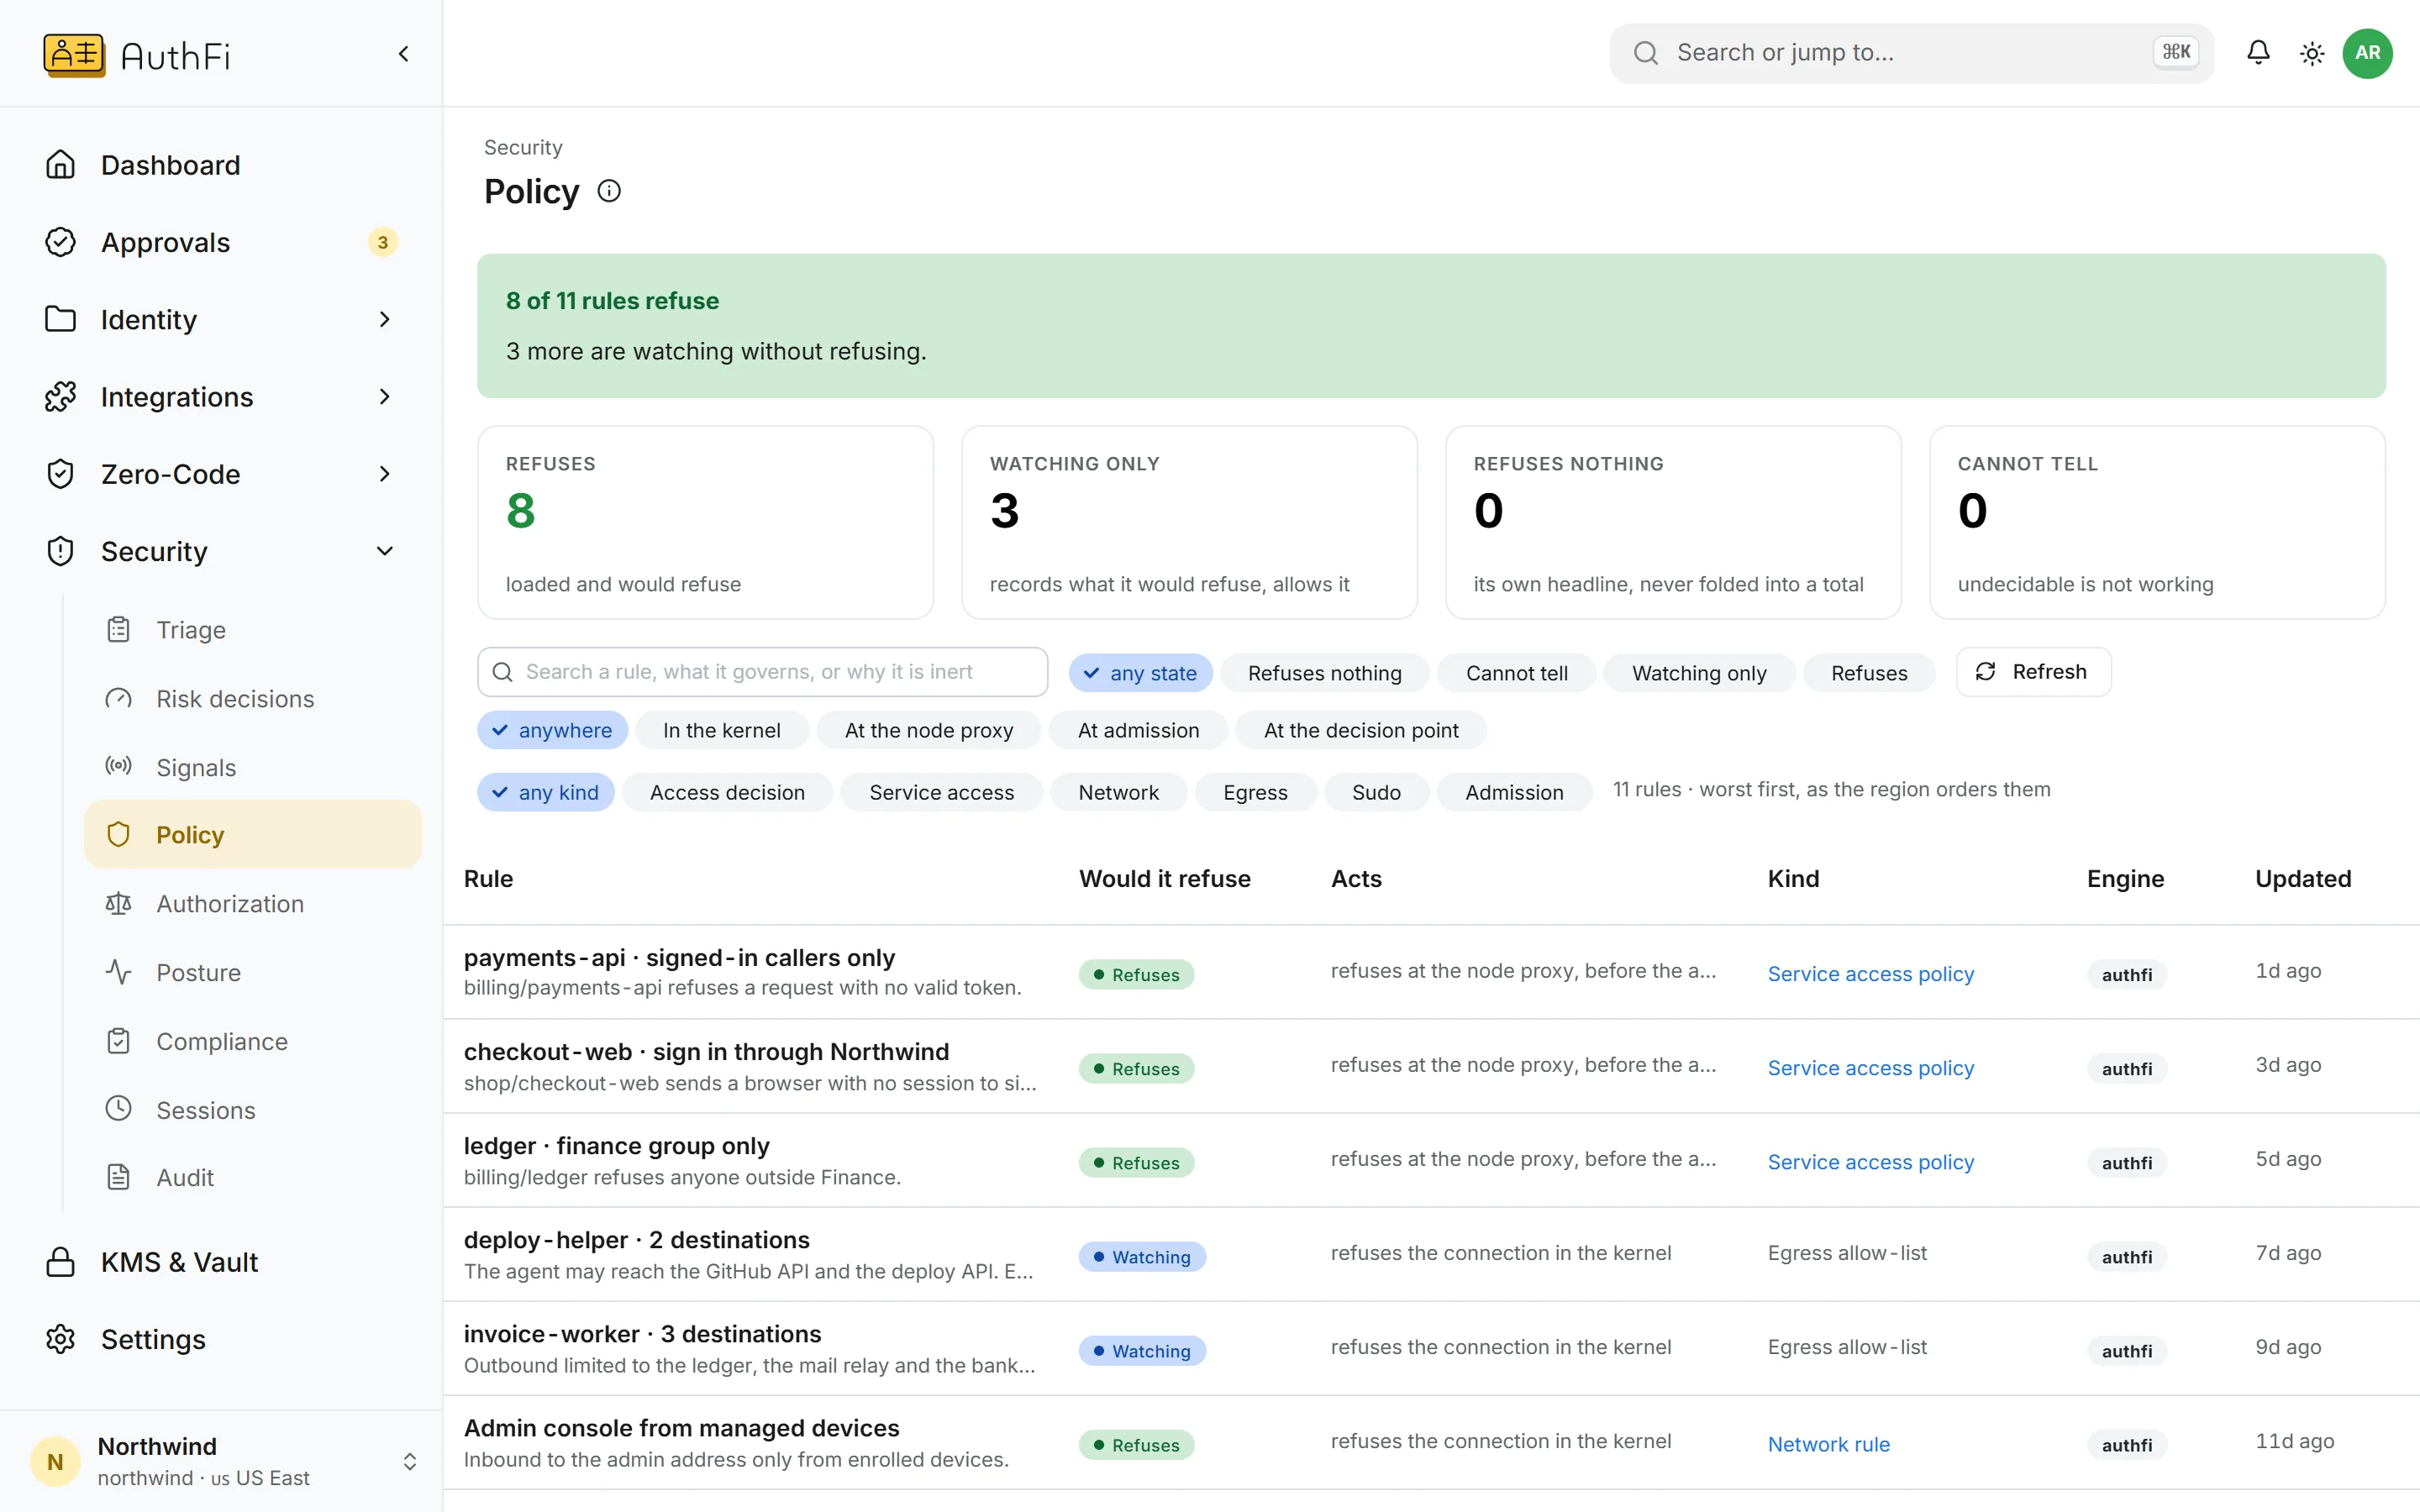
Which of your rules actually refuse
OpenFinancial services
What an auditor asks for
OpenMore in Security
One record of who did what
Every sign-in, grant, approval and refusal, for people and agents, on one chained record.
See howKnow which of your rules actually refuse
Every rule on the platform, and whether it refuses, only watches, or cannot bite.
See howProtect every account from takeover
Passkeys, a second step on every plan, lockout, breached-password checks and sessions you can end.
See how