Solution · Identity and access
Sign-in for the product you sell, under your own brand.
Give your customers a sign-in page that is yours, and model each business you sell to, without building or maintaining any of it.
Northwind’s sign-in page, not ours
Their logo, colour, headline and domain. Nothing on the page says AuthFI. This is the real hosted sign-in page, running on example data.
Type any email address and press Continue. Or press Create an account.
What changes
The problem as most companies have it today, and the same thing with AuthFI.
How it works
Each step, on the screen you would use.
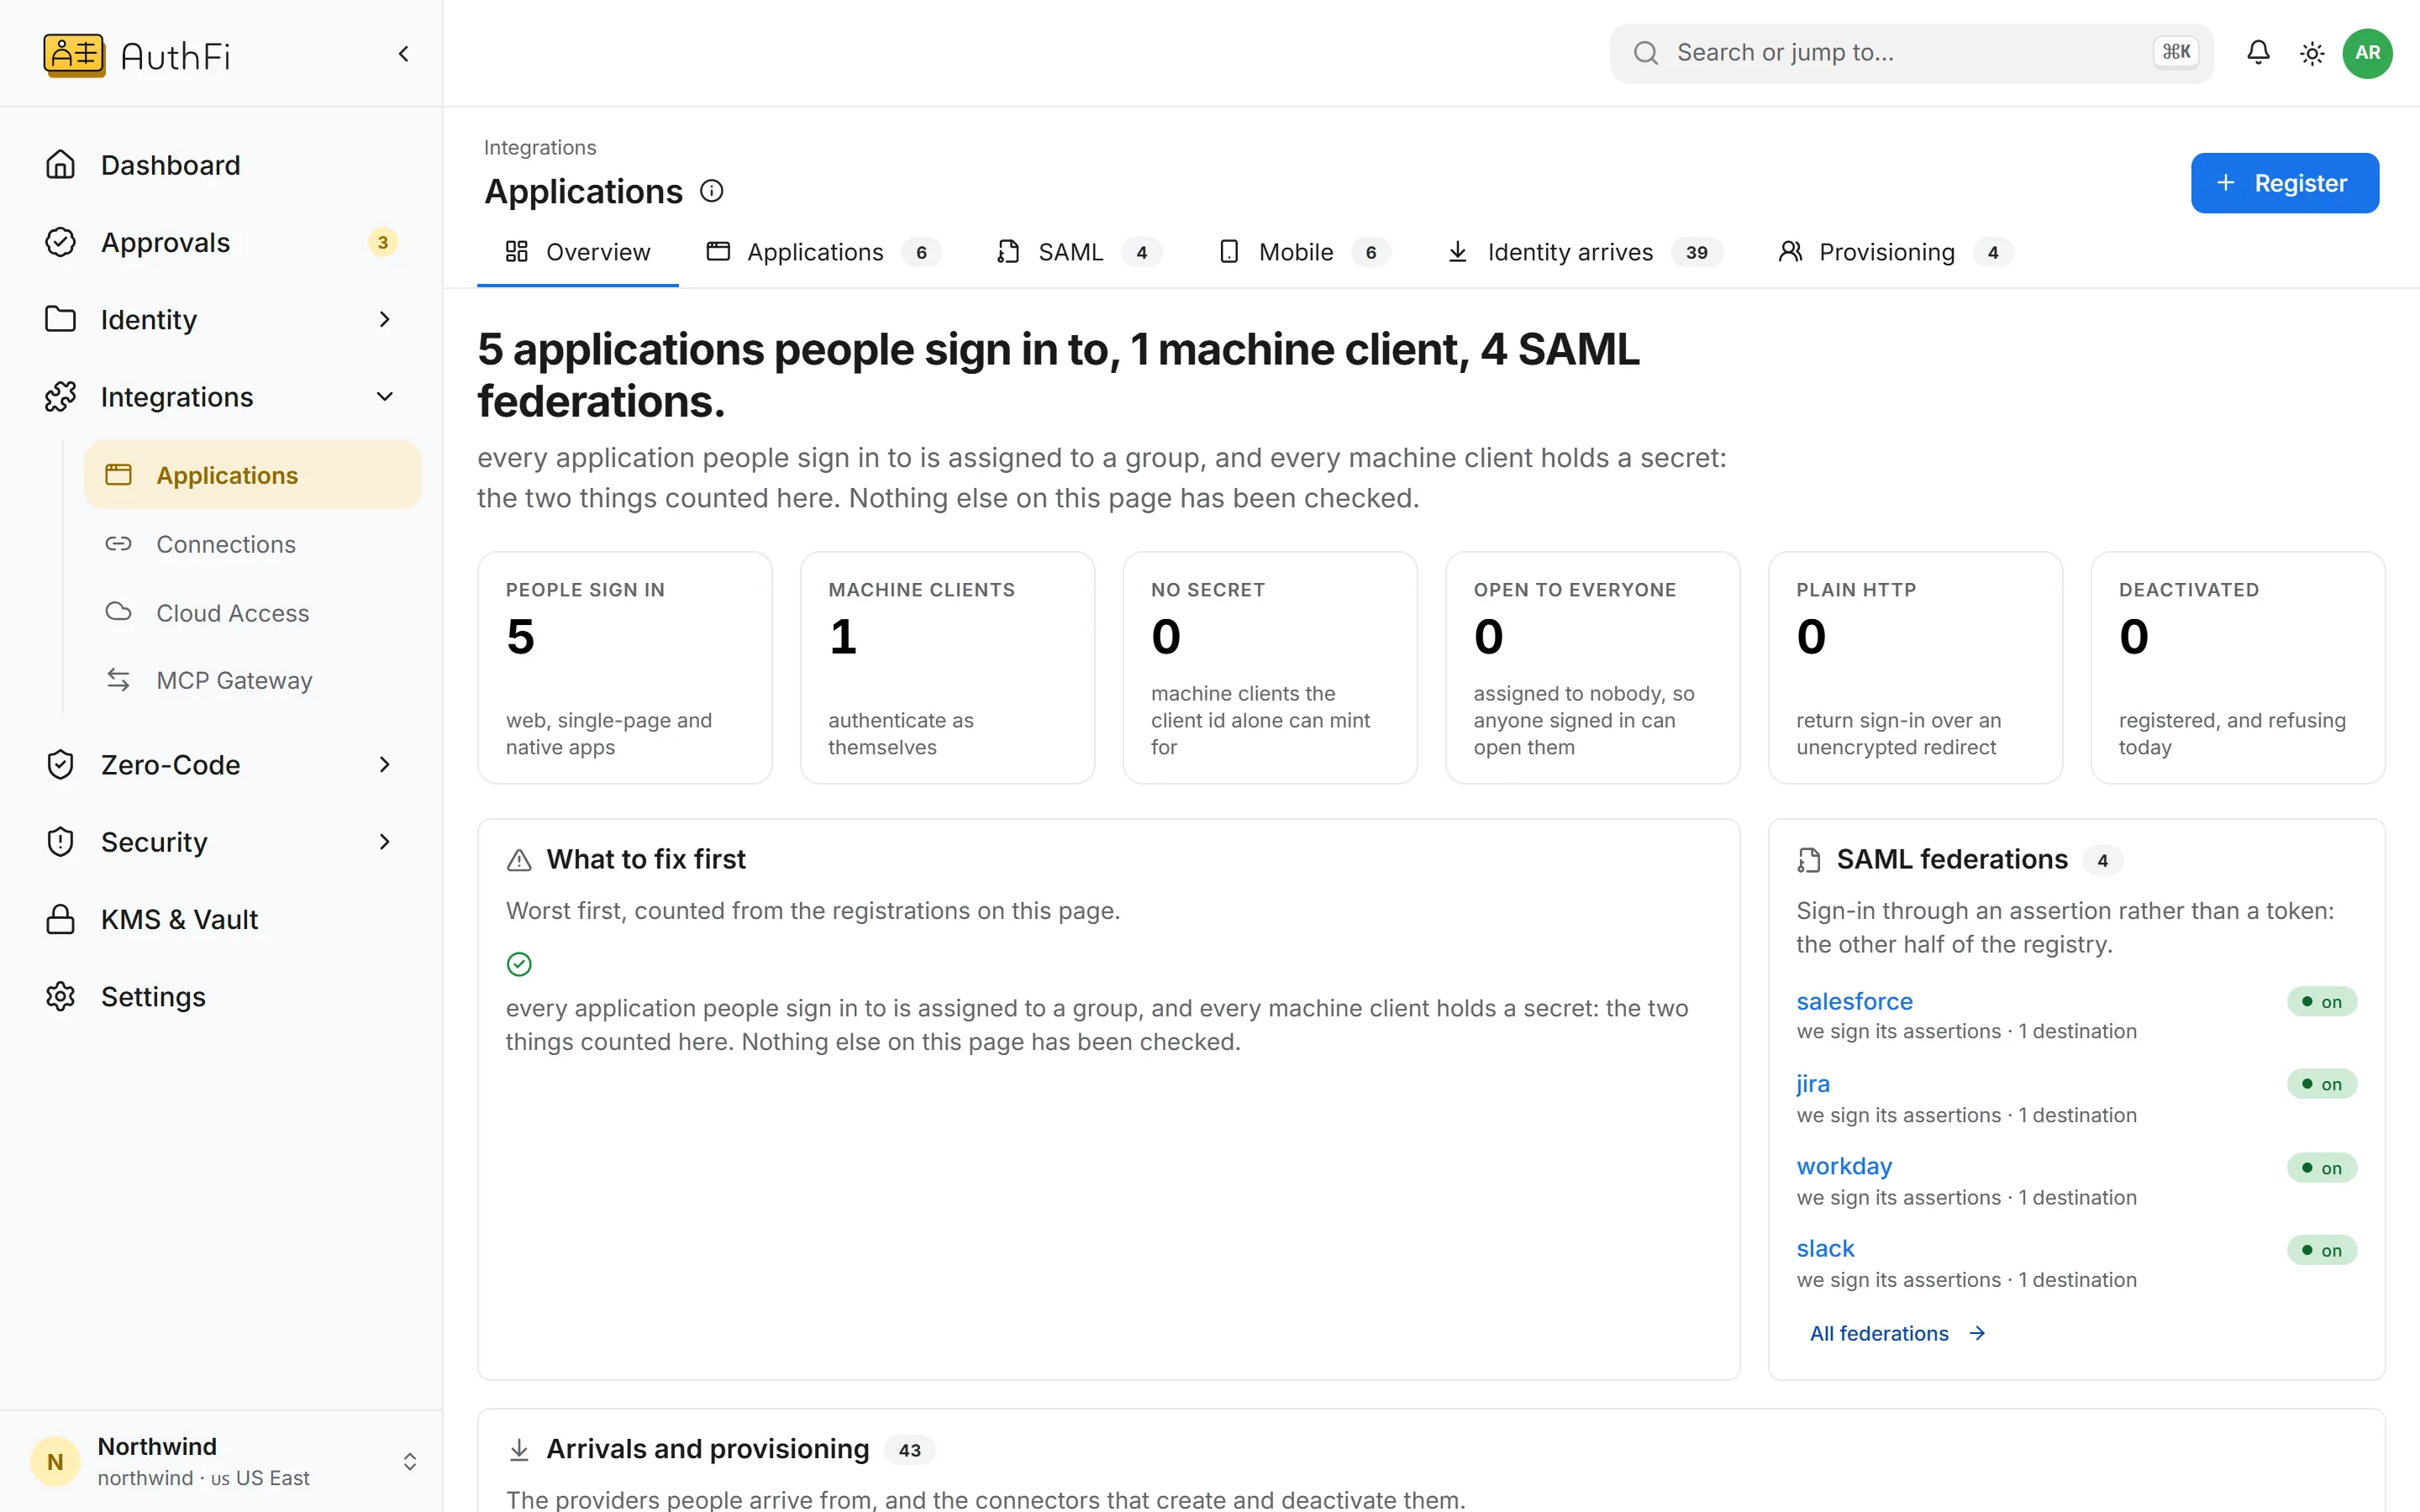
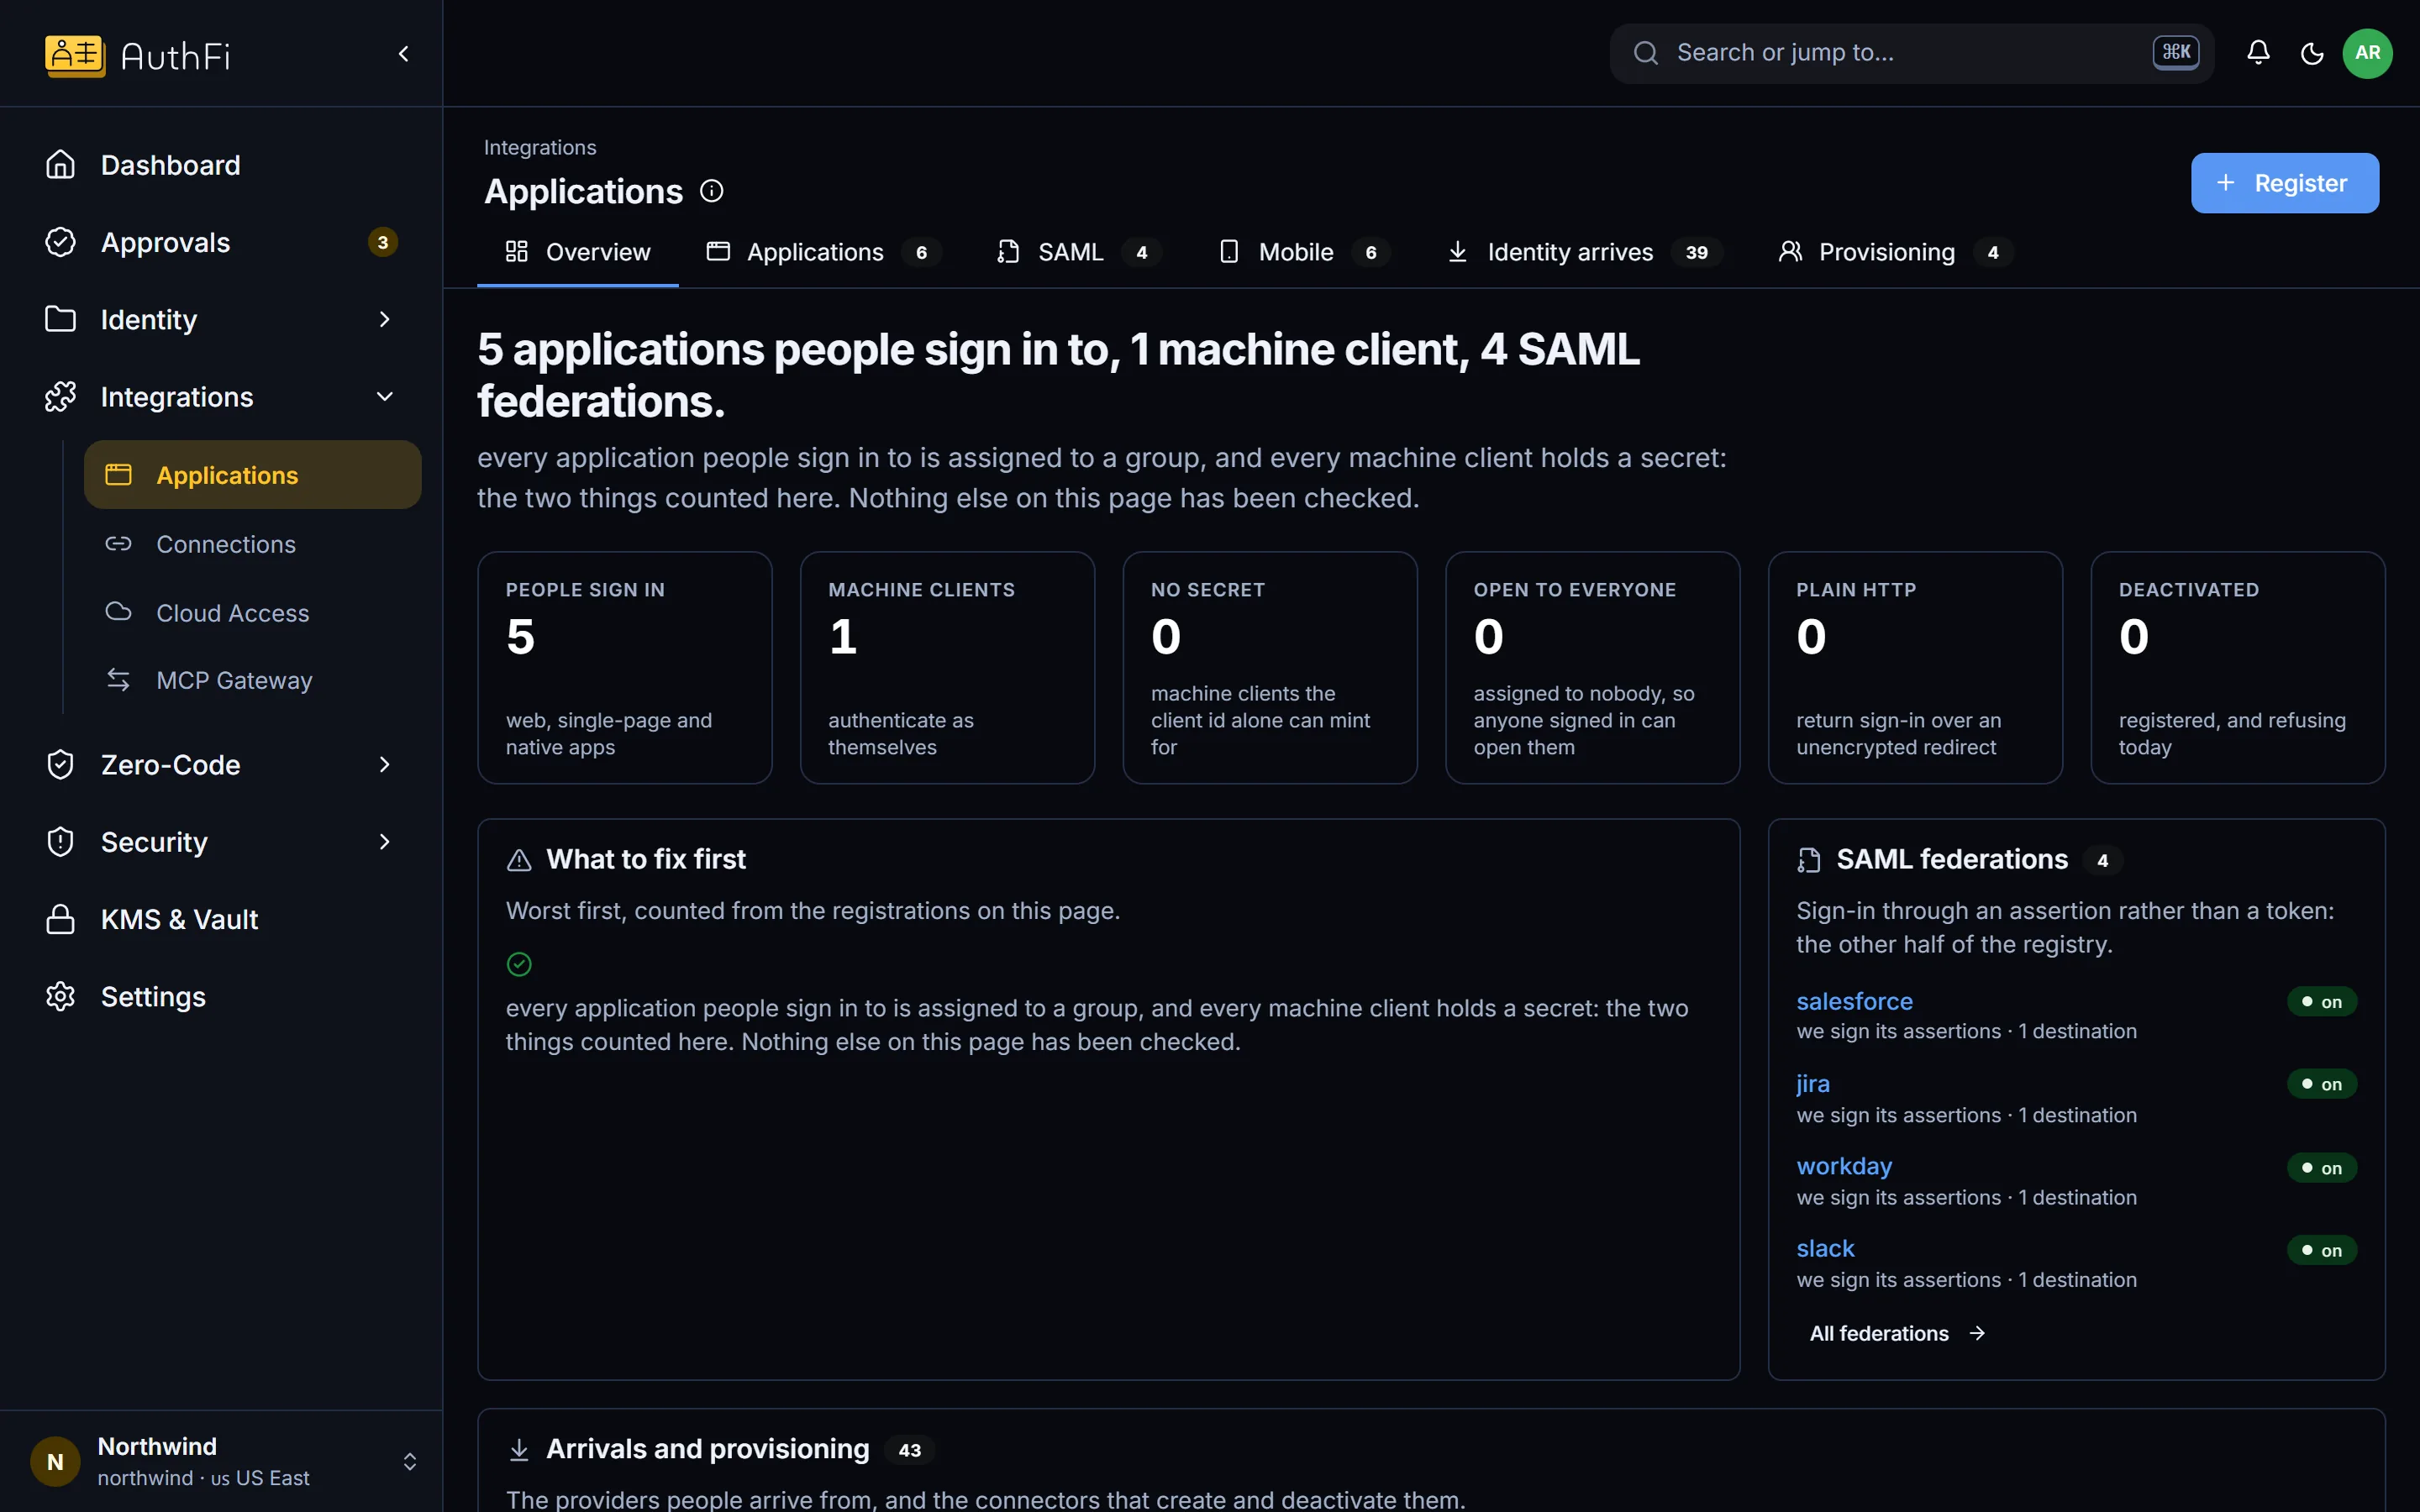
Applications
Standard sign-in for every app.
Register each of your applications and it signs people in with OpenID Connect. Any standard library works.
Authorization code flow with PKCE
Passkeys, a second step, email codes
Groups and roles in the token
Organizations
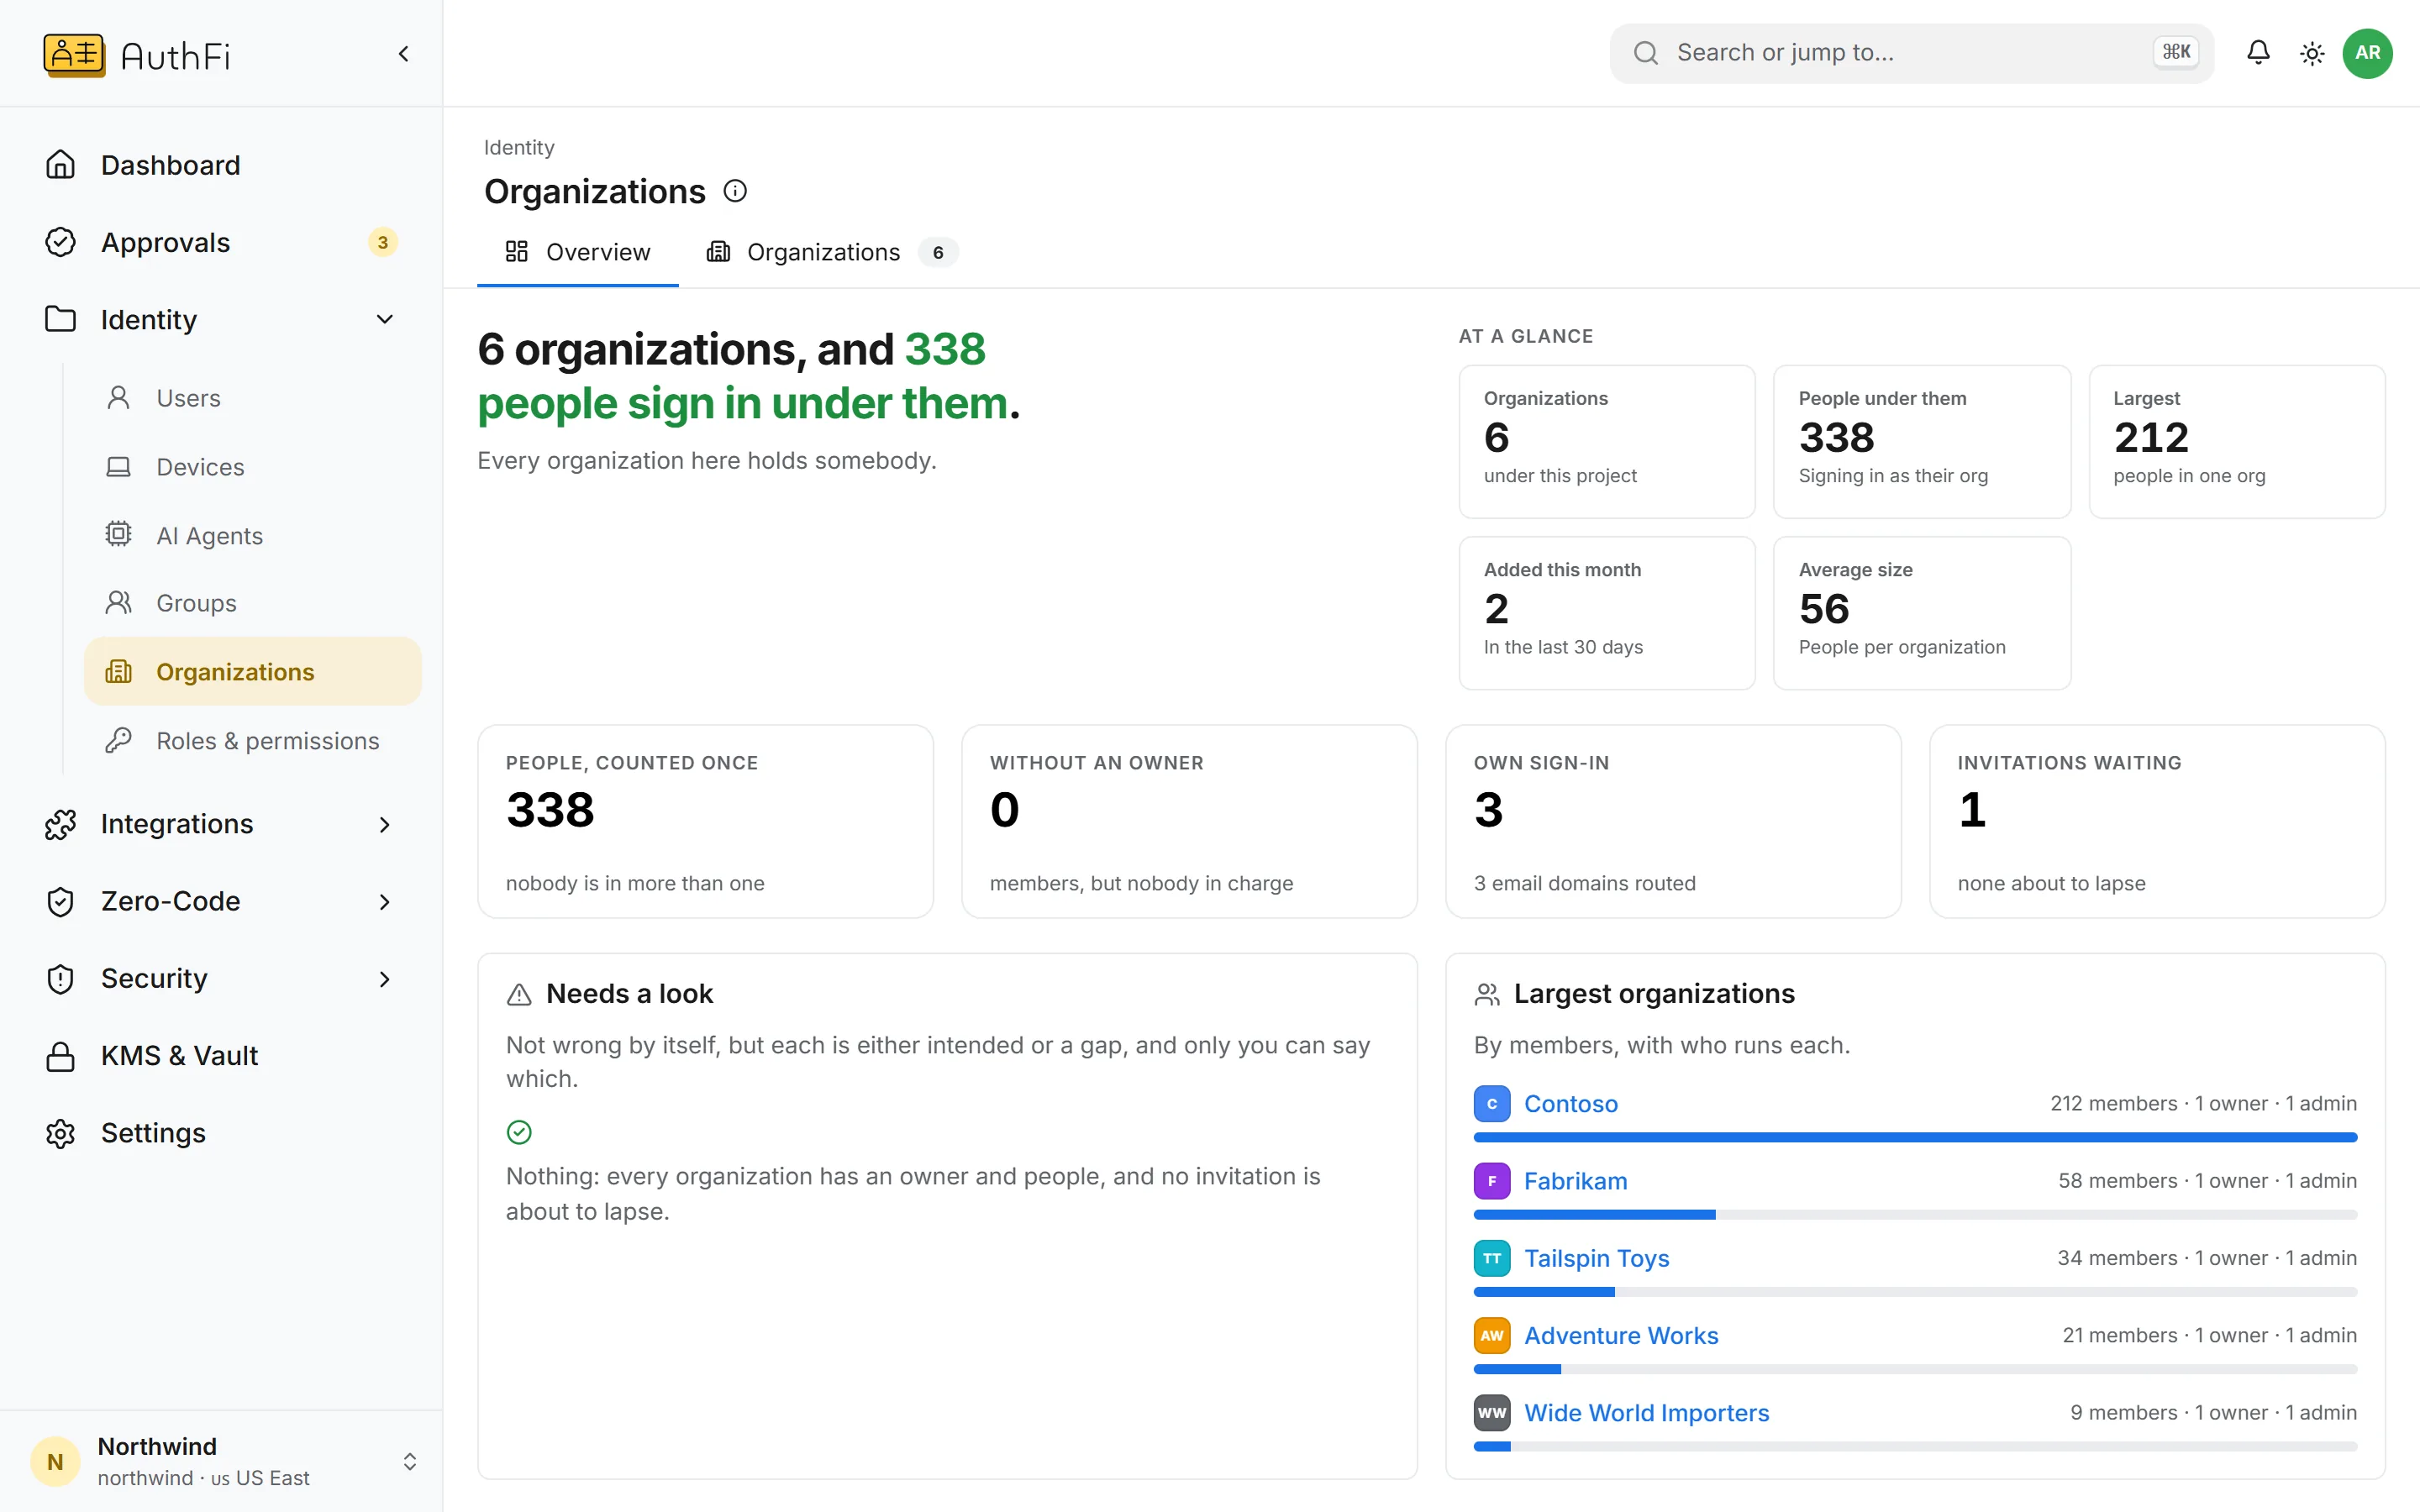
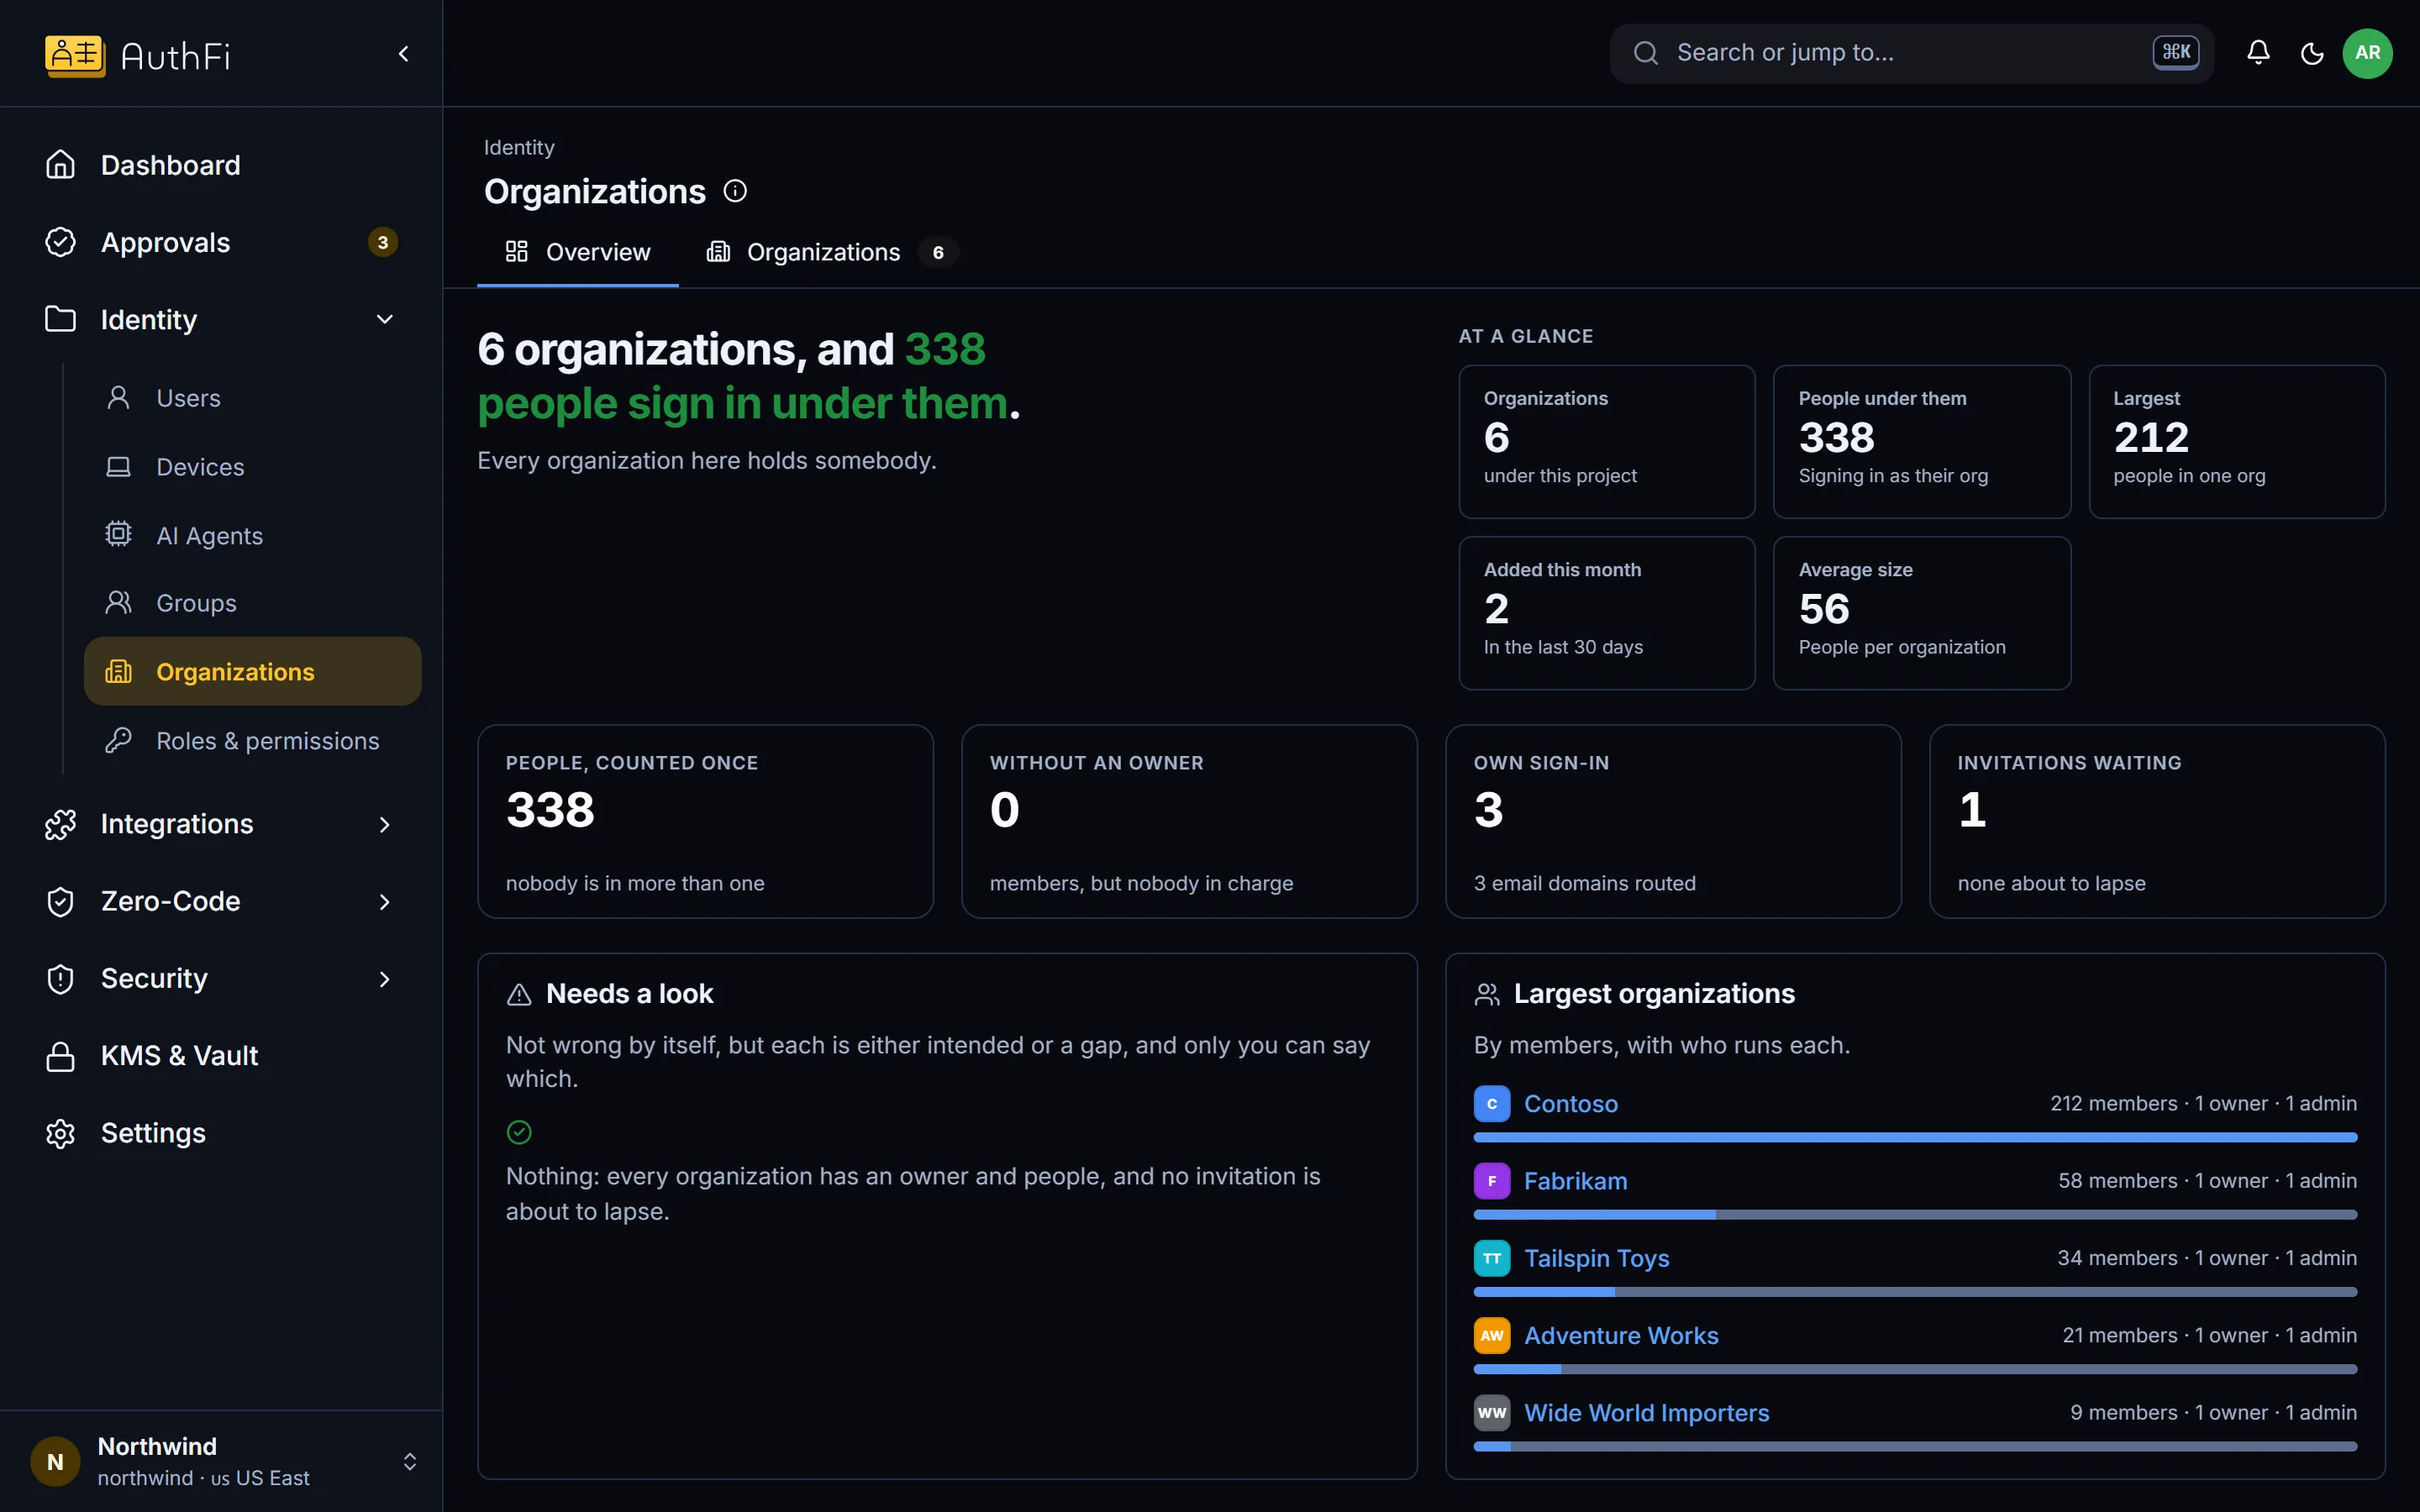
Your customers, as organizations.
Each business you sell to is an organization with its own members, so you can see and manage a customer as one thing.
Members per organization
Invitations
One place to see who belongs where
Read on
The parts of the product behind this.
Customer identity
Branded sign-in and organizations
OpenSign-in quickstart
Add sign-in to an app
OpenPricing
Included monthly users per plan
OpenMore in Identity and access
Zero-Code: sign-in for services, with no code
Zero-Code puts sign-in and access rules in front of services you already run.
See howWorkforce identity: a modern IdP
Single sign-on, provisioning, passkeys and devices, on open standards, with users included in the plan.
See howCloud and server access with no stored keys
Short-lived cloud roles and server sessions, granted by group.
See how