Solution · Security
Catch an agent or a workload behaving oddly.
A boundary stops what you did not grant. Detection tells you when something inside the boundary starts acting unlike itself.
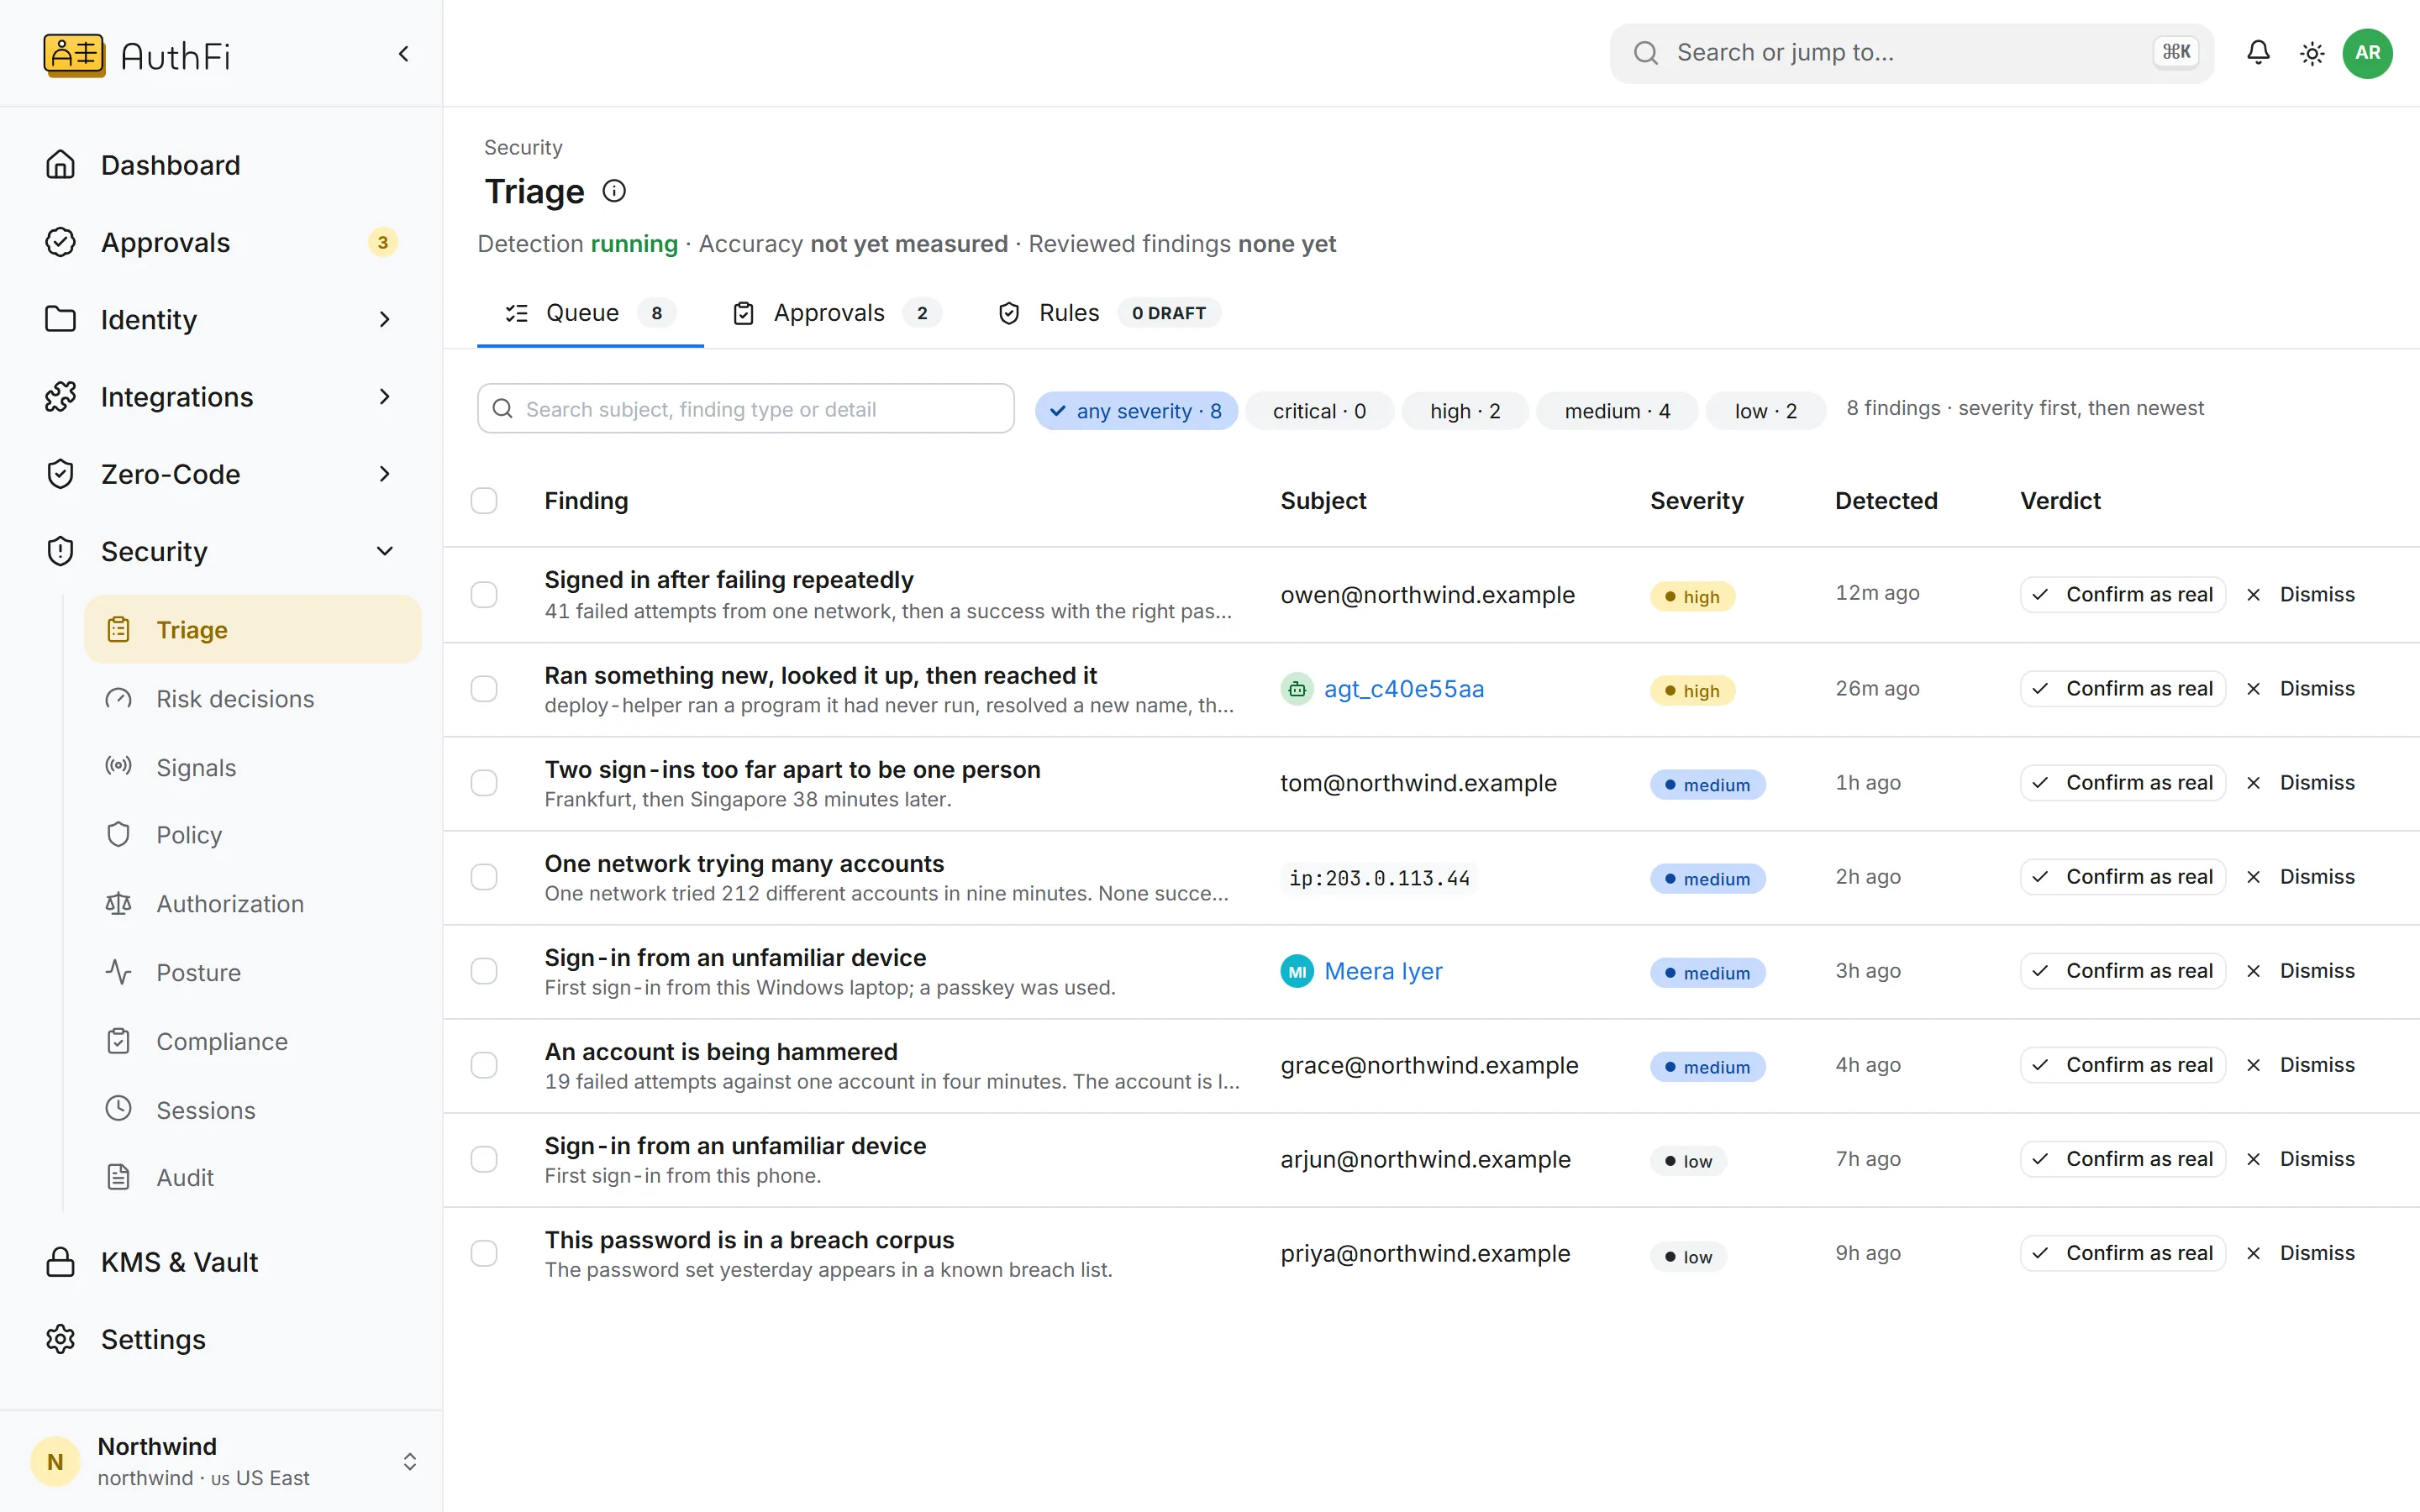
Findings to triage
Each finding says in plain words what was seen. You confirm it as real or dismiss it, and that verdict is what detection learns from.
What changes
The problem as most companies have it today, and the same thing with AuthFI.
How it works
Each step, on the screen you would use.
Findings
Findings a person can act on.
Each finding names the subject, what happened and how serious it is, and waits for a verdict.
A sign-in after a burst of failures
Two sign-ins too far apart
A workload that ran something new and reached it
Context
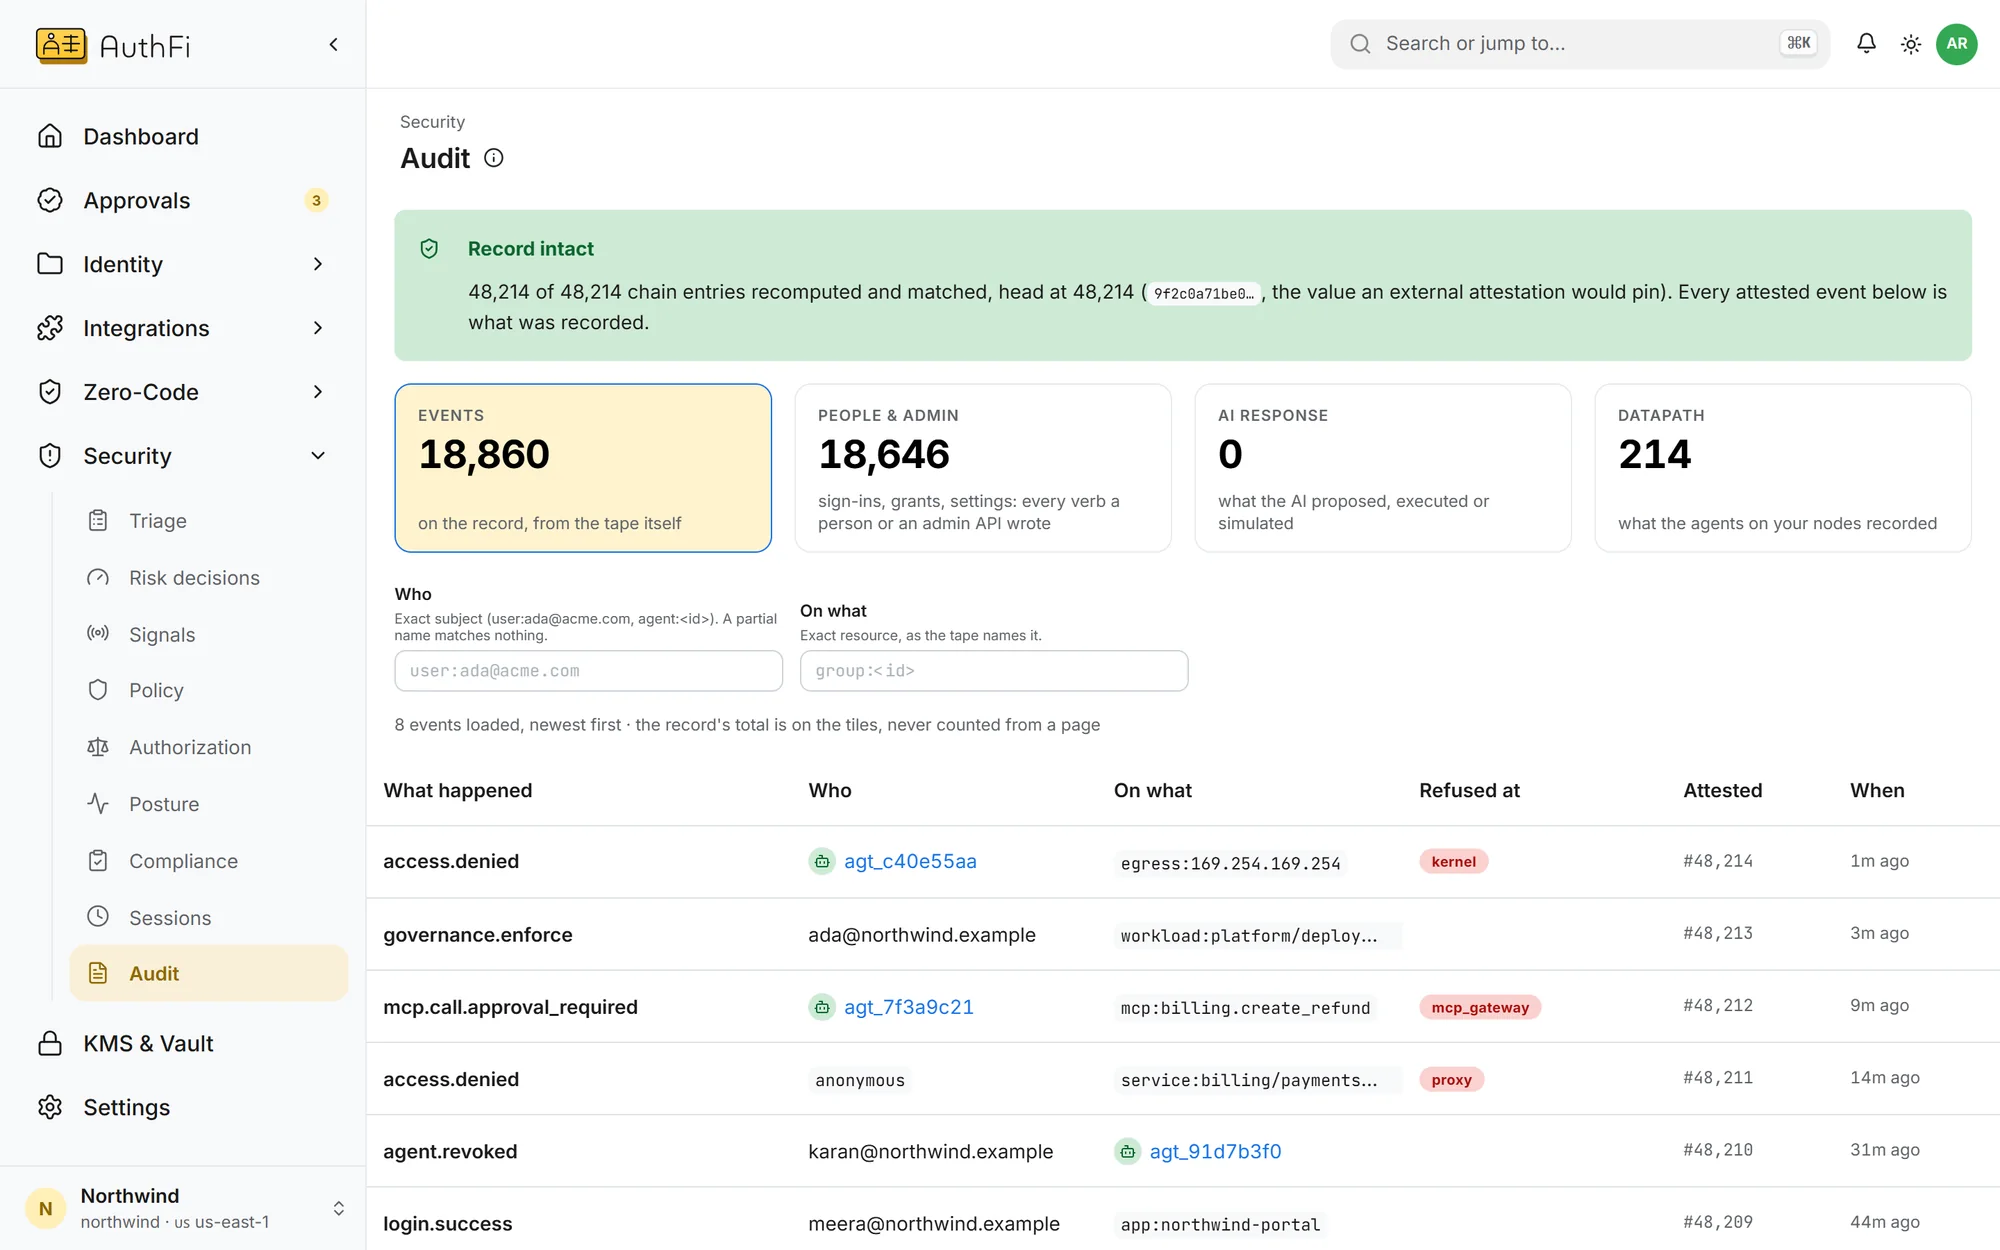
The record behind every finding.
Open the record for the same subject and see what it did before and after, and what was refused.
The same subject across sign-in, tools and the machine
Refusals beside successes
Export to your tools
Read on
Detection findings are in pilot. Findings from what runs on the machine need Zero-Code.
Security and audit
Findings, rules and the record
OpenAgent boundary
What is refused before detection is needed
OpenStop an agent
The off switch
OpenMore in Security
One record of who did what
Every sign-in, grant, approval and refusal, for people and agents, on one chained record.
See howKnow which of your rules actually refuse
Every rule on the platform, and whether it refuses, only watches, or cannot bite.
See howProtect every account from takeover
Passkeys, a second step on every plan, lockout, breached-password checks and sessions you can end.
See how