Solution · Identity and access
SAML single sign-on for every app, from one account.
Connect the applications your staff use over SAML 2.0. Each person signs in once, and their groups decide which apps they can open.
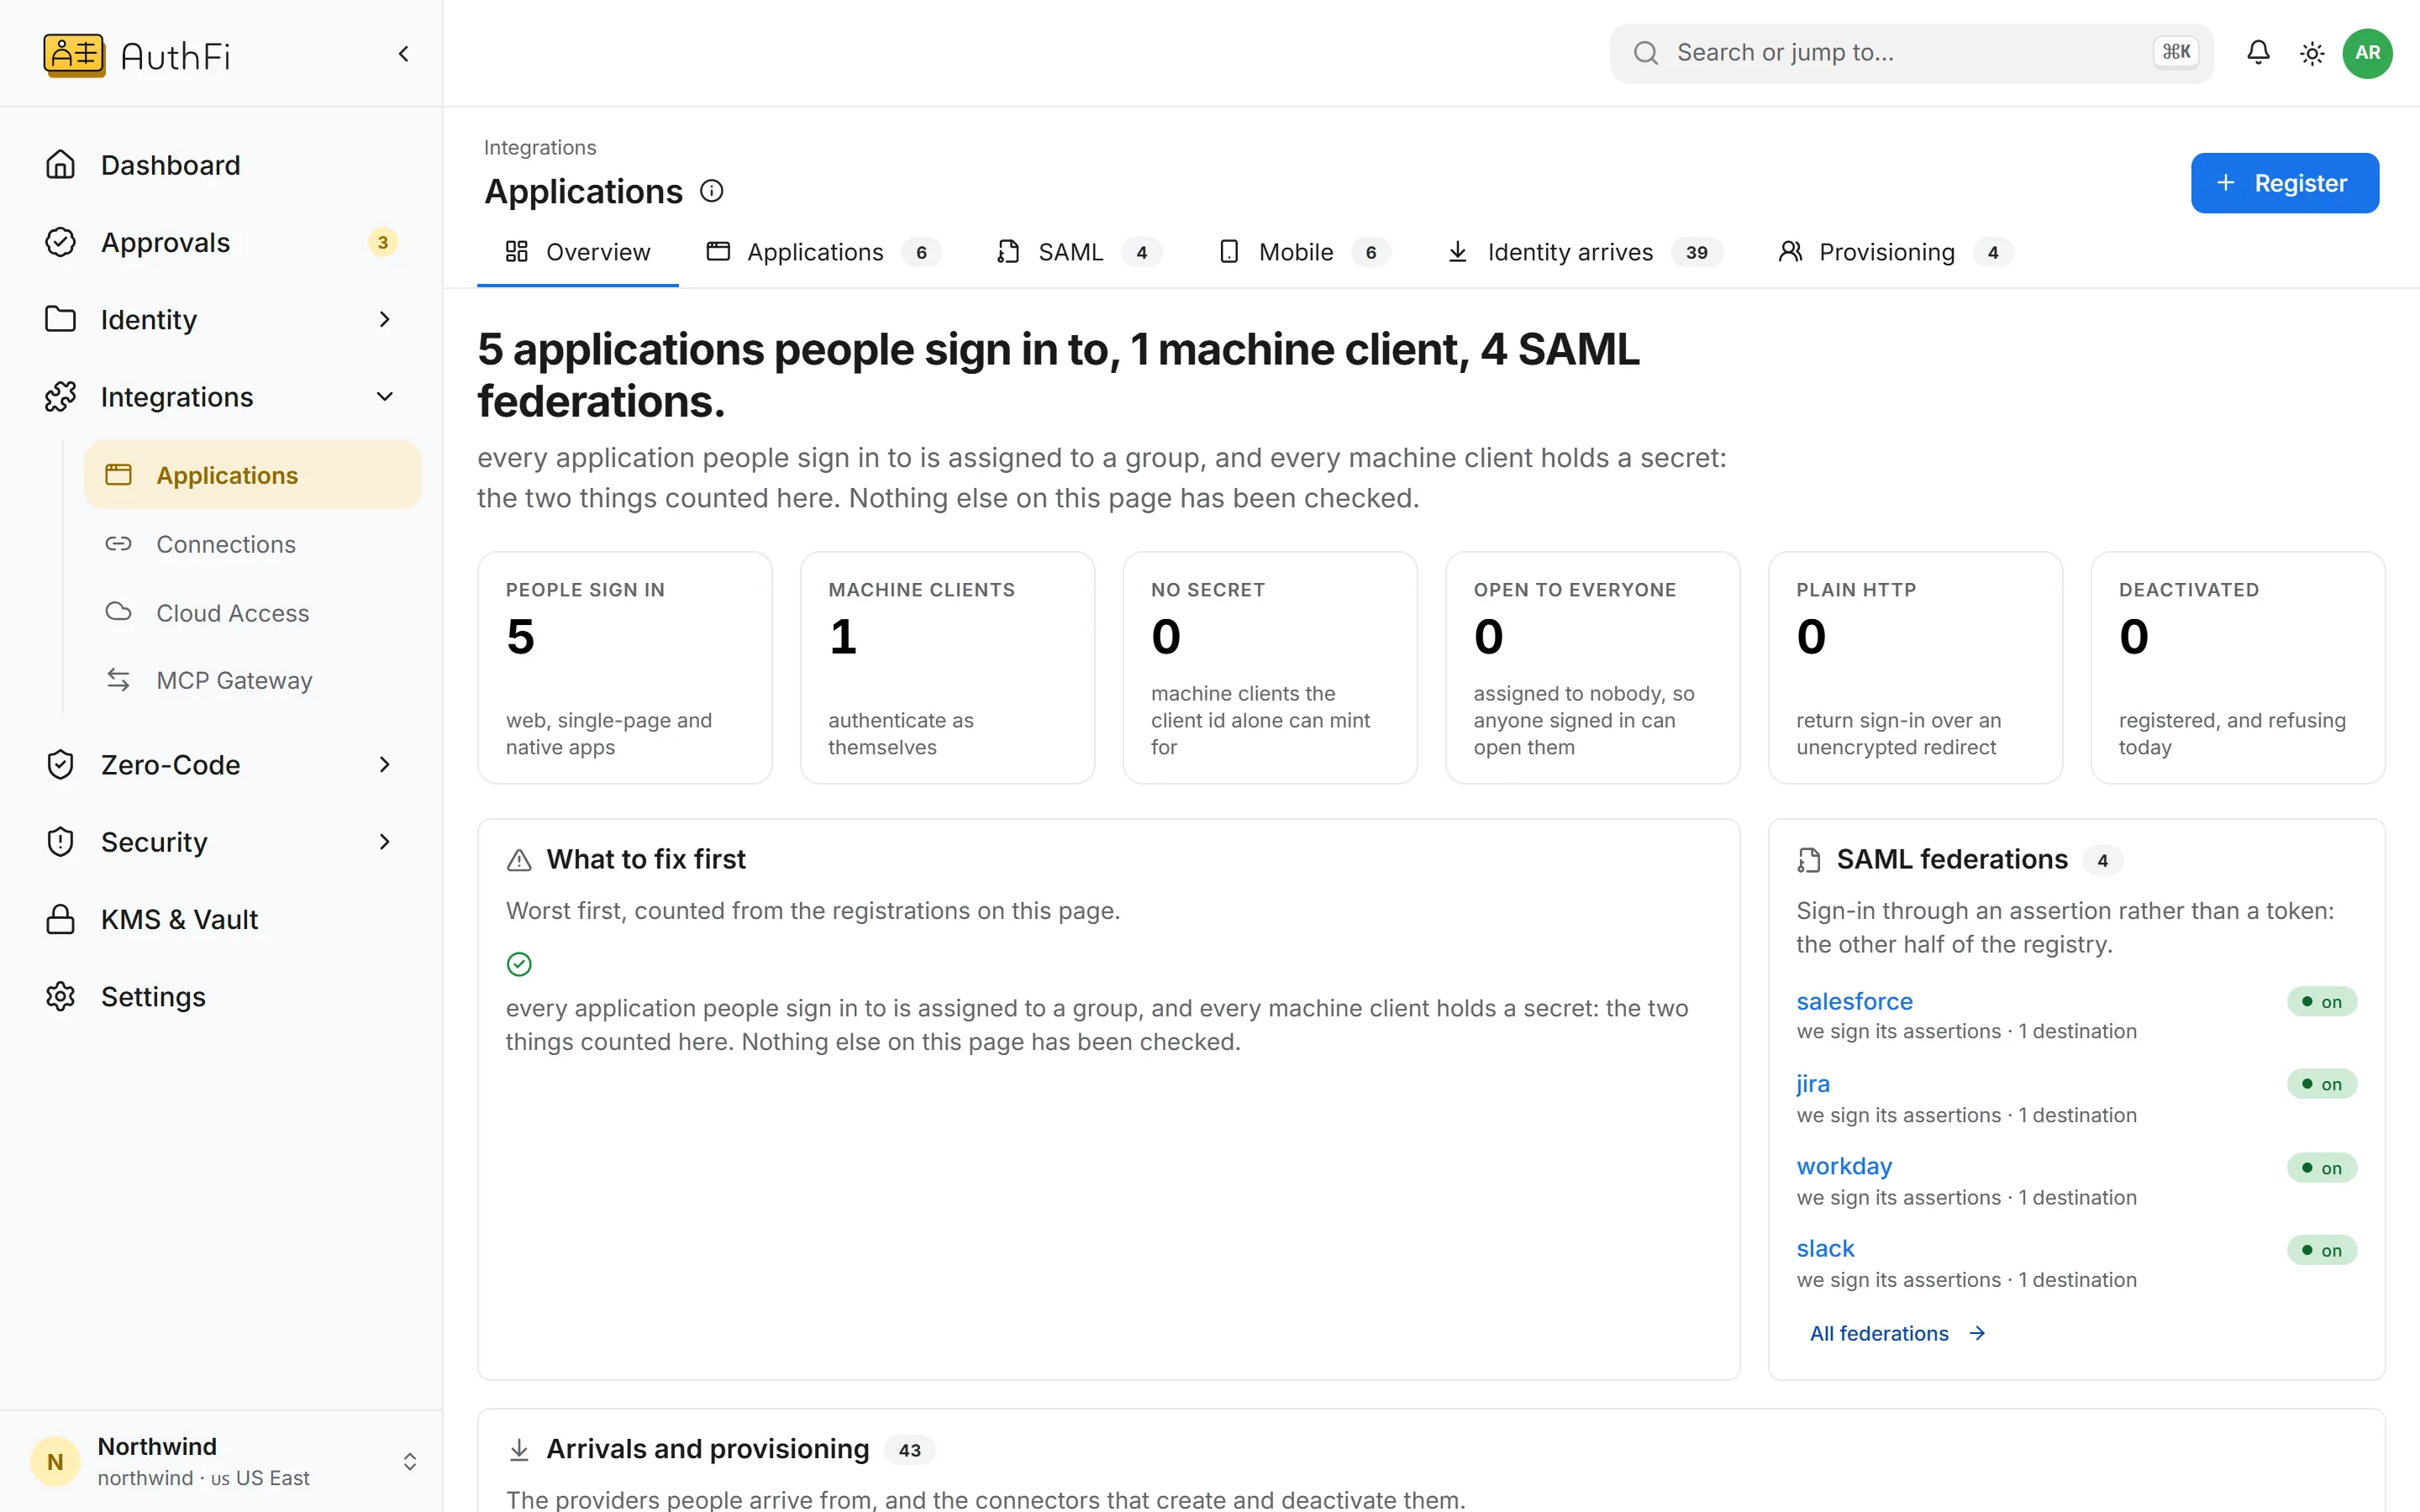
Every application people sign in to
Web, mobile and machine clients, and the software that signs in over SAML. The page leads with what to fix first.
What changes
The problem as most companies have it today, and the same thing with AuthFI.
How it works
Each step, on the screen you would use.
Applications
Add an app, hand over its settings.
Register the application, then copy the sign-on address, entity id and certificate into it. That is the whole exchange.
SAML 2.0, and OpenID Connect for apps that prefer it
Metadata and certificate ready to copy
Assigned to groups
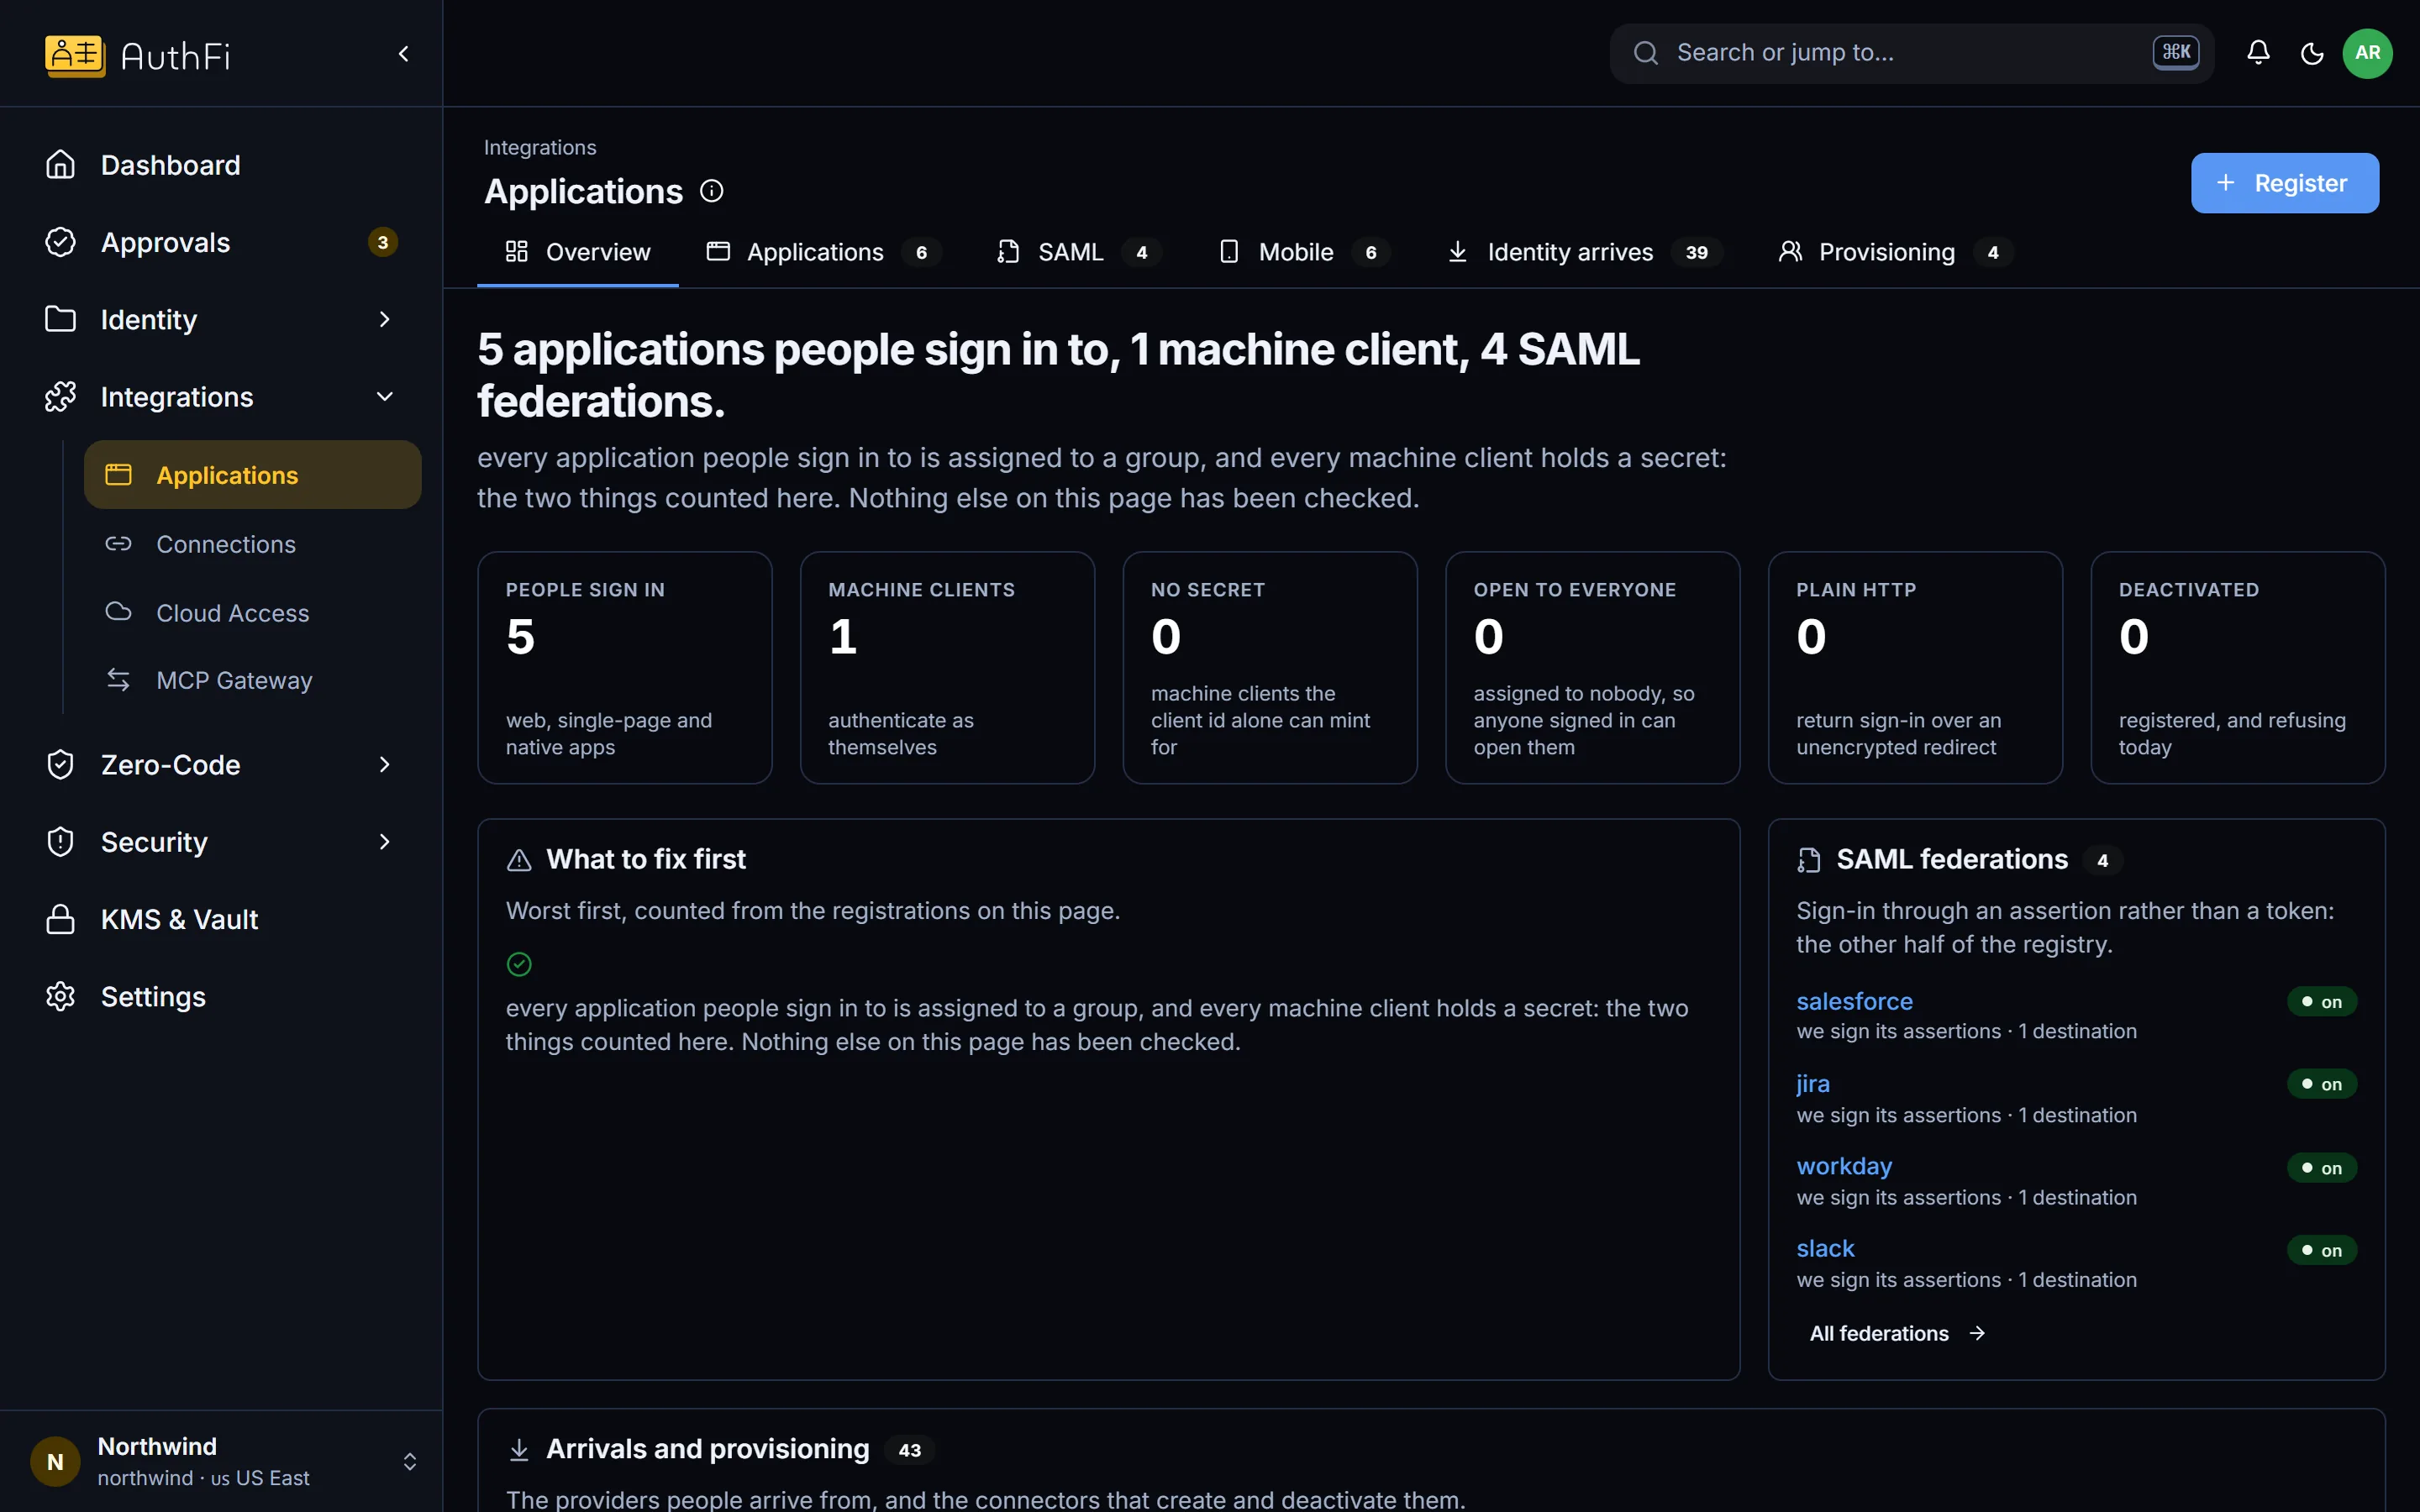
People
Bring your existing directory.
People can keep signing in with the identity provider you already have, and AuthFI carries them on to every app.
Sign people in from Okta, Entra, Google and others
Passkeys and a second step on top
One record of every sign-in
Read on
Encrypted SAML assertions and full single logout are not supported yet.
Workforce identity
Every protocol AuthFI speaks
OpenSCIM provisioning
Accounts that follow your directory
OpenA modern IdP
The whole workforce story
OpenMore in Identity and access
Zero-Code: sign-in for services, with no code
Zero-Code puts sign-in and access rules in front of services you already run.
See howWorkforce identity: a modern IdP
Single sign-on, provisioning, passkeys and devices, on open standards, with users included in the plan.
See howCloud and server access with no stored keys
Short-lived cloud roles and server sessions, granted by group.
See how