Solution · by industry
Identity for financial services, with every action on the record.
For banks, fintechs and insurers that must show who did what, keep data in the country, and stay in control of the AI agents they are starting to use.
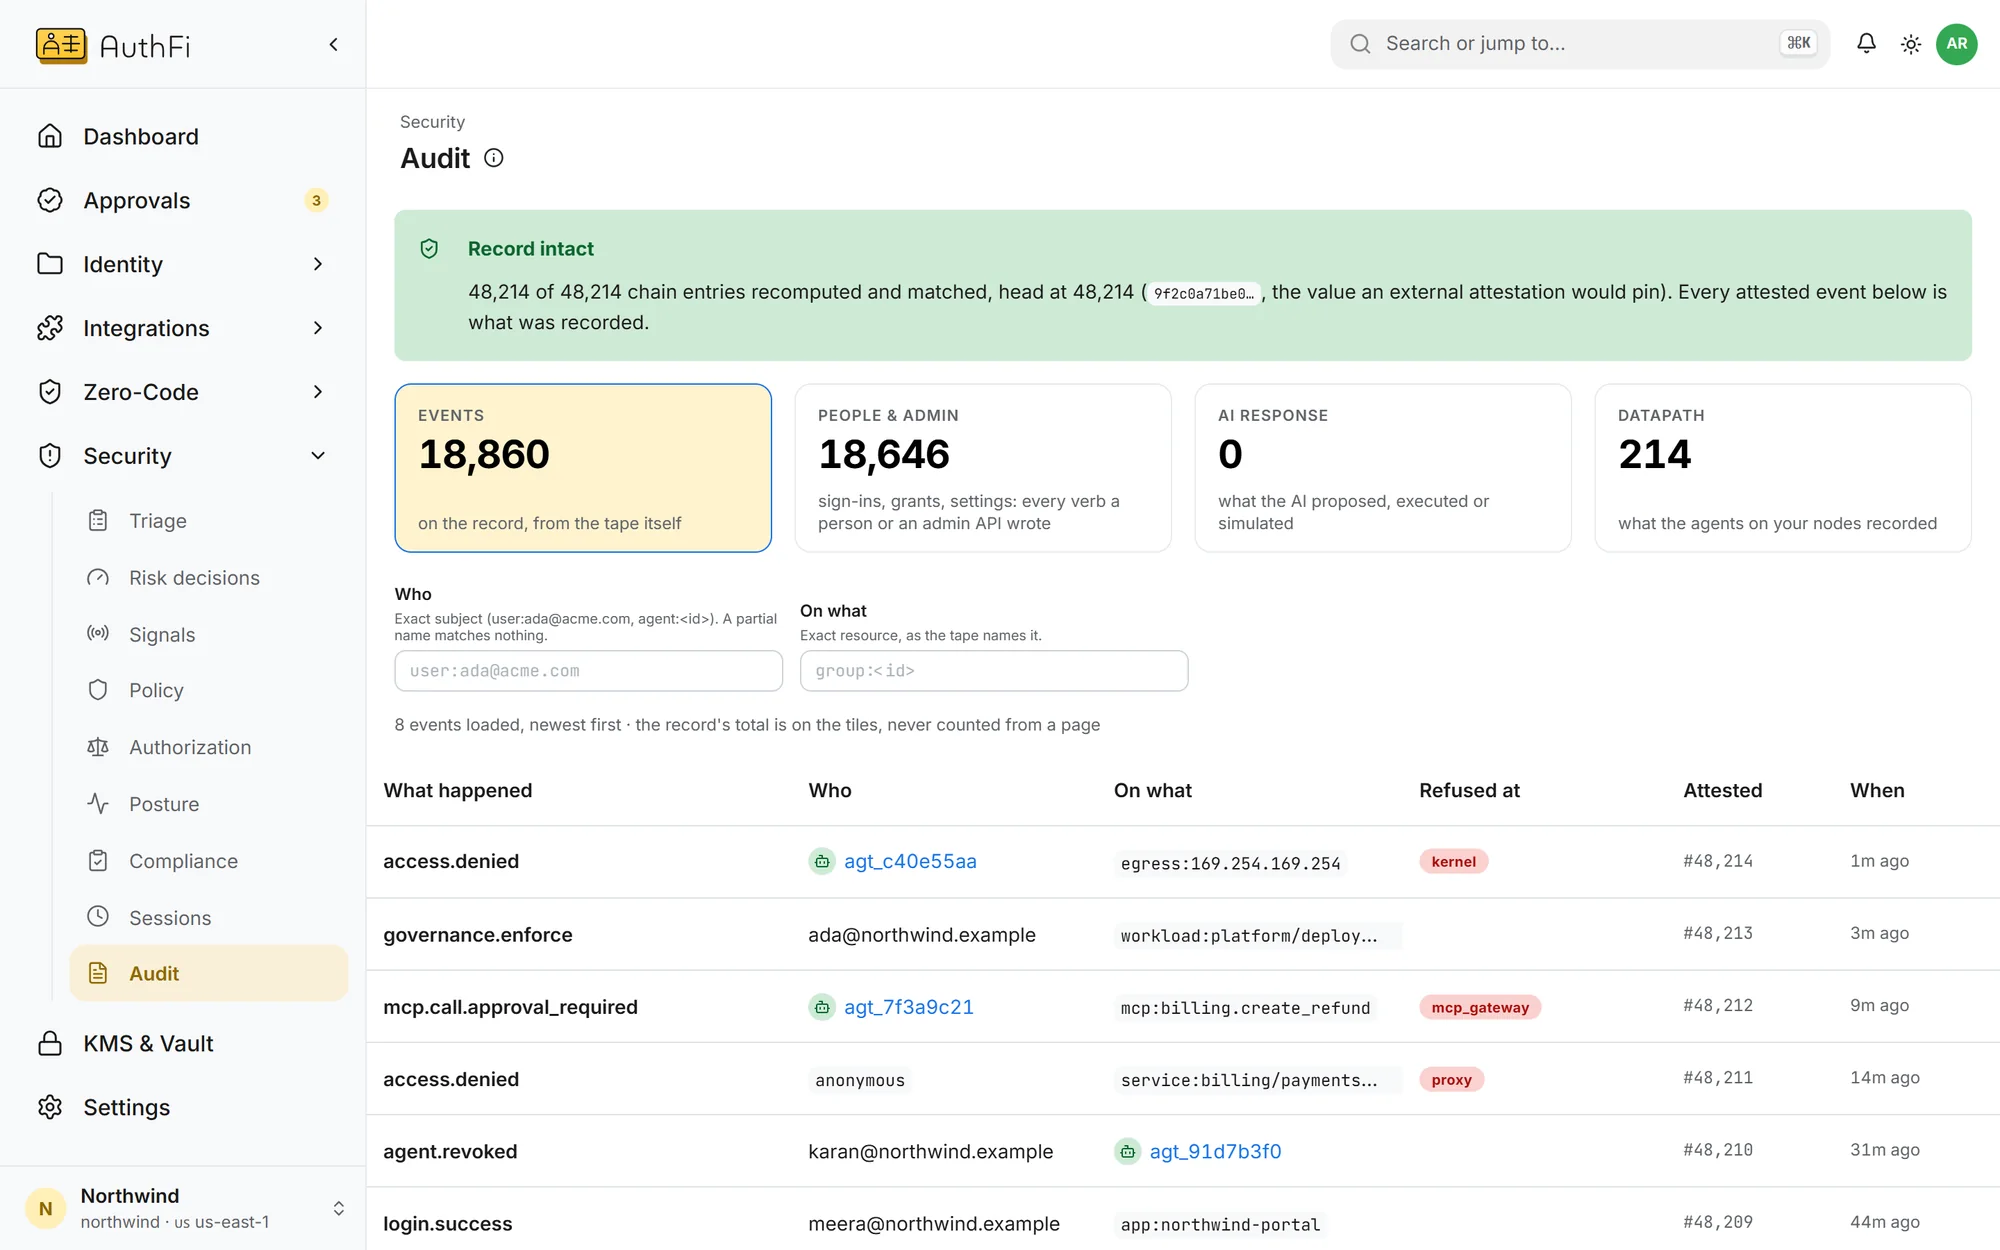
The record
What happened, who did it and at which layer it was refused. The banner says whether the record itself is intact.
What changes
Where organisations like yours usually start, and where AuthFI takes them.
How it works
Each step, on the screen you would use.
Approval
A second person on the actions that move money.
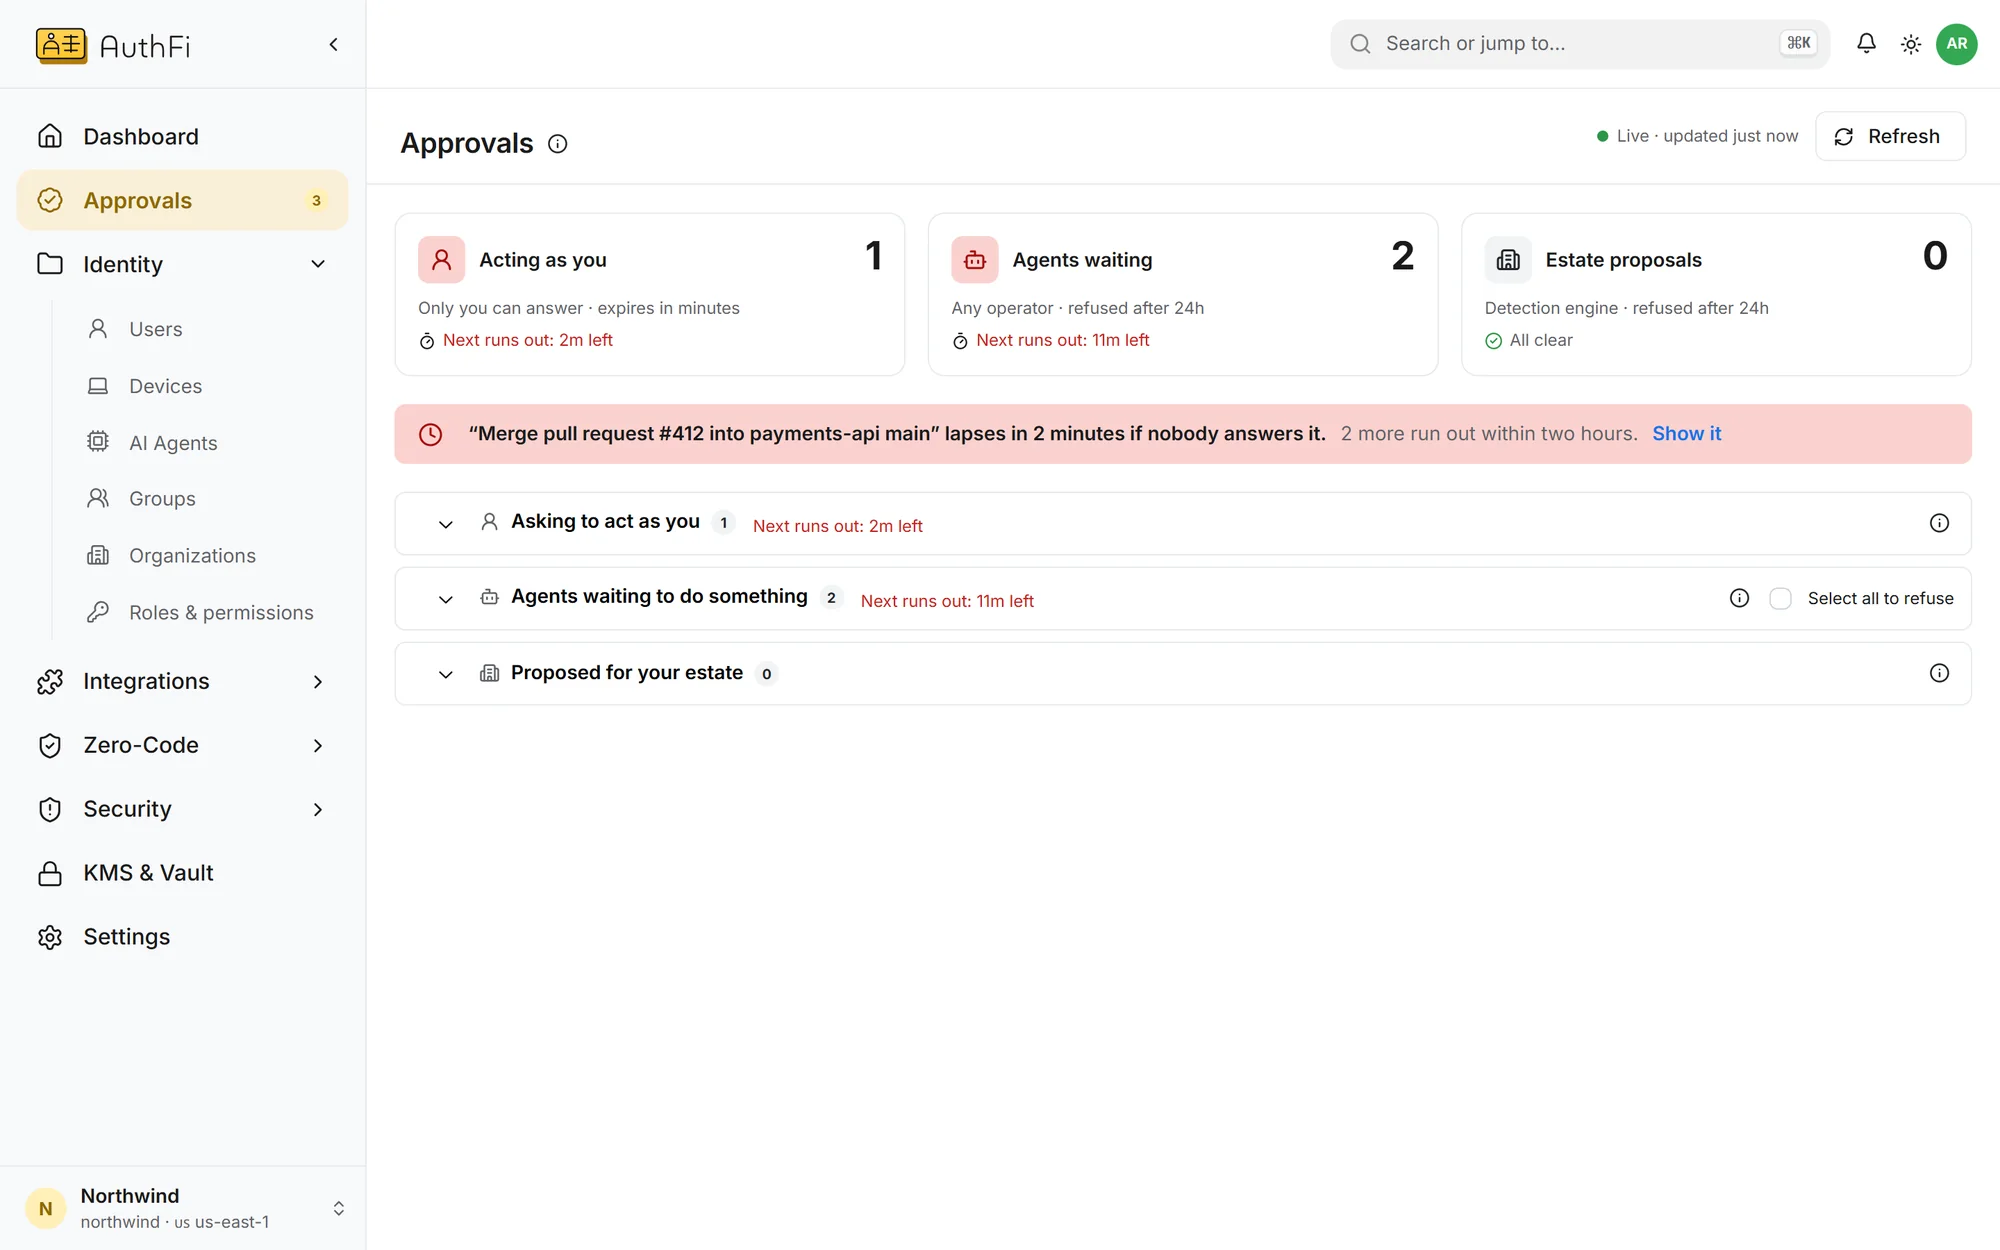
When an AI agent wants to do something you marked as sensitive, it stops and a named person decides.
Limits on amounts, checked on every call
A request nobody answers is refused
Who approved, and when, is recorded
Record
A record that shows tampering.
Every sign-in, grant and refusal lands on one record. Entries are chained, so an edit or a gap is visible.
People and agents on the same record
Each refusal with the layer that refused it
Export to the log tools you use
Our region
Virginia, USA
AWS, US East
us-east-1Our region
Mumbai, India
Google Cloud, Mumbai
asia-south1Your own cloud
Any cloud
AWS, Google Cloud, Azure, Oracle, or your own data centre. Run by you, or by us inside your boundary.
EnterpriseWhat you are asked for
The questions a regulator, an auditor or a customer's security team puts to you, and what in AuthFI answers each.
Strong authentication for staff and customers
Passkeys and a second step, and an application can require the stronger sign-in
Workforce identityA second person on sensitive actions
An AI agent's sensitive action waits for a named person's approval
AI AuthAn audit trail that cannot be quietly edited
A chained record, with every refusal and who decided each approval
Security and auditLeast privilege, and access removed on time
Access by group, server certificates that last five minutes, cloud roles with no stored keys
Keyless accessControl of signing keys
Signing keys per project, with rotation that signs nobody out
Keys and secretsRead on
This page describes controls the product has. It is not a statement of certification. Ask us for our current security documentation.
Govern AI agents
Owners, limits, approvals and an off switch
OpenSecurity and audit
The record, the rules and the findings
OpenTalk to us
Ask for our security documentation
OpenOther industries
Healthcare
For hospitals, labs and health software: a named account behind every access.
See howSoftware and AI companies
Enterprise-ready sign-in for your product, and control of the agents inside it.
See howPublic sector and regulated India
Identity that runs in India, or inside your own data centre.
See how