Solution · AI enforcement
Put AI agents into production, under control.
AI Auth gives every agent an identity through the AuthFI Agent Profile, a profile of published standards. Know which agents you run, what each can reach, who answers for it, and how to stop it.
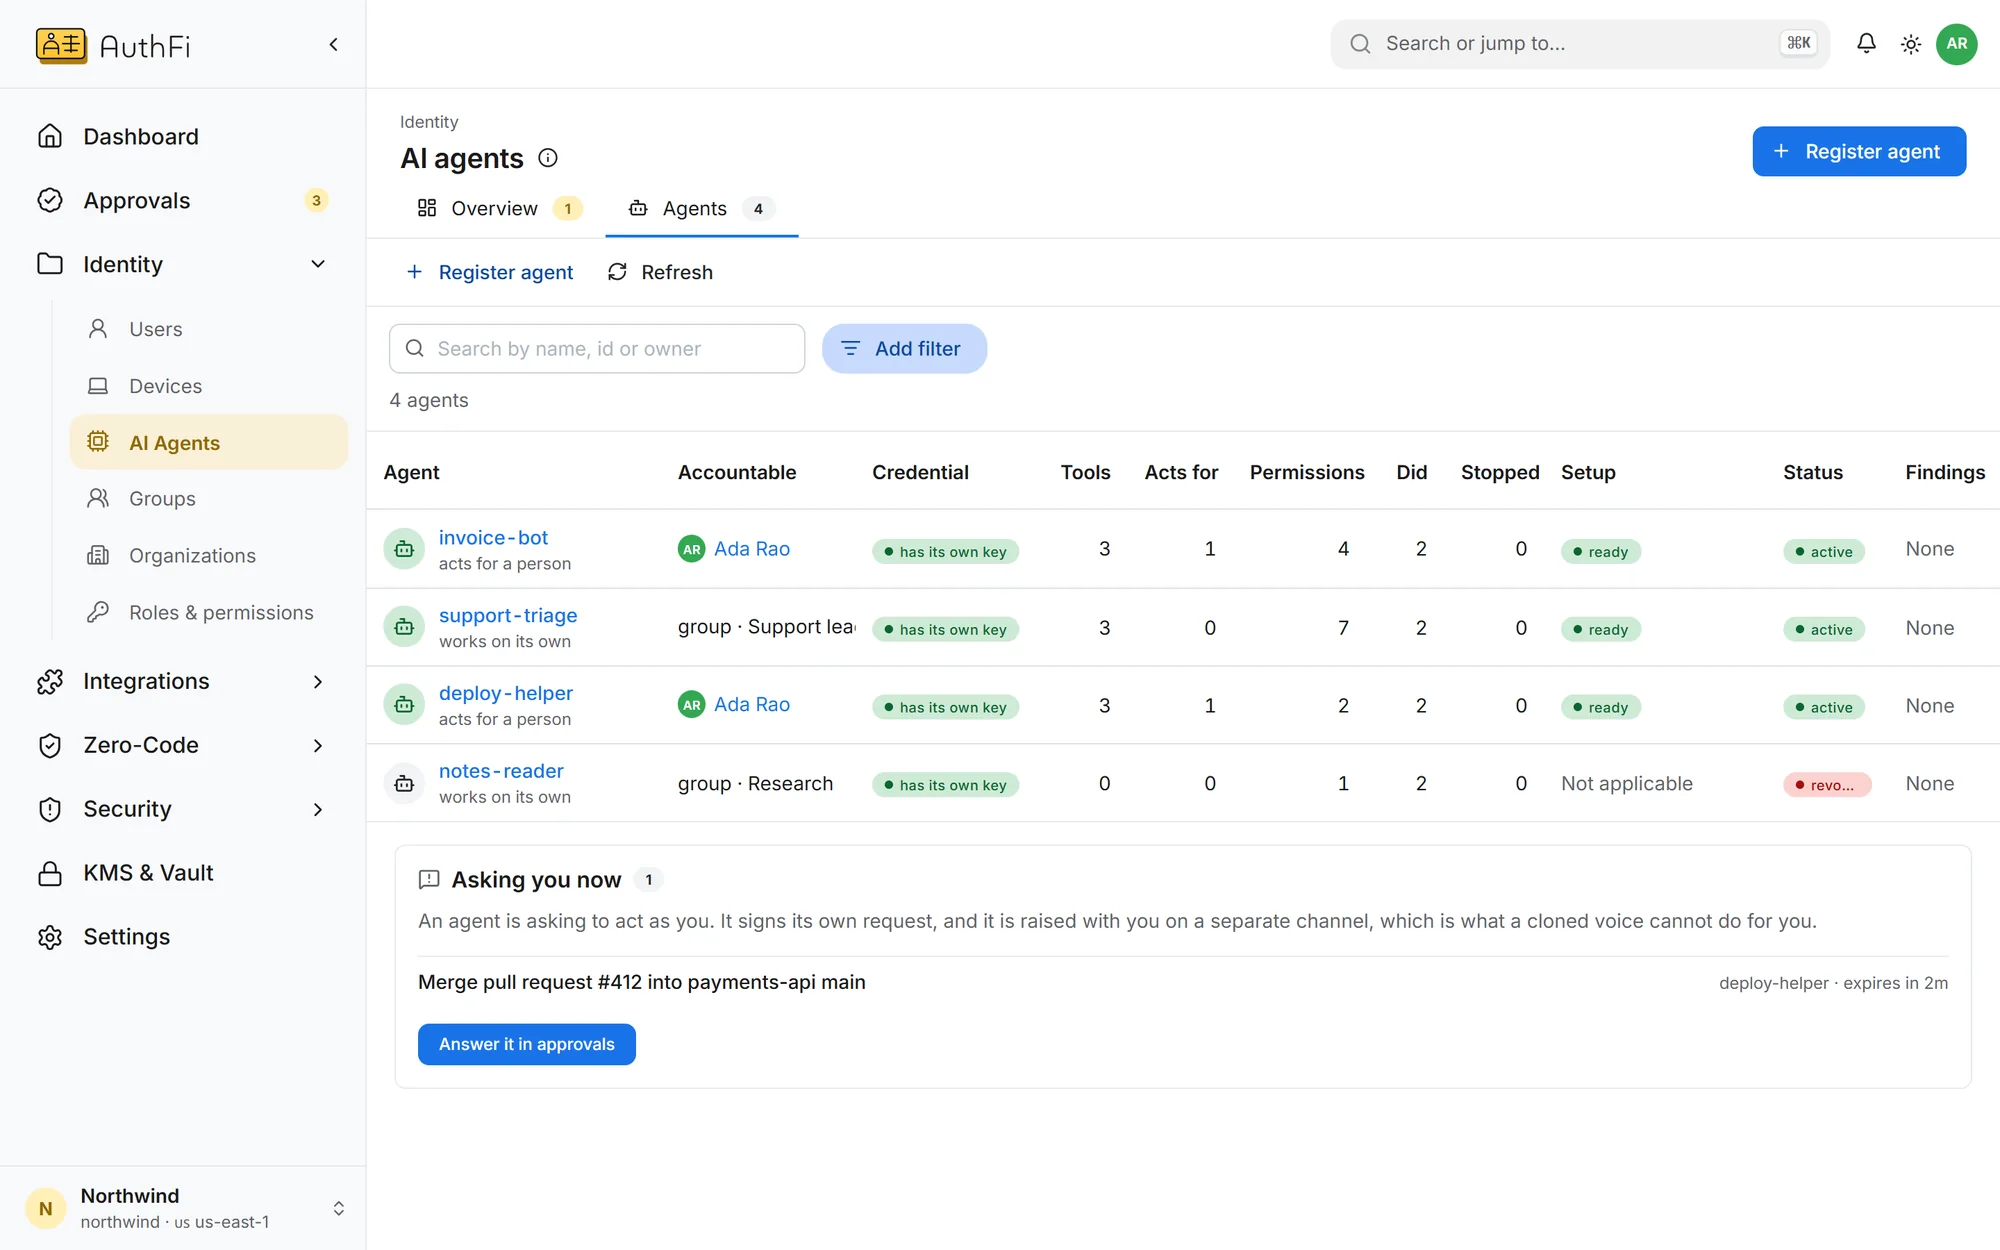
Every agent, with someone accountable
Each agent is listed with its owner, the key it holds, how many tools it has, and what it has been stopped from doing.
What changes
The problem as most companies have it today, and the same thing with AuthFI.
How it works
Each step, on the screen you would use.
Identity
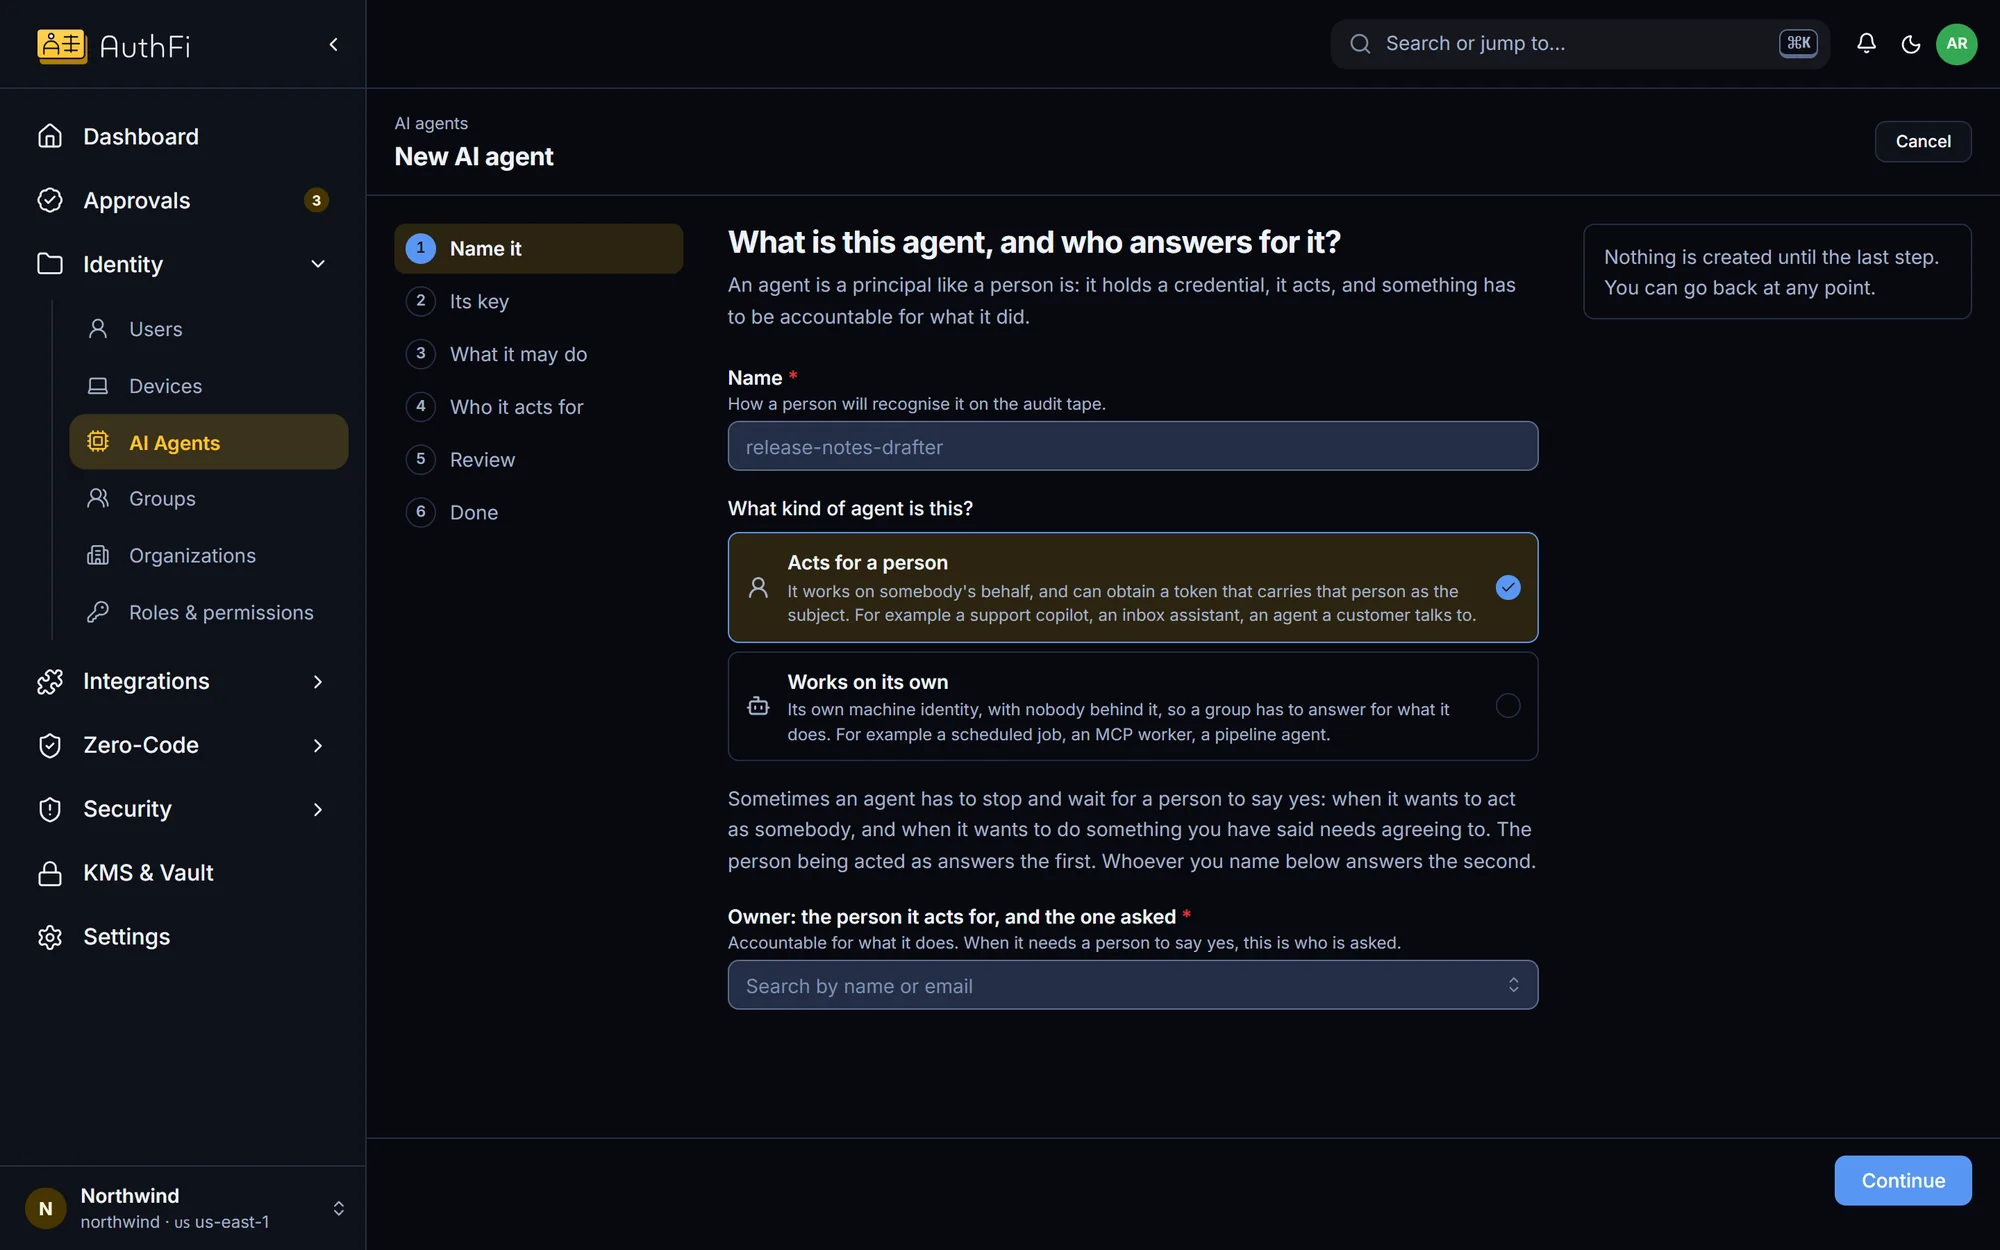
Every agent, with someone accountable.
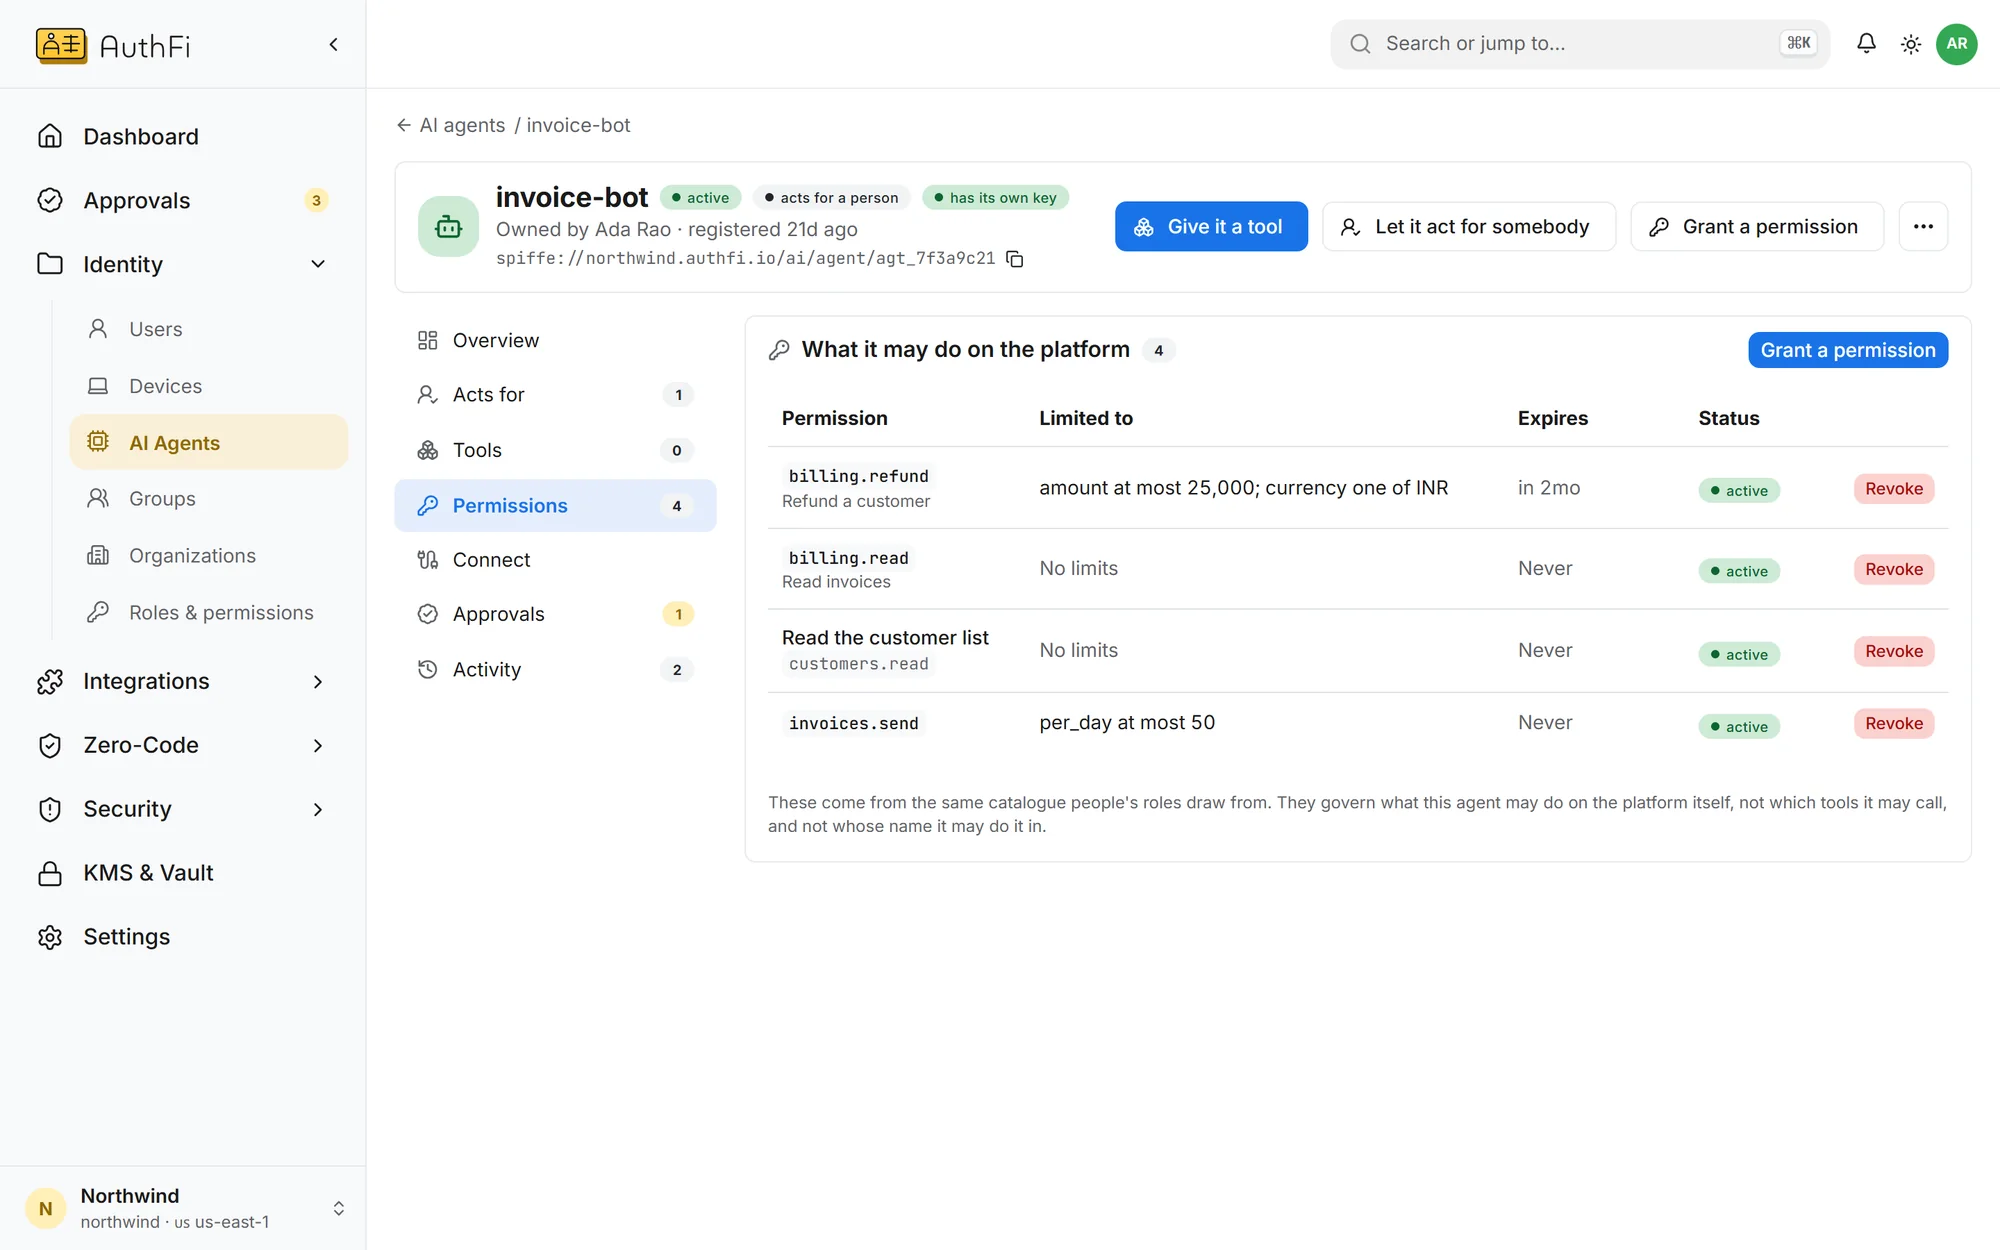
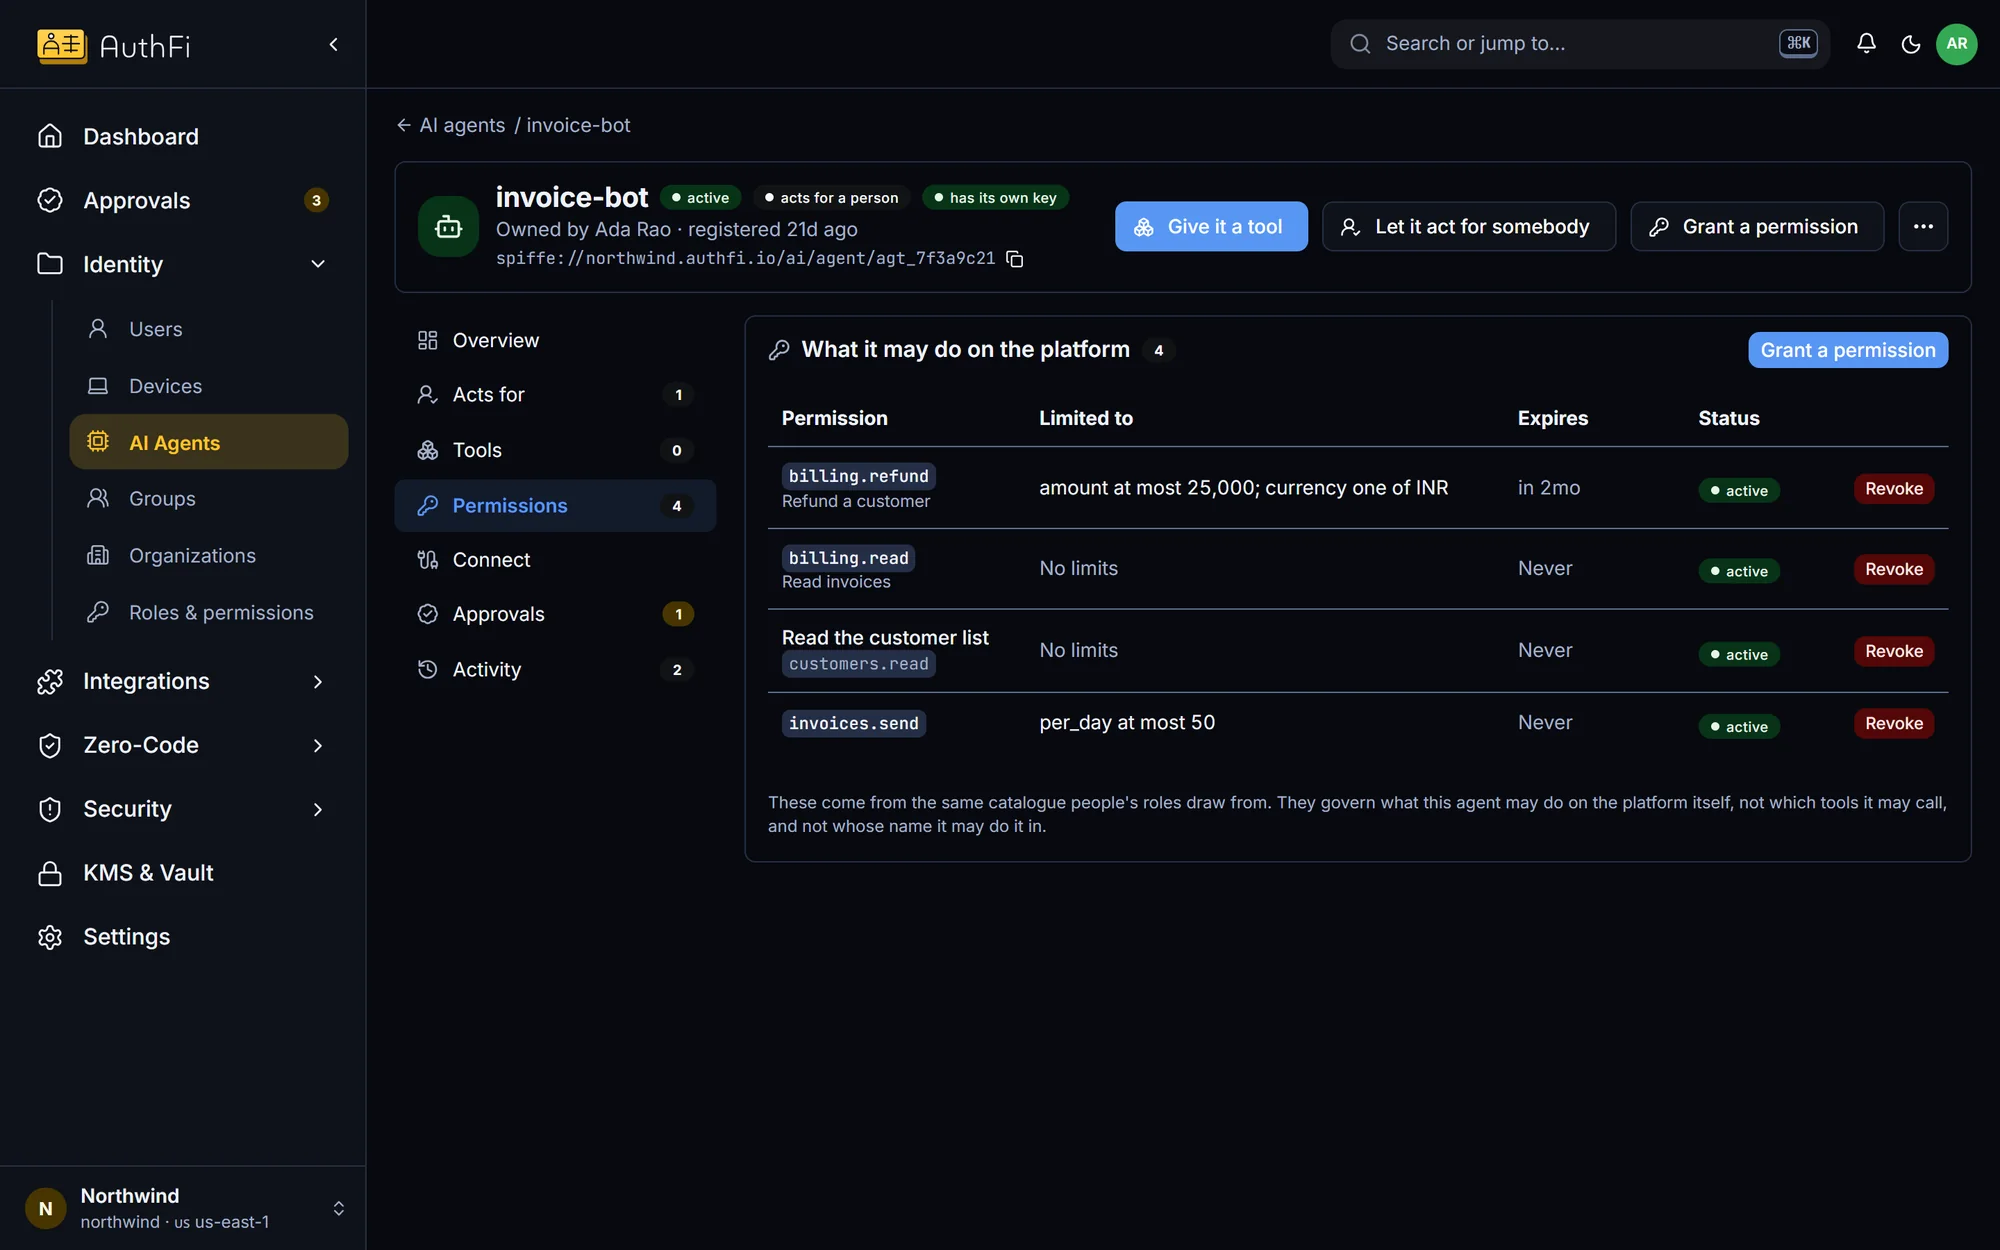
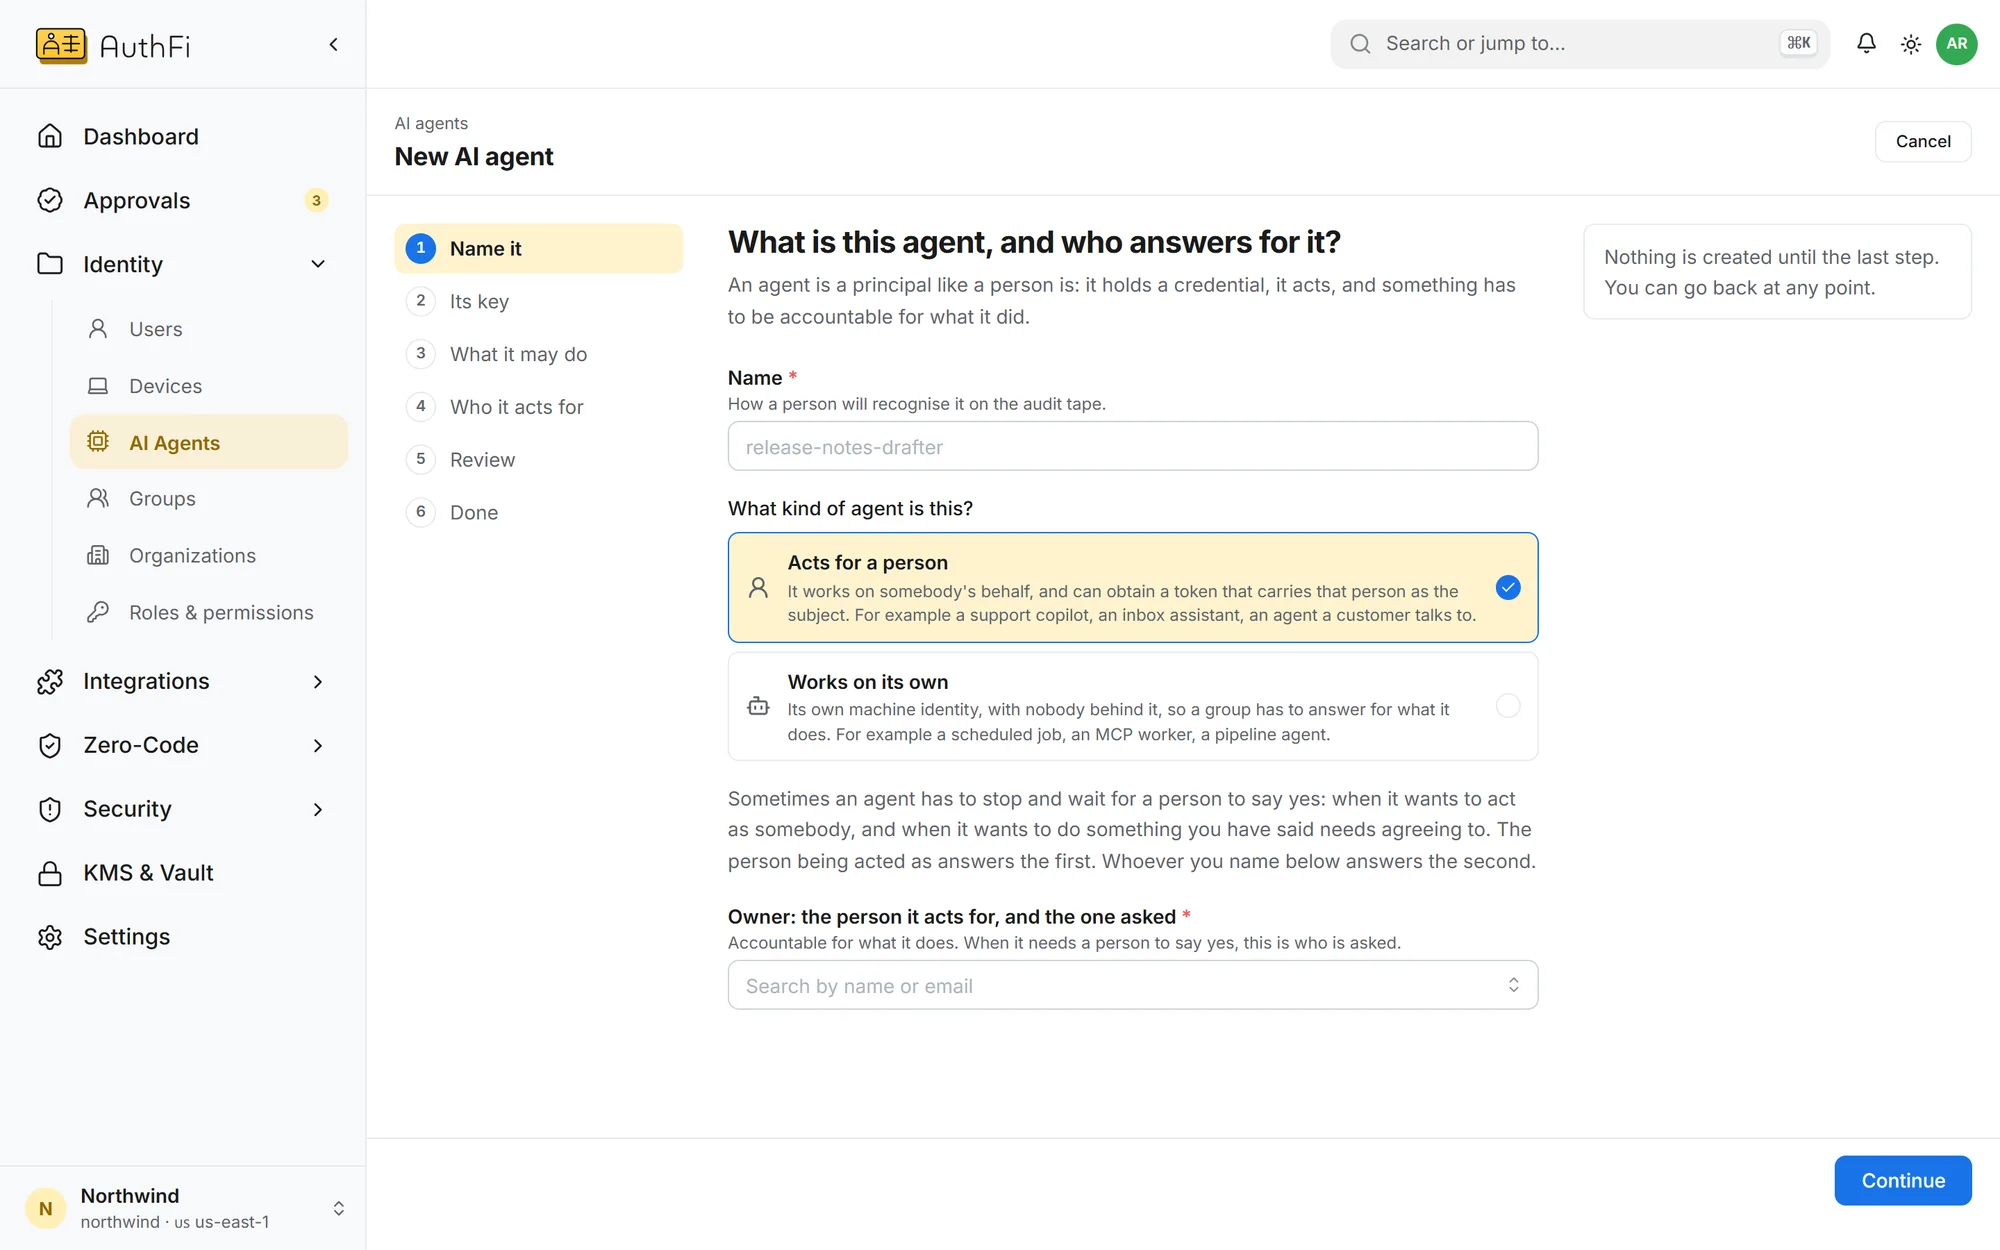
An agent is registered with its own key and the person or group that answers for it. Nothing is shared, so nothing can be copied.
Its own key, never a shared secret
Tokens that last 15 minutes
Acts for a person, or works on its own
AuthFI Agent Profile
Built on standards, so any client can speak it.
The AuthFI Agent Profile fixes which published standards an agent uses, with an AuthFI extension only where none exists. An agent signs in with its own key, gets a short token, and binds a token to one action before it acts.
Sign-in with a signed assertion (RFC 7523)
One-action tokens that last 60 seconds
Approval by a person, out of band (OpenID CIBA)
Tools
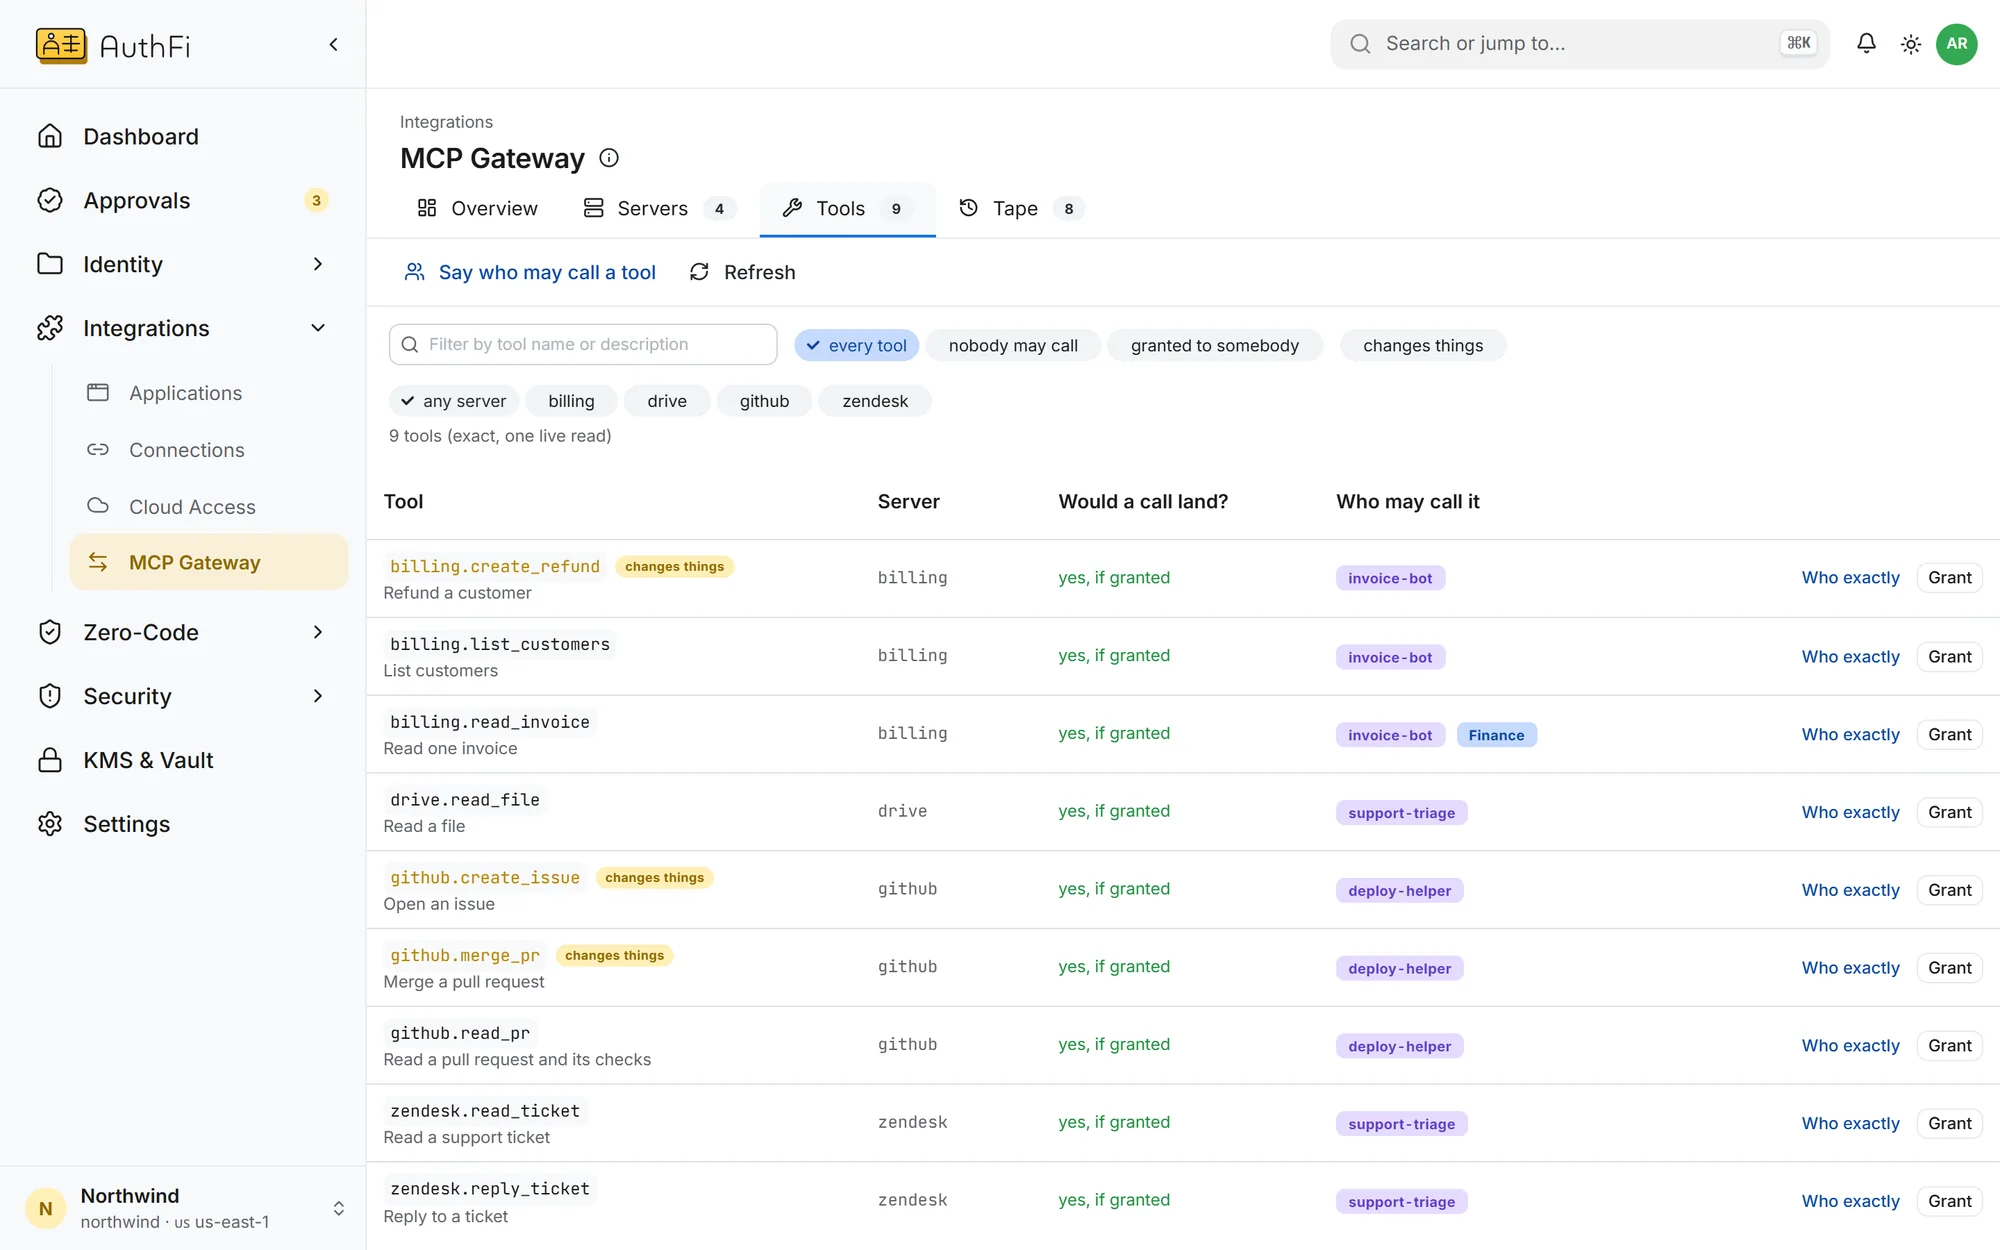
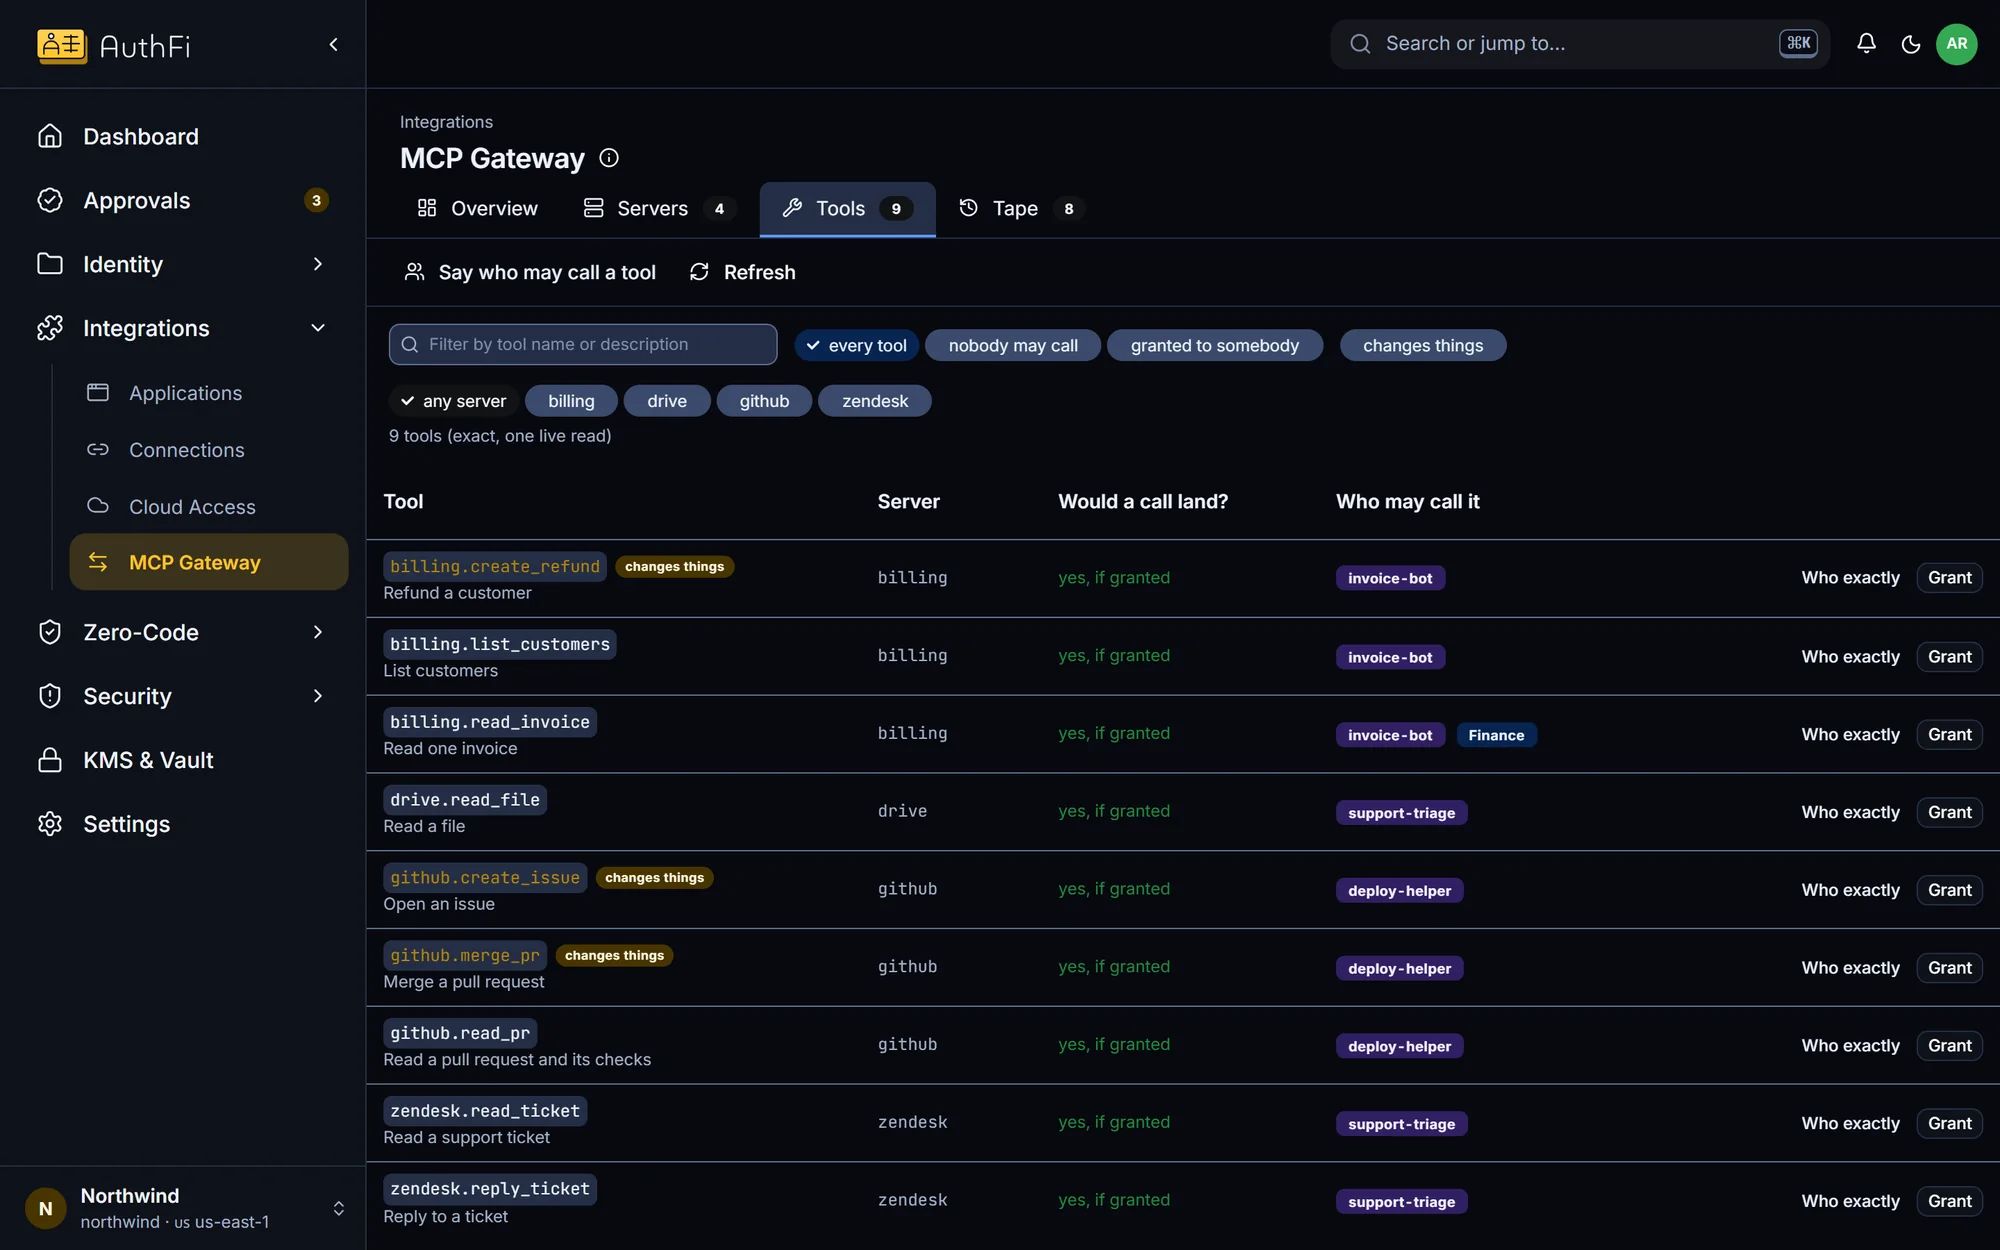
Tools granted one by one.
Agents reach tools through the gateway. A tool that was not granted is refused, and the tool's own credential never reaches the agent.
Per-tool grants
Arguments checked against the limit
Every call recorded with its verdict
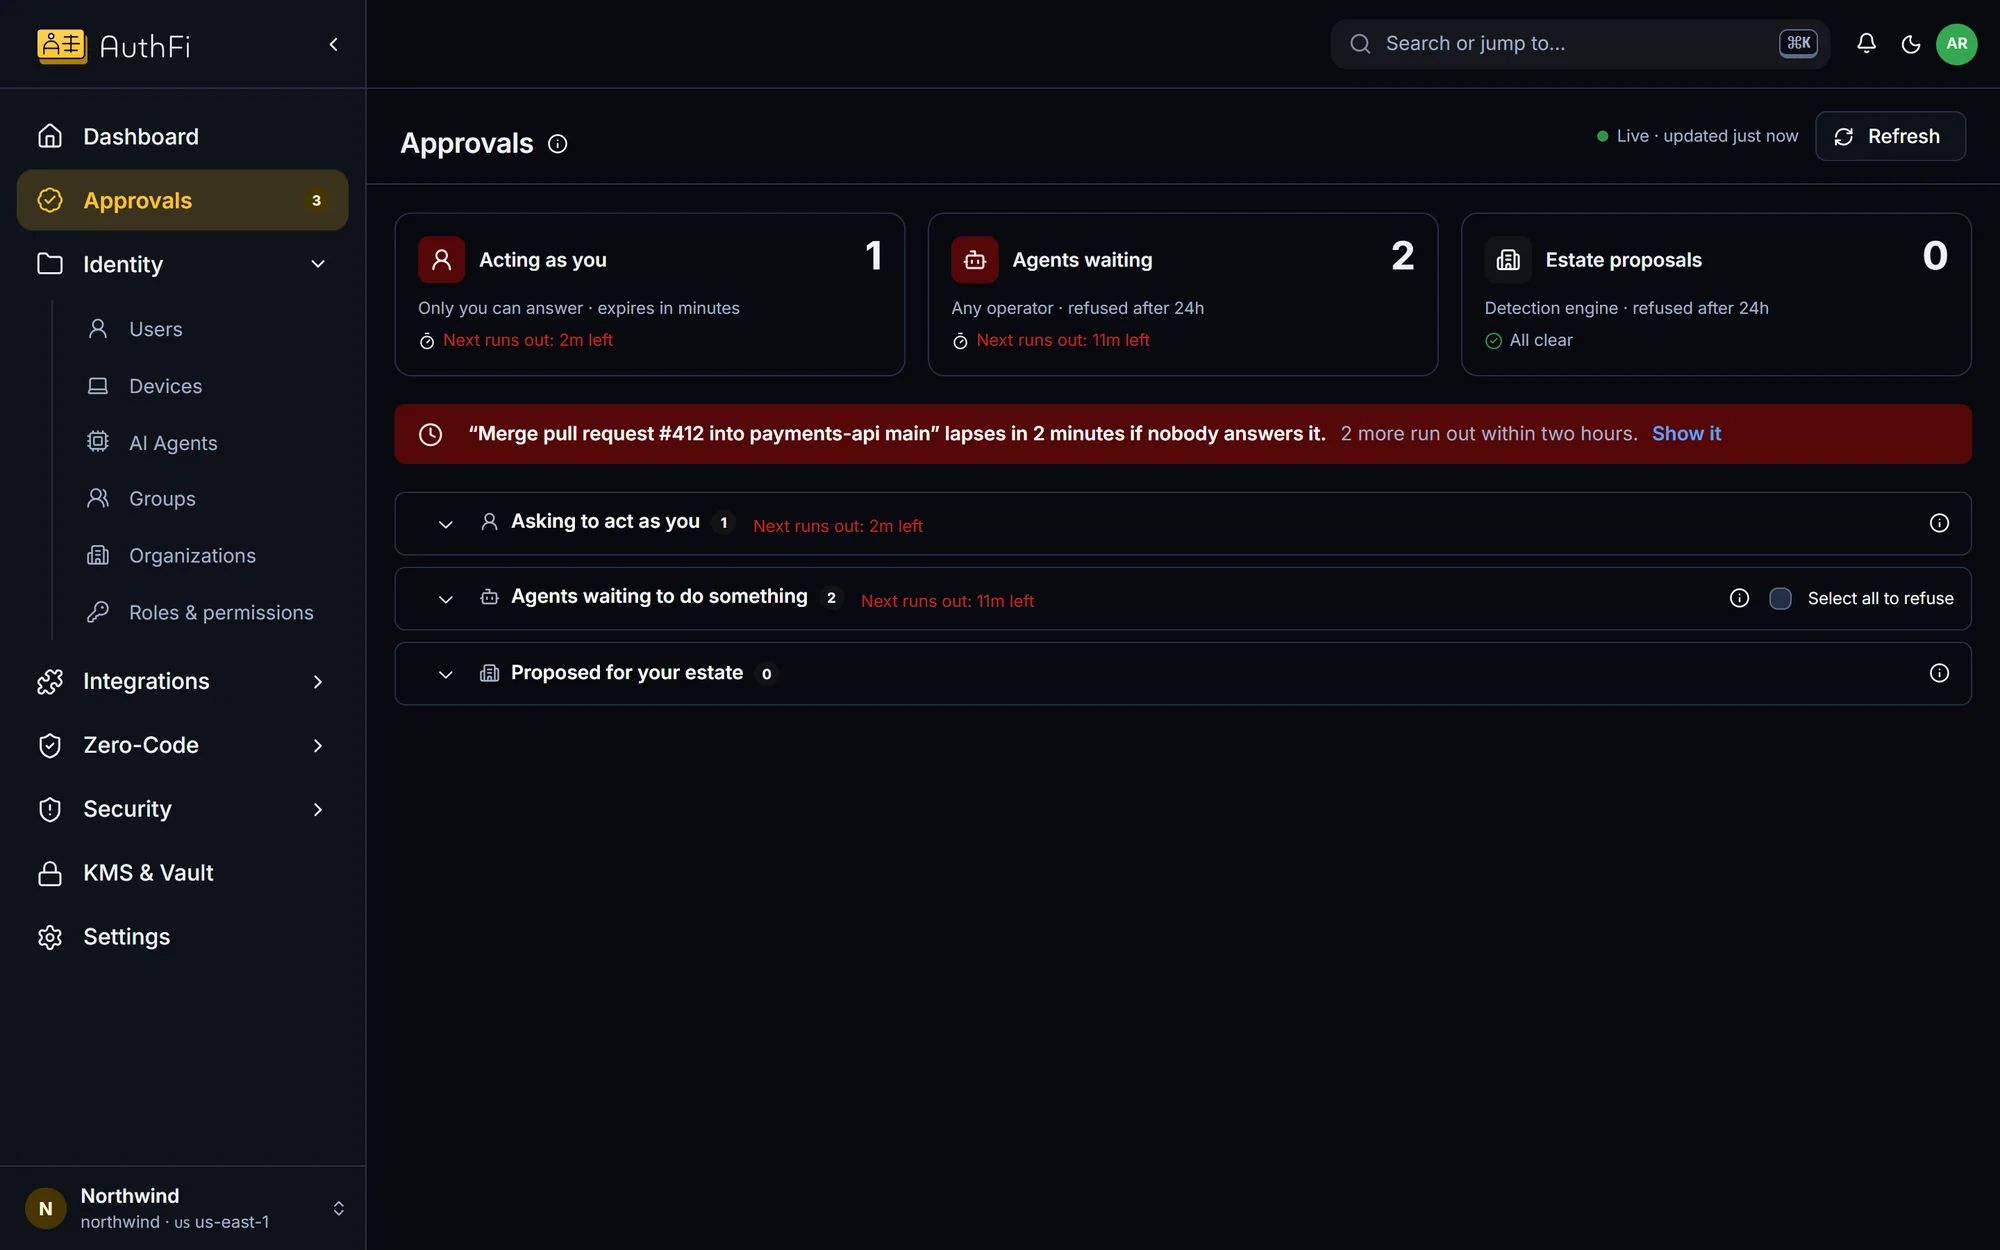
Approval
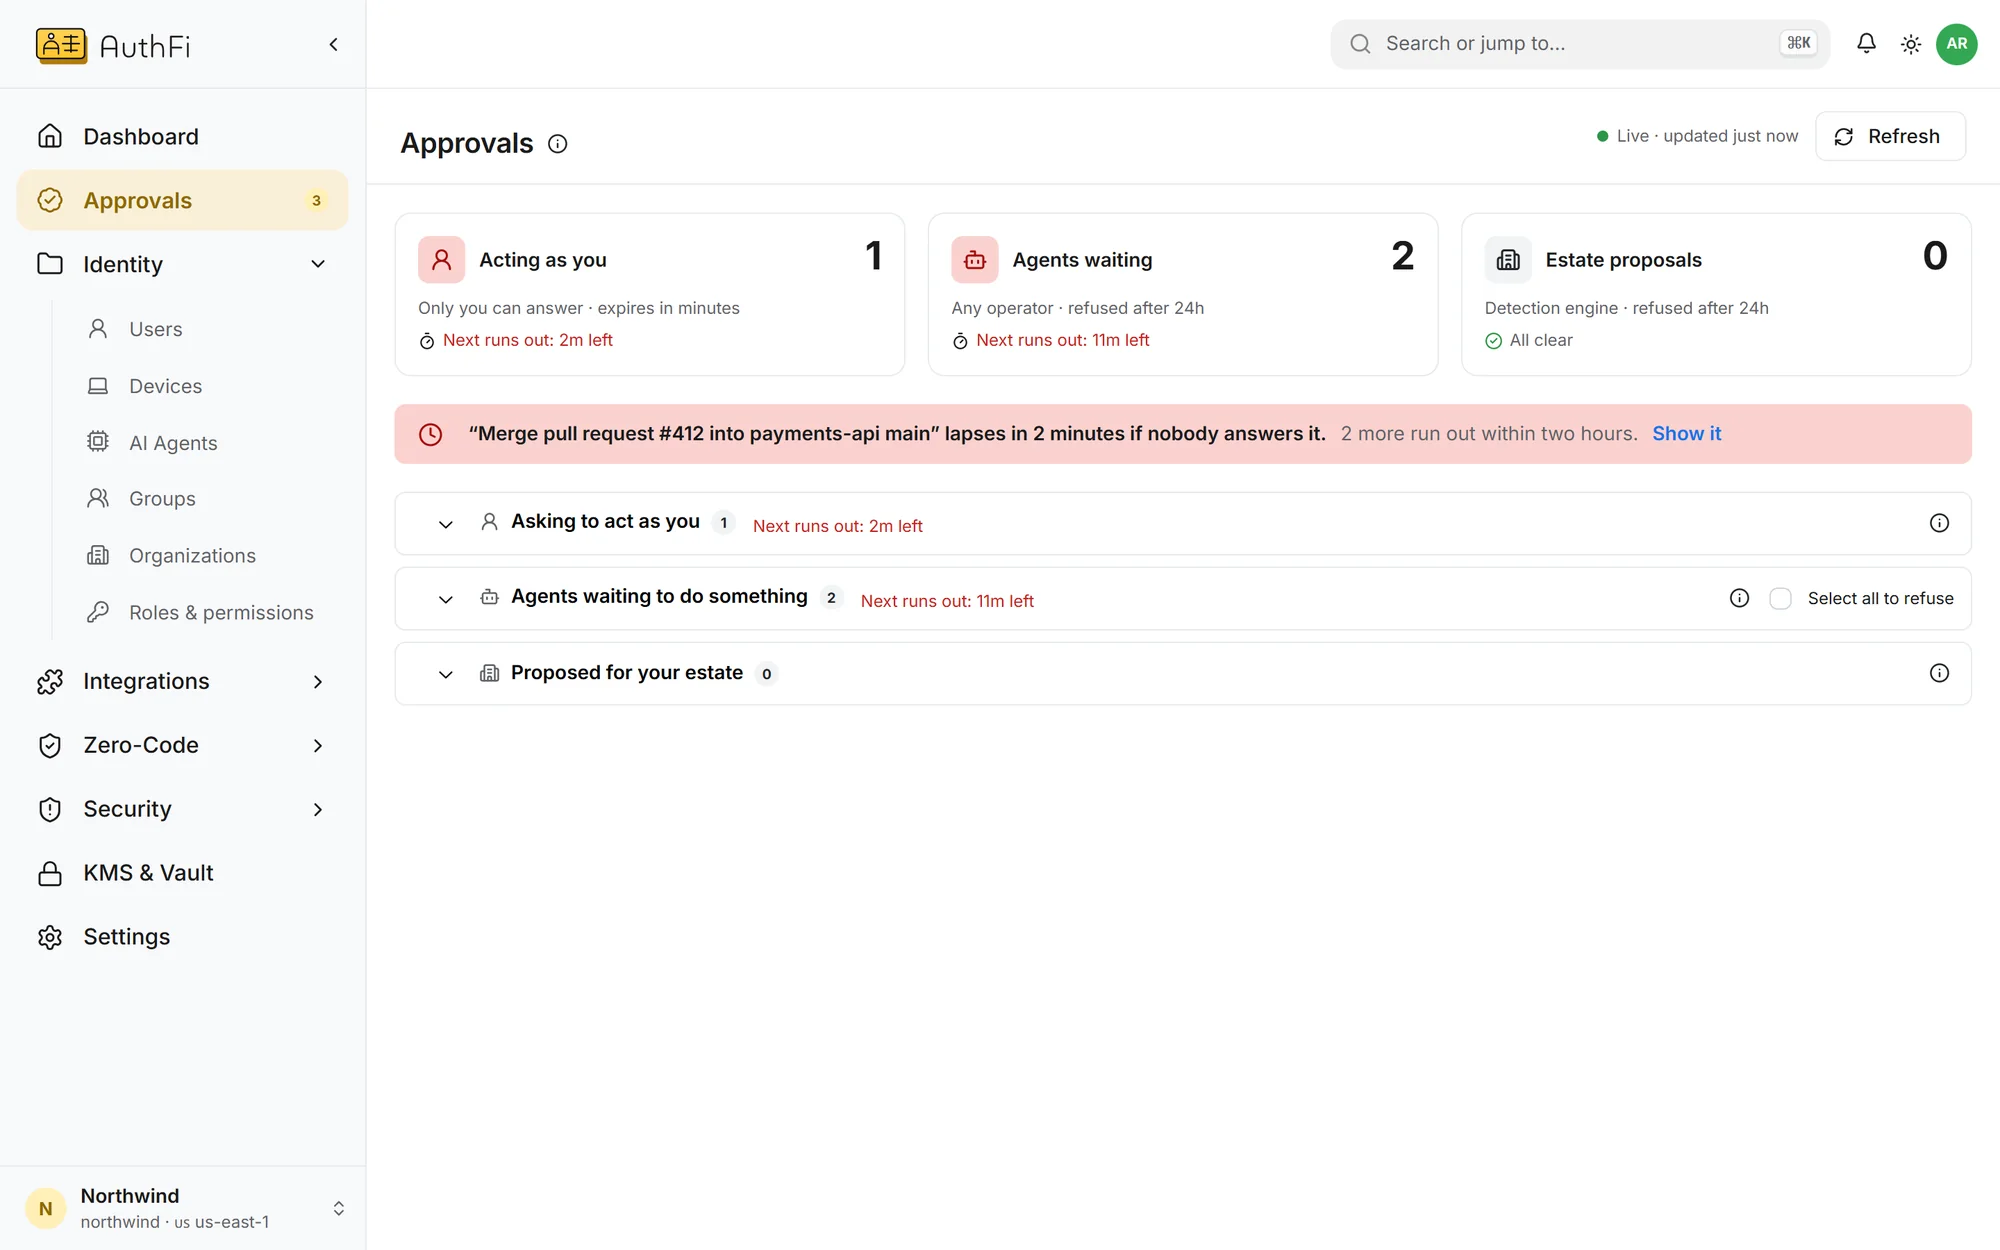
A person decides the actions that matter.
A sensitive action waits for the agent's owner. A request nobody answers is refused.
The request says what, for whom and how much
No answer is a refusal
The decision is on the record
Read on
The boundary on the machine needs Zero-Code, which runs on Kubernetes on Linux.
AI Auth
The AuthFI Agent Profile, step by step
OpenAgent quickstart
Register an agent and get a token
OpenZero-Code
The boundary on the machine
OpenMore in AI enforcement
Give an agent a boundary it cannot leave
On the machine it runs on, an agent reaches only what you granted. Enforced in the kernel.
See howCIBA approvals: a person decides for the agent
Sensitive agent actions wait for a named person, out of band, over OpenID CIBA.
See howMCP gateway: control which tools an agent can call
One MCP gateway for every tool: per-tool grants, checked arguments, no shared credentials.
See how