Solution · Security
Protect every account from takeover.
Most breaches start with a stolen password. Give every person a sign-in that cannot be phished, and take away what an attacker relies on.
Northwind’s sign-in page, not ours
Their logo, colour, headline and domain. Nothing on the page says AuthFI. This is the real hosted sign-in page, running on example data.
Type any email address and press Continue. Or press Create an account.
What changes
The problem as most companies have it today, and the same thing with AuthFI.
How it works
Each step, on the screen you would use.
Sign-in
Sign-in that resists phishing.
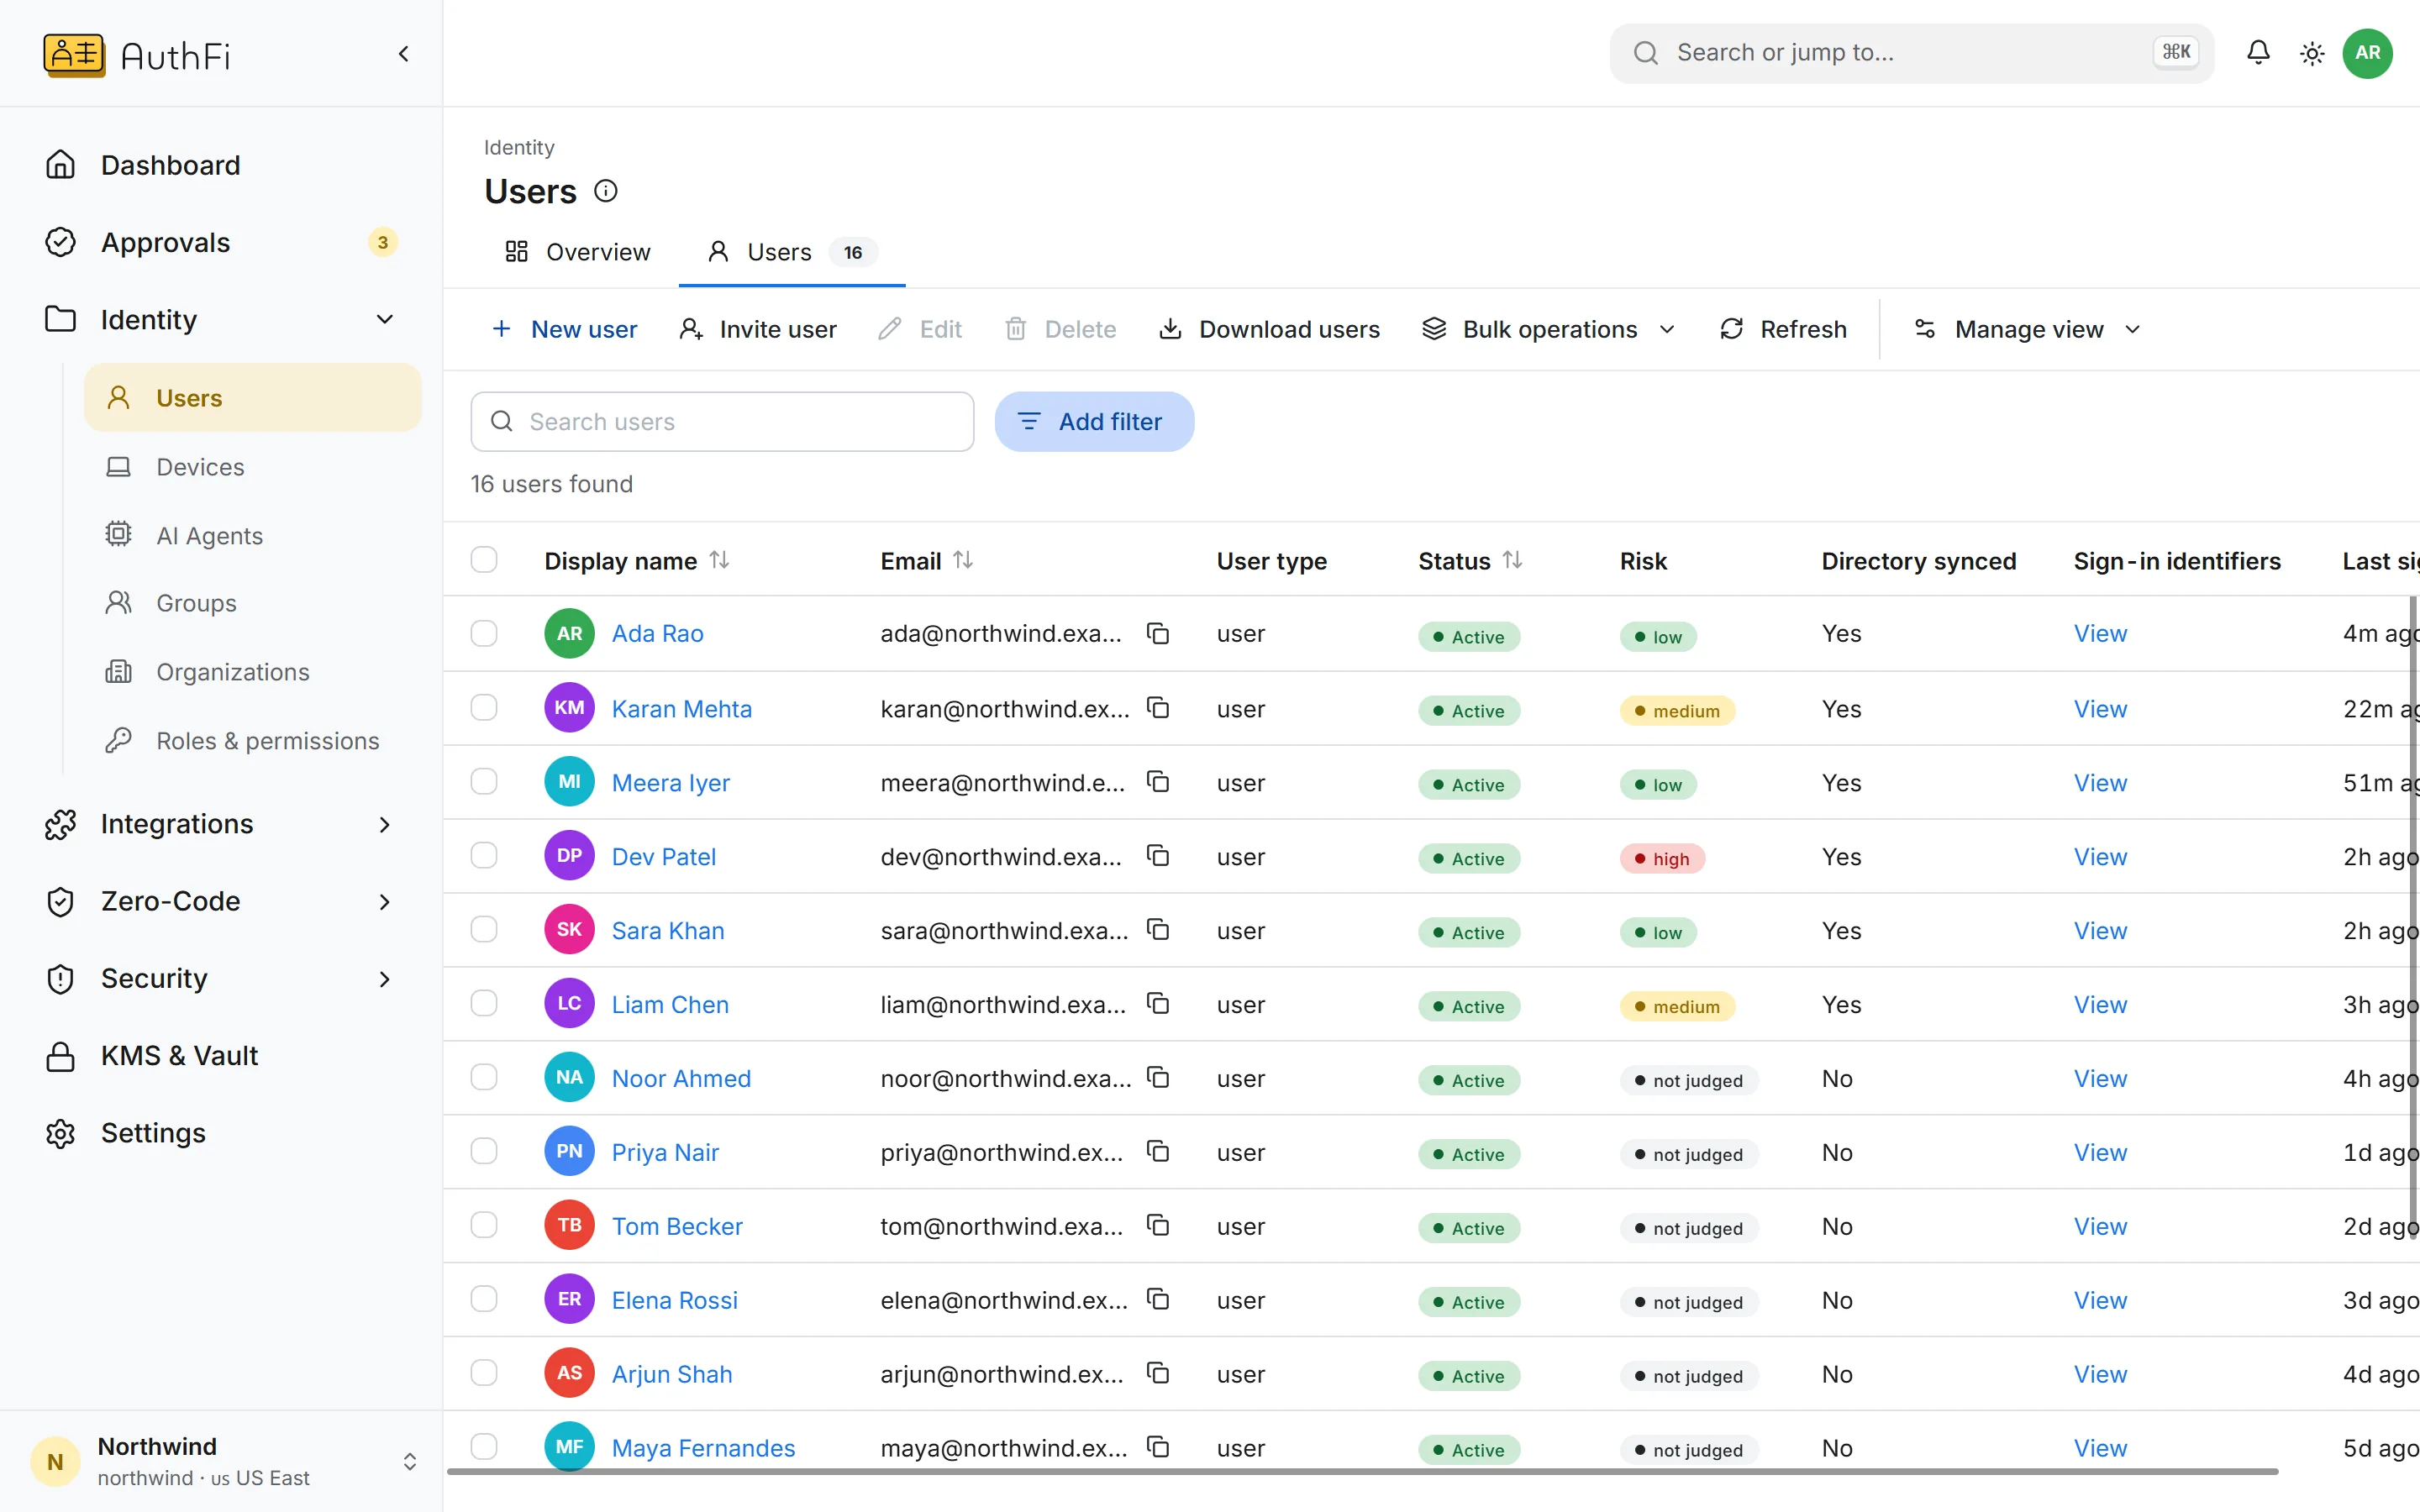
People sign in with a passkey or with a second step, and repeated failed sign-ins from one IP address lock the account out from that address.
Passkeys
A second step, on every plan
Lockout after repeated failures from one IP address
Findings
Told when a sign-in looks wrong.
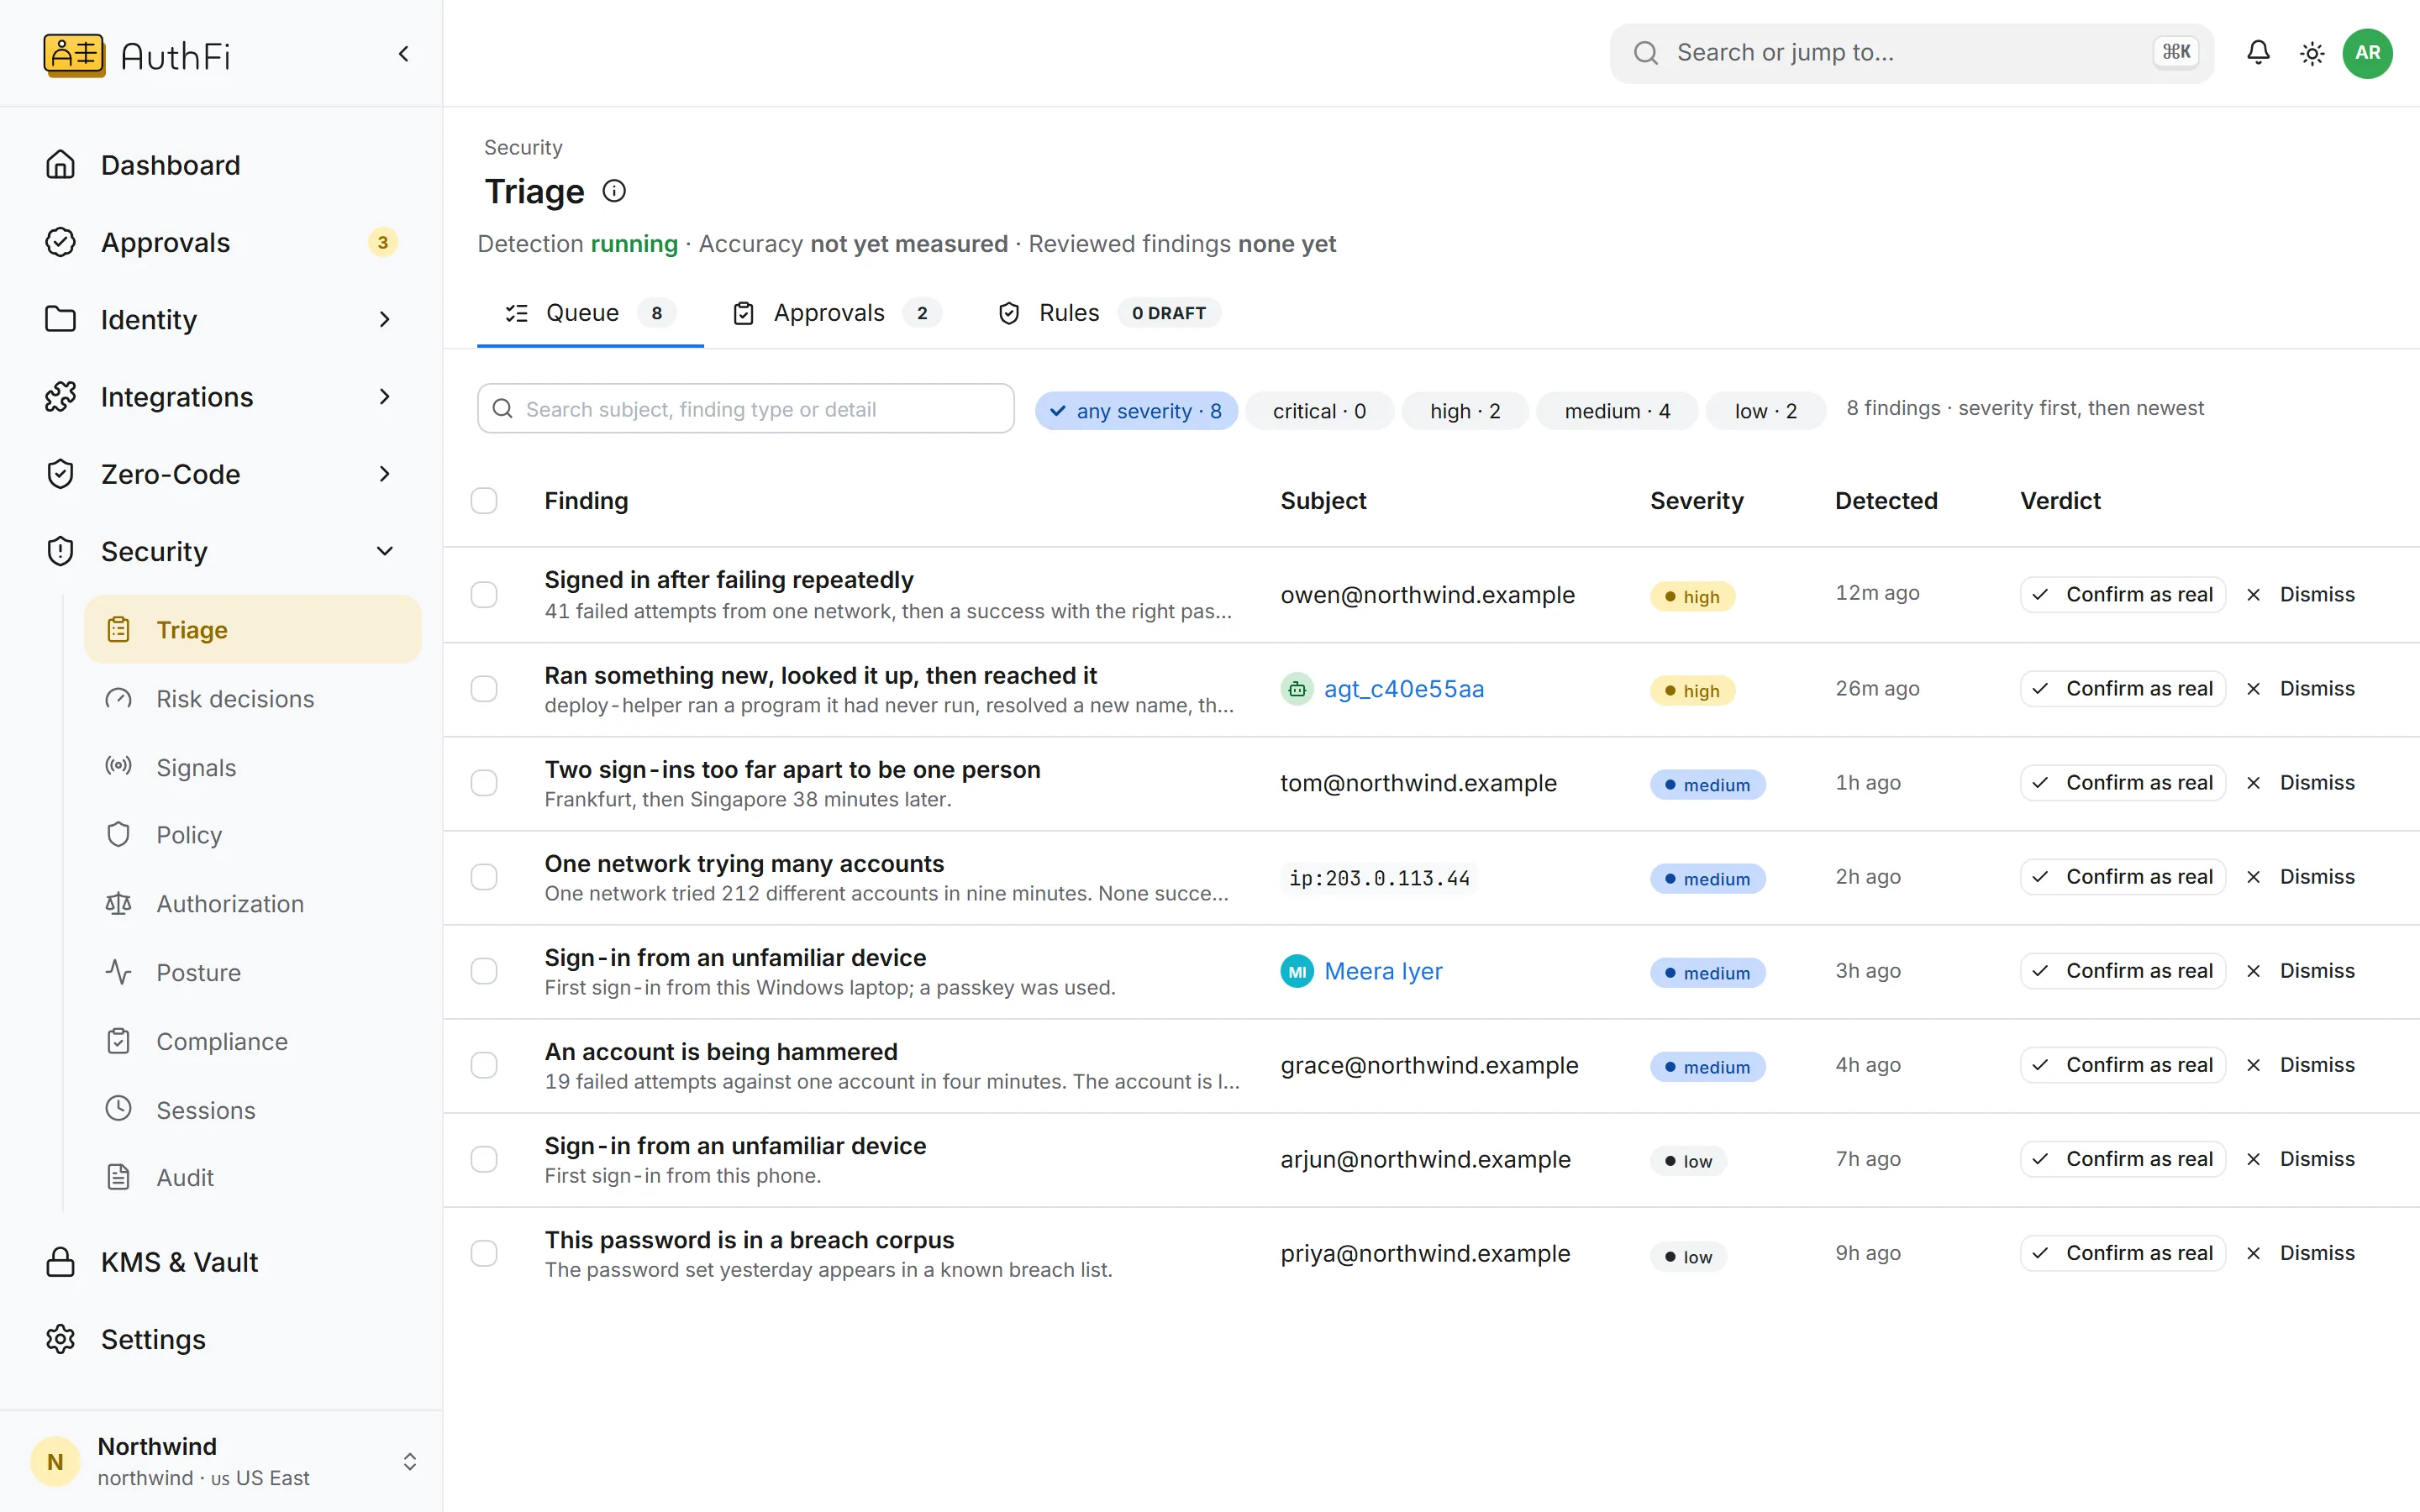
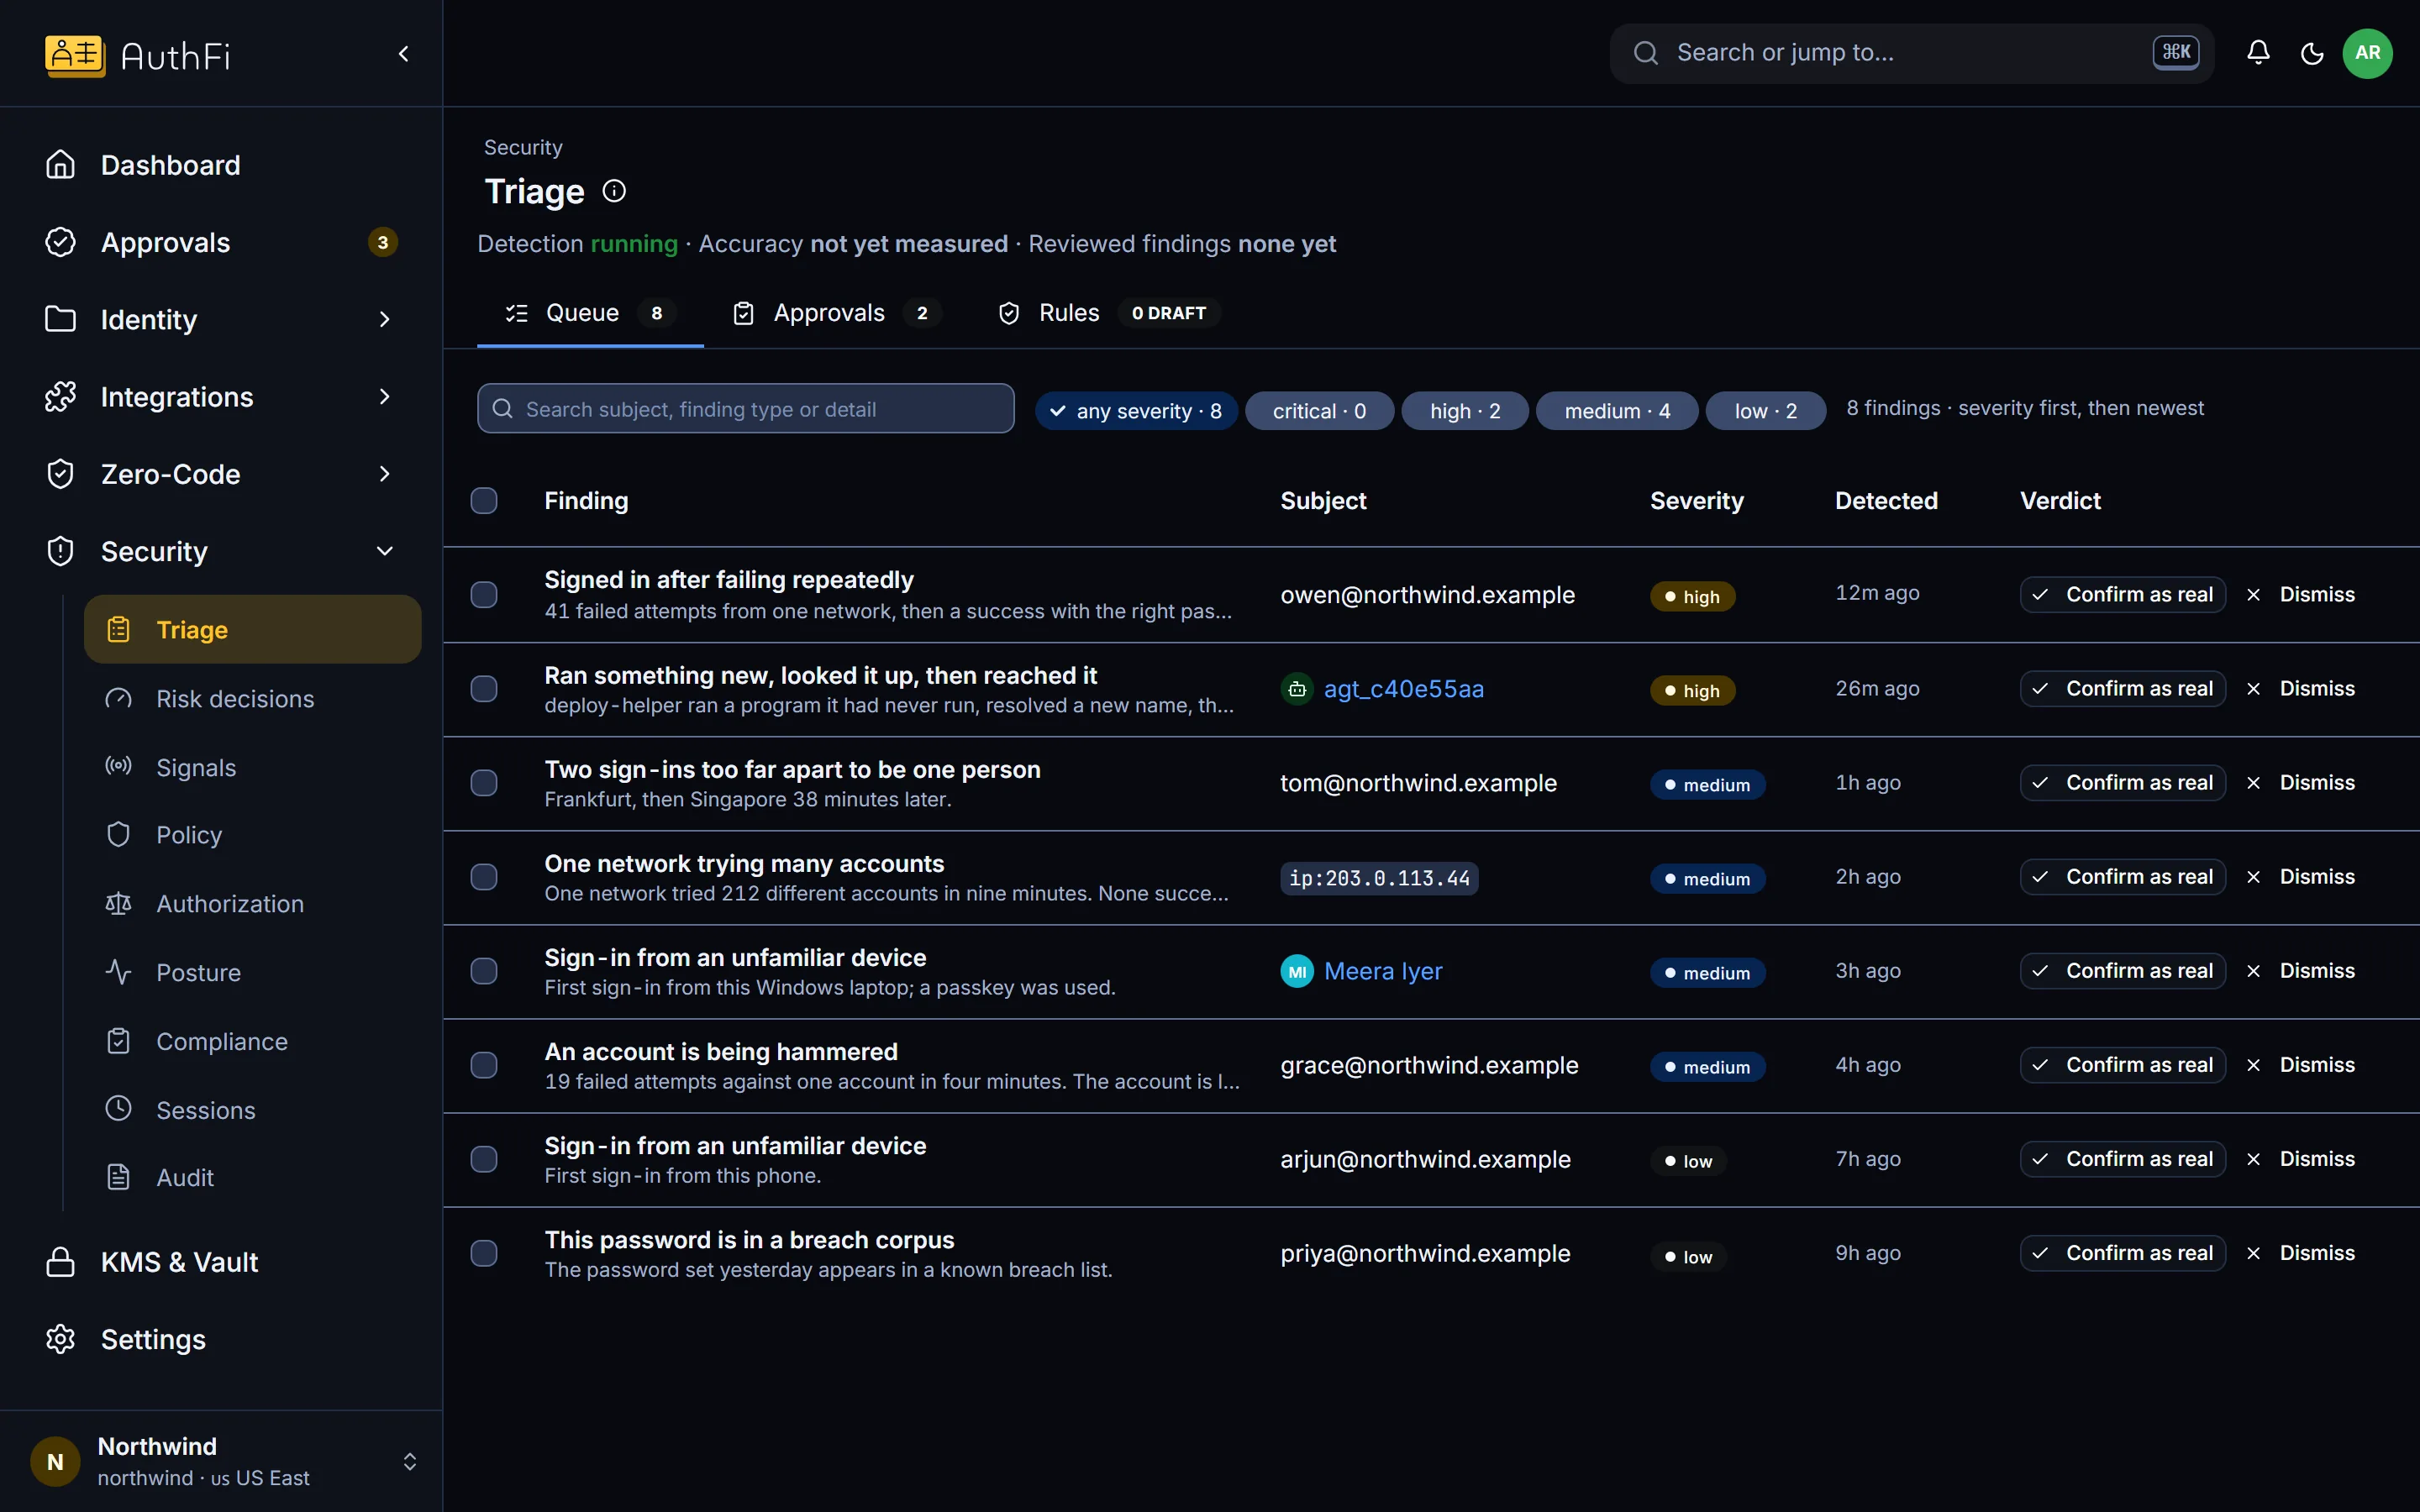
Findings say what was seen in plain words, such as a sign-in after a burst of failures, and a person confirms or dismisses each one.
Plain-language findings
Confirm or dismiss
Your verdict is what the detection learns from
Read on
Findings from sign-in behaviour are in pilot.
Workforce identity
Passkeys, a second step and devices
OpenSecurity and audit
Findings, rules and the record
OpenA modern IdP
The whole workforce story
OpenMore in Security
One record of who did what
Every sign-in, grant, approval and refusal, for people and agents, on one chained record.
See howKnow which of your rules actually refuse
Every rule on the platform, and whether it refuses, only watches, or cannot bite.
See howCatch an agent or workload behaving oddly
Findings when a workload runs something new and reaches out, or a sign-in looks wrong.
See how