Solution · AI enforcement
Stop a misbehaving agent everywhere, at once.
When an agent goes wrong you need one switch, not a hunt for keys. Revoke it once and it is refused at sign-in, at the tool gateway and on the machine.
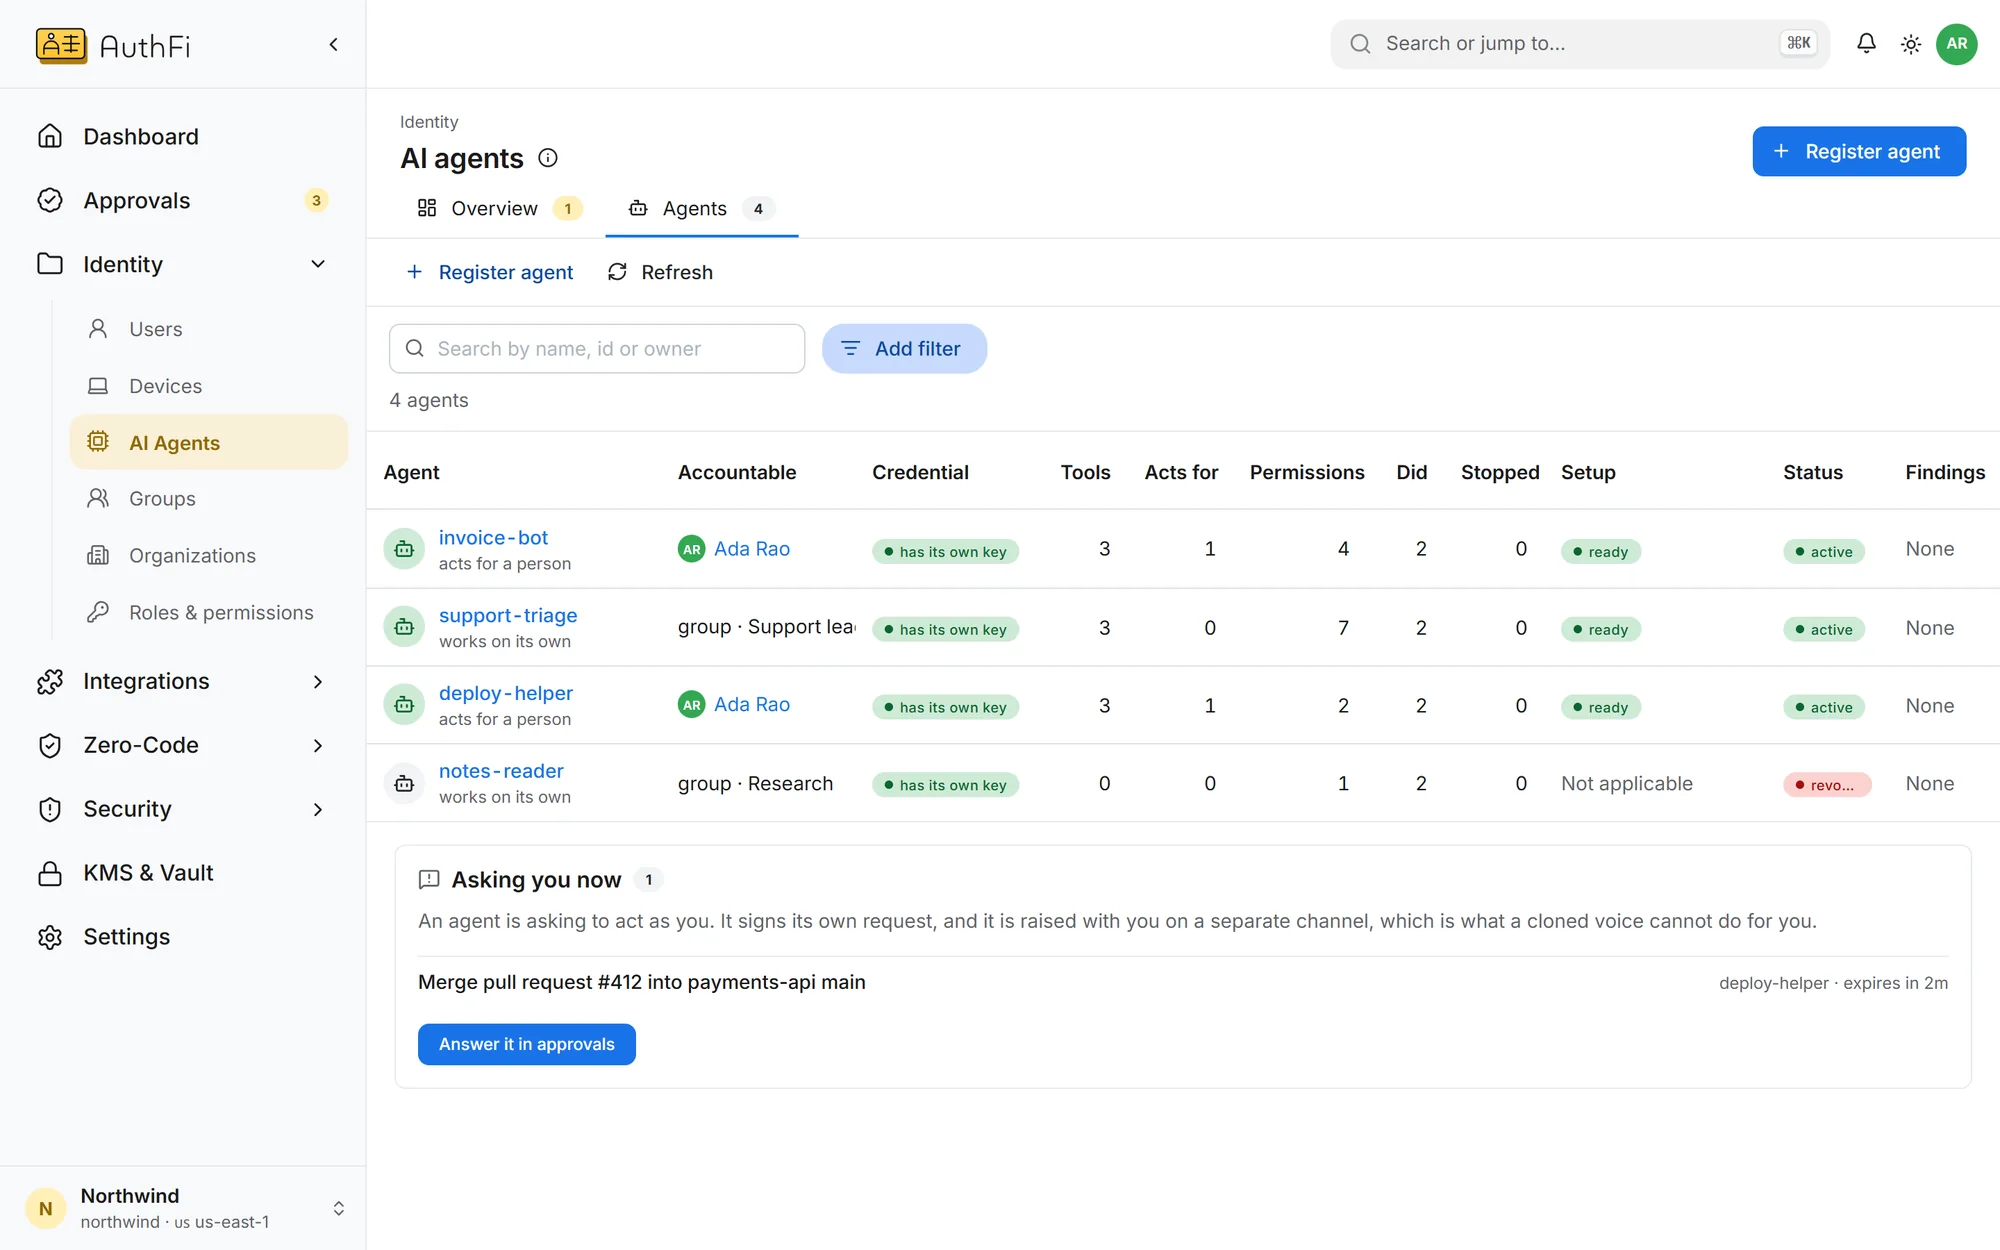
Every agent, with someone accountable
Each agent is listed with its owner, the key it holds, how many tools it has, and what it has been stopped from doing.
What changes
The problem as most companies have it today, and the same thing with AuthFI.
How it works
Each step, on the screen you would use.
Revoke
One switch per agent.
Revoking ends that agent's ability to sign in and leaves every other agent alone. Its history stays for the review.
No new tokens from that moment
Its tool calls and approvals are refused
Machines running Zero-Code are sent the revocation
Afterwards
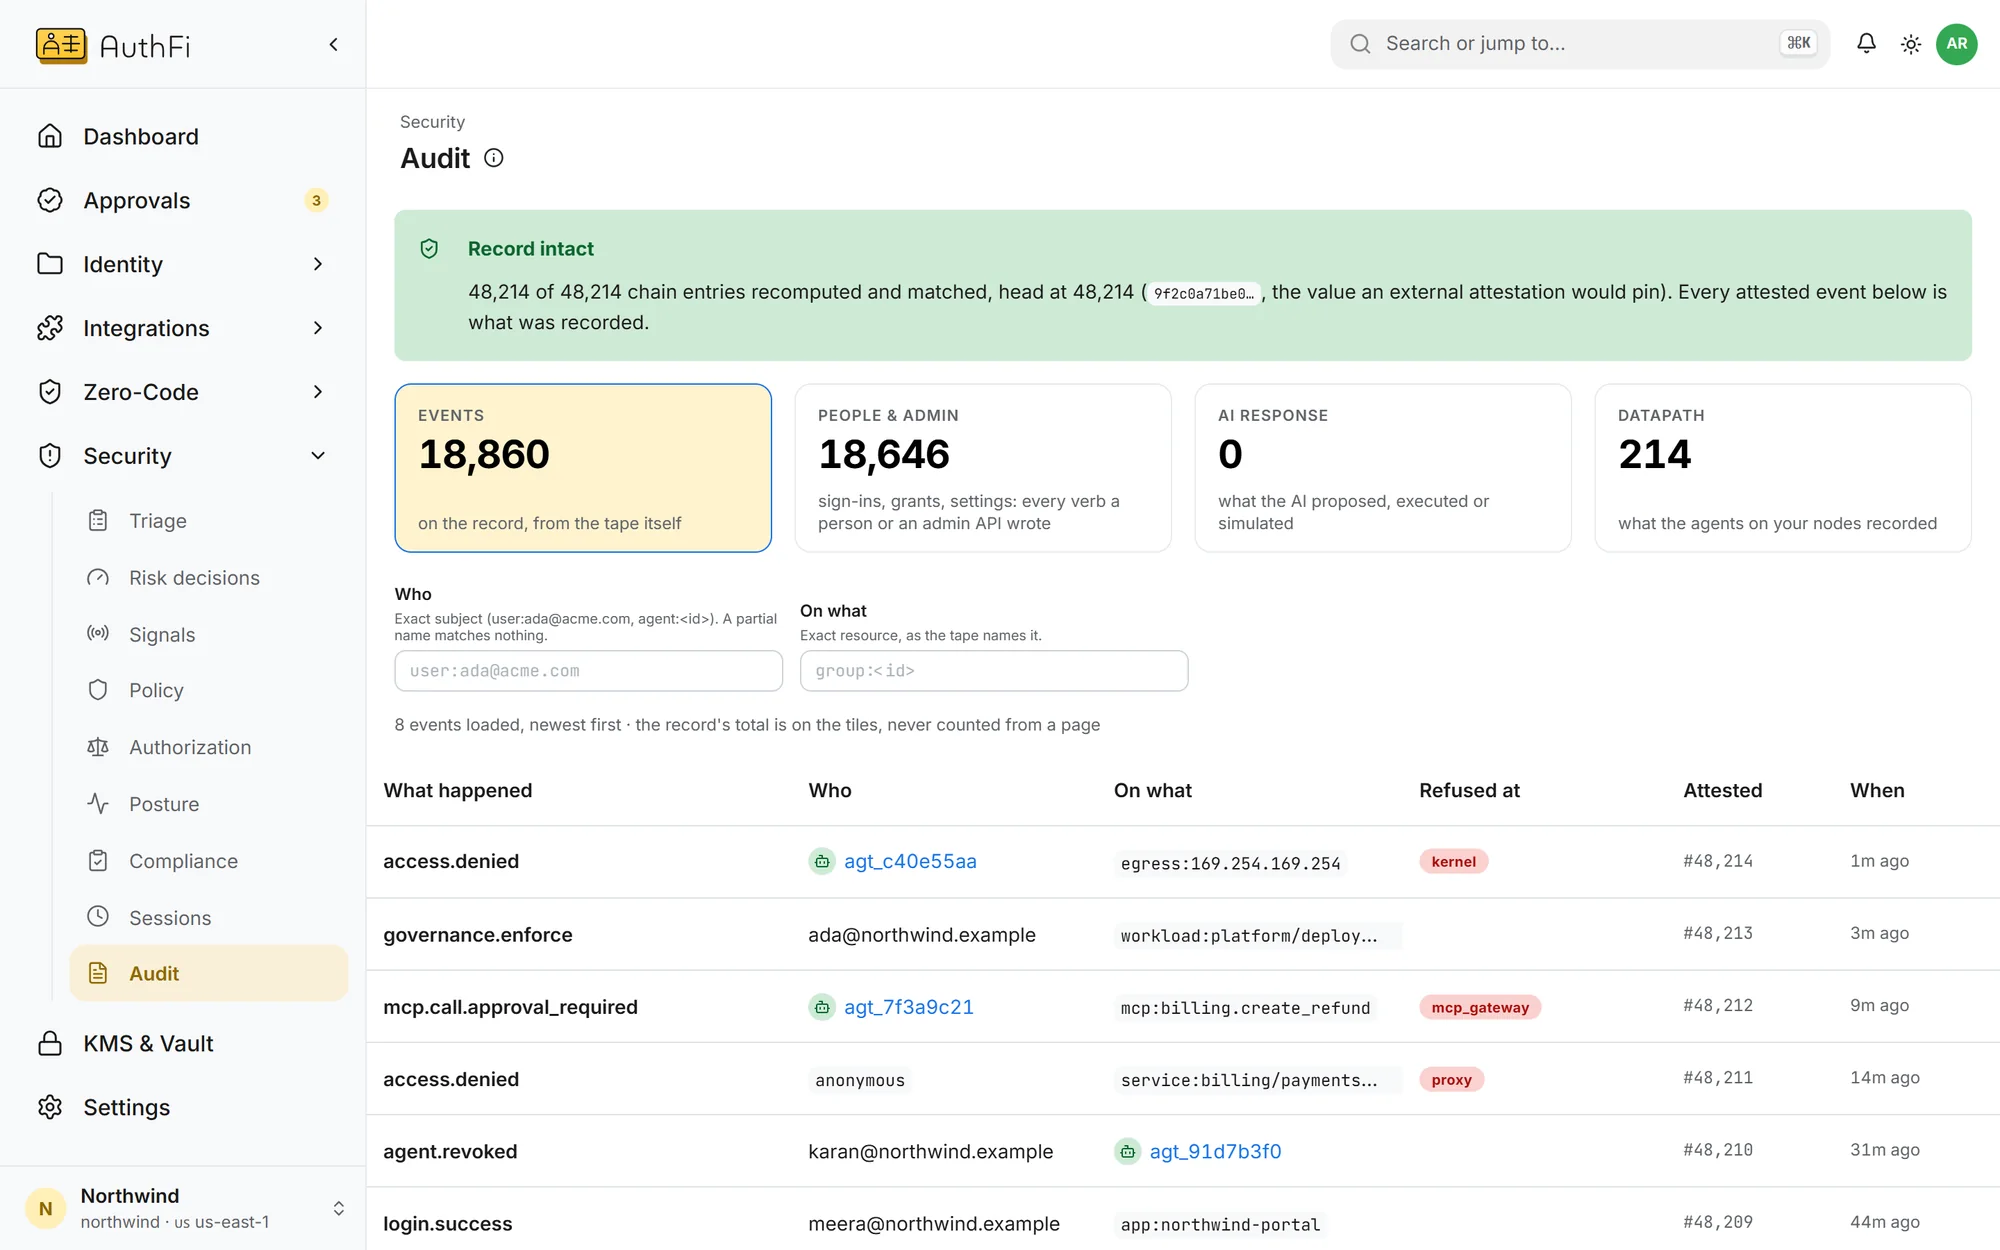
See everything it did, and tried.
The record shows each call the agent made and each one that was refused, so the review starts from facts.
What it did and what it was stopped from doing
Which layer refused each attempt
Export to your incident tools
Read on
A service that only checks a token's signature, and does not listen for revocation events, accepts the token until it expires: 15 minutes at most.
Stop an agent
Revocation and the events you can subscribe to
OpenAI Auth
Nine things a rogue agent tries
OpenAgent boundary
What stops it on the machine
OpenMore in AI enforcement
AI Auth: govern AI agents in production
AI Auth gives every agent an identity, limits and an off switch, on open standards.
See howGive an agent a boundary it cannot leave
On the machine it runs on, an agent reaches only what you granted. Enforced in the kernel.
See howCIBA approvals: a person decides for the agent
Sensitive agent actions wait for a named person, out of band, over OpenID CIBA.
See how