Solution · Security
One record of who did what, and what was refused.
Sign-ins, grants, approvals and refusals for people and AI agents land on one record. Entries are chained, so an edit or a gap shows.
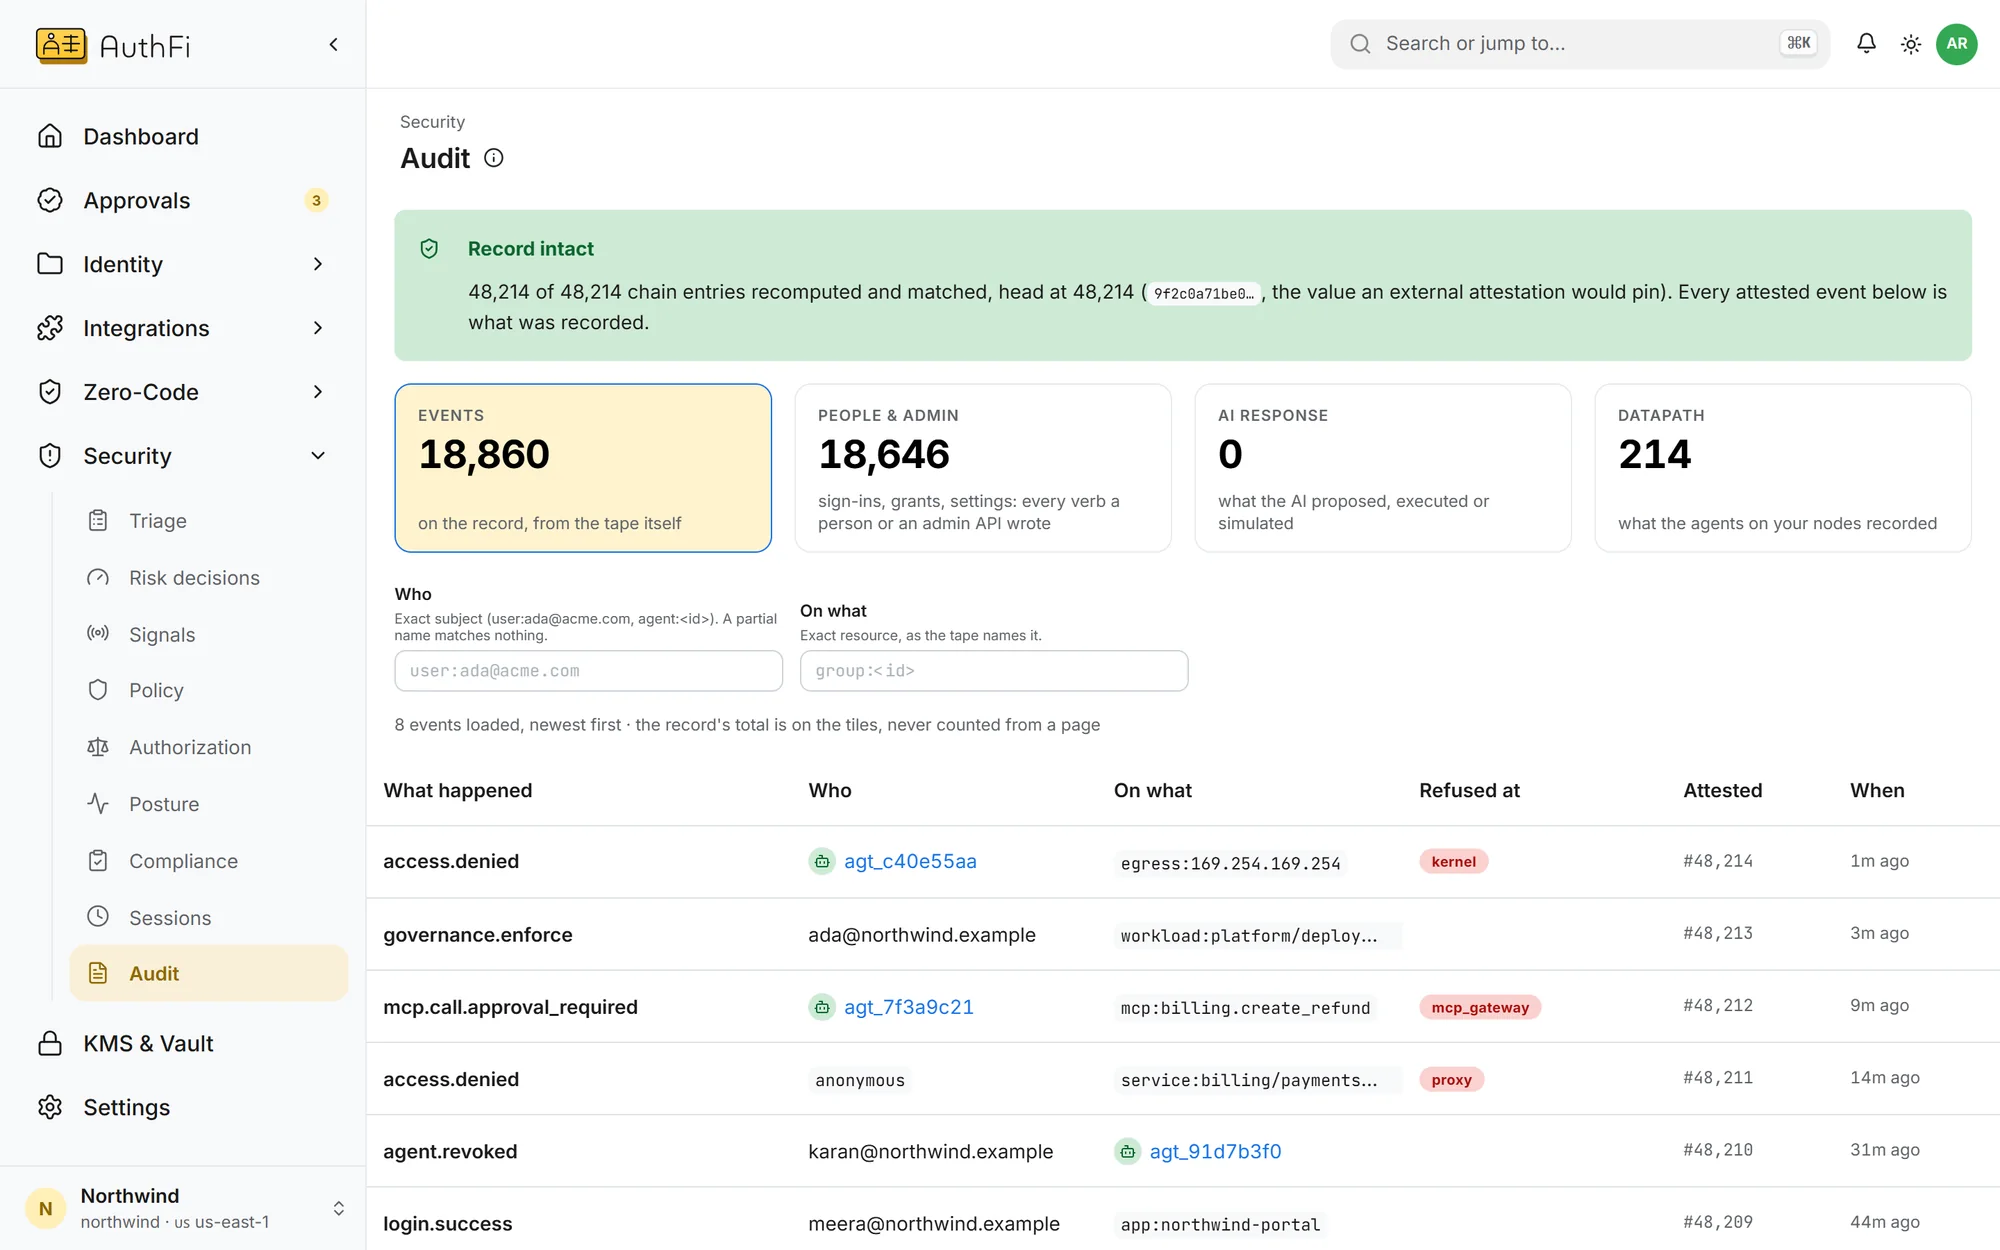
The record
What happened, who did it and at which layer it was refused. The banner says whether the record itself is intact.
What changes
The problem as most companies have it today, and the same thing with AuthFI.
How it works
Each step, on the screen you would use.
Record
Read it by person, action or layer.
Filter by who did it, what they did, or where a refusal happened: at sign-in, at the tool gateway, at the service or on the machine.
Who, what, on what, and when
The layer that refused
A banner that says whether the chain is intact
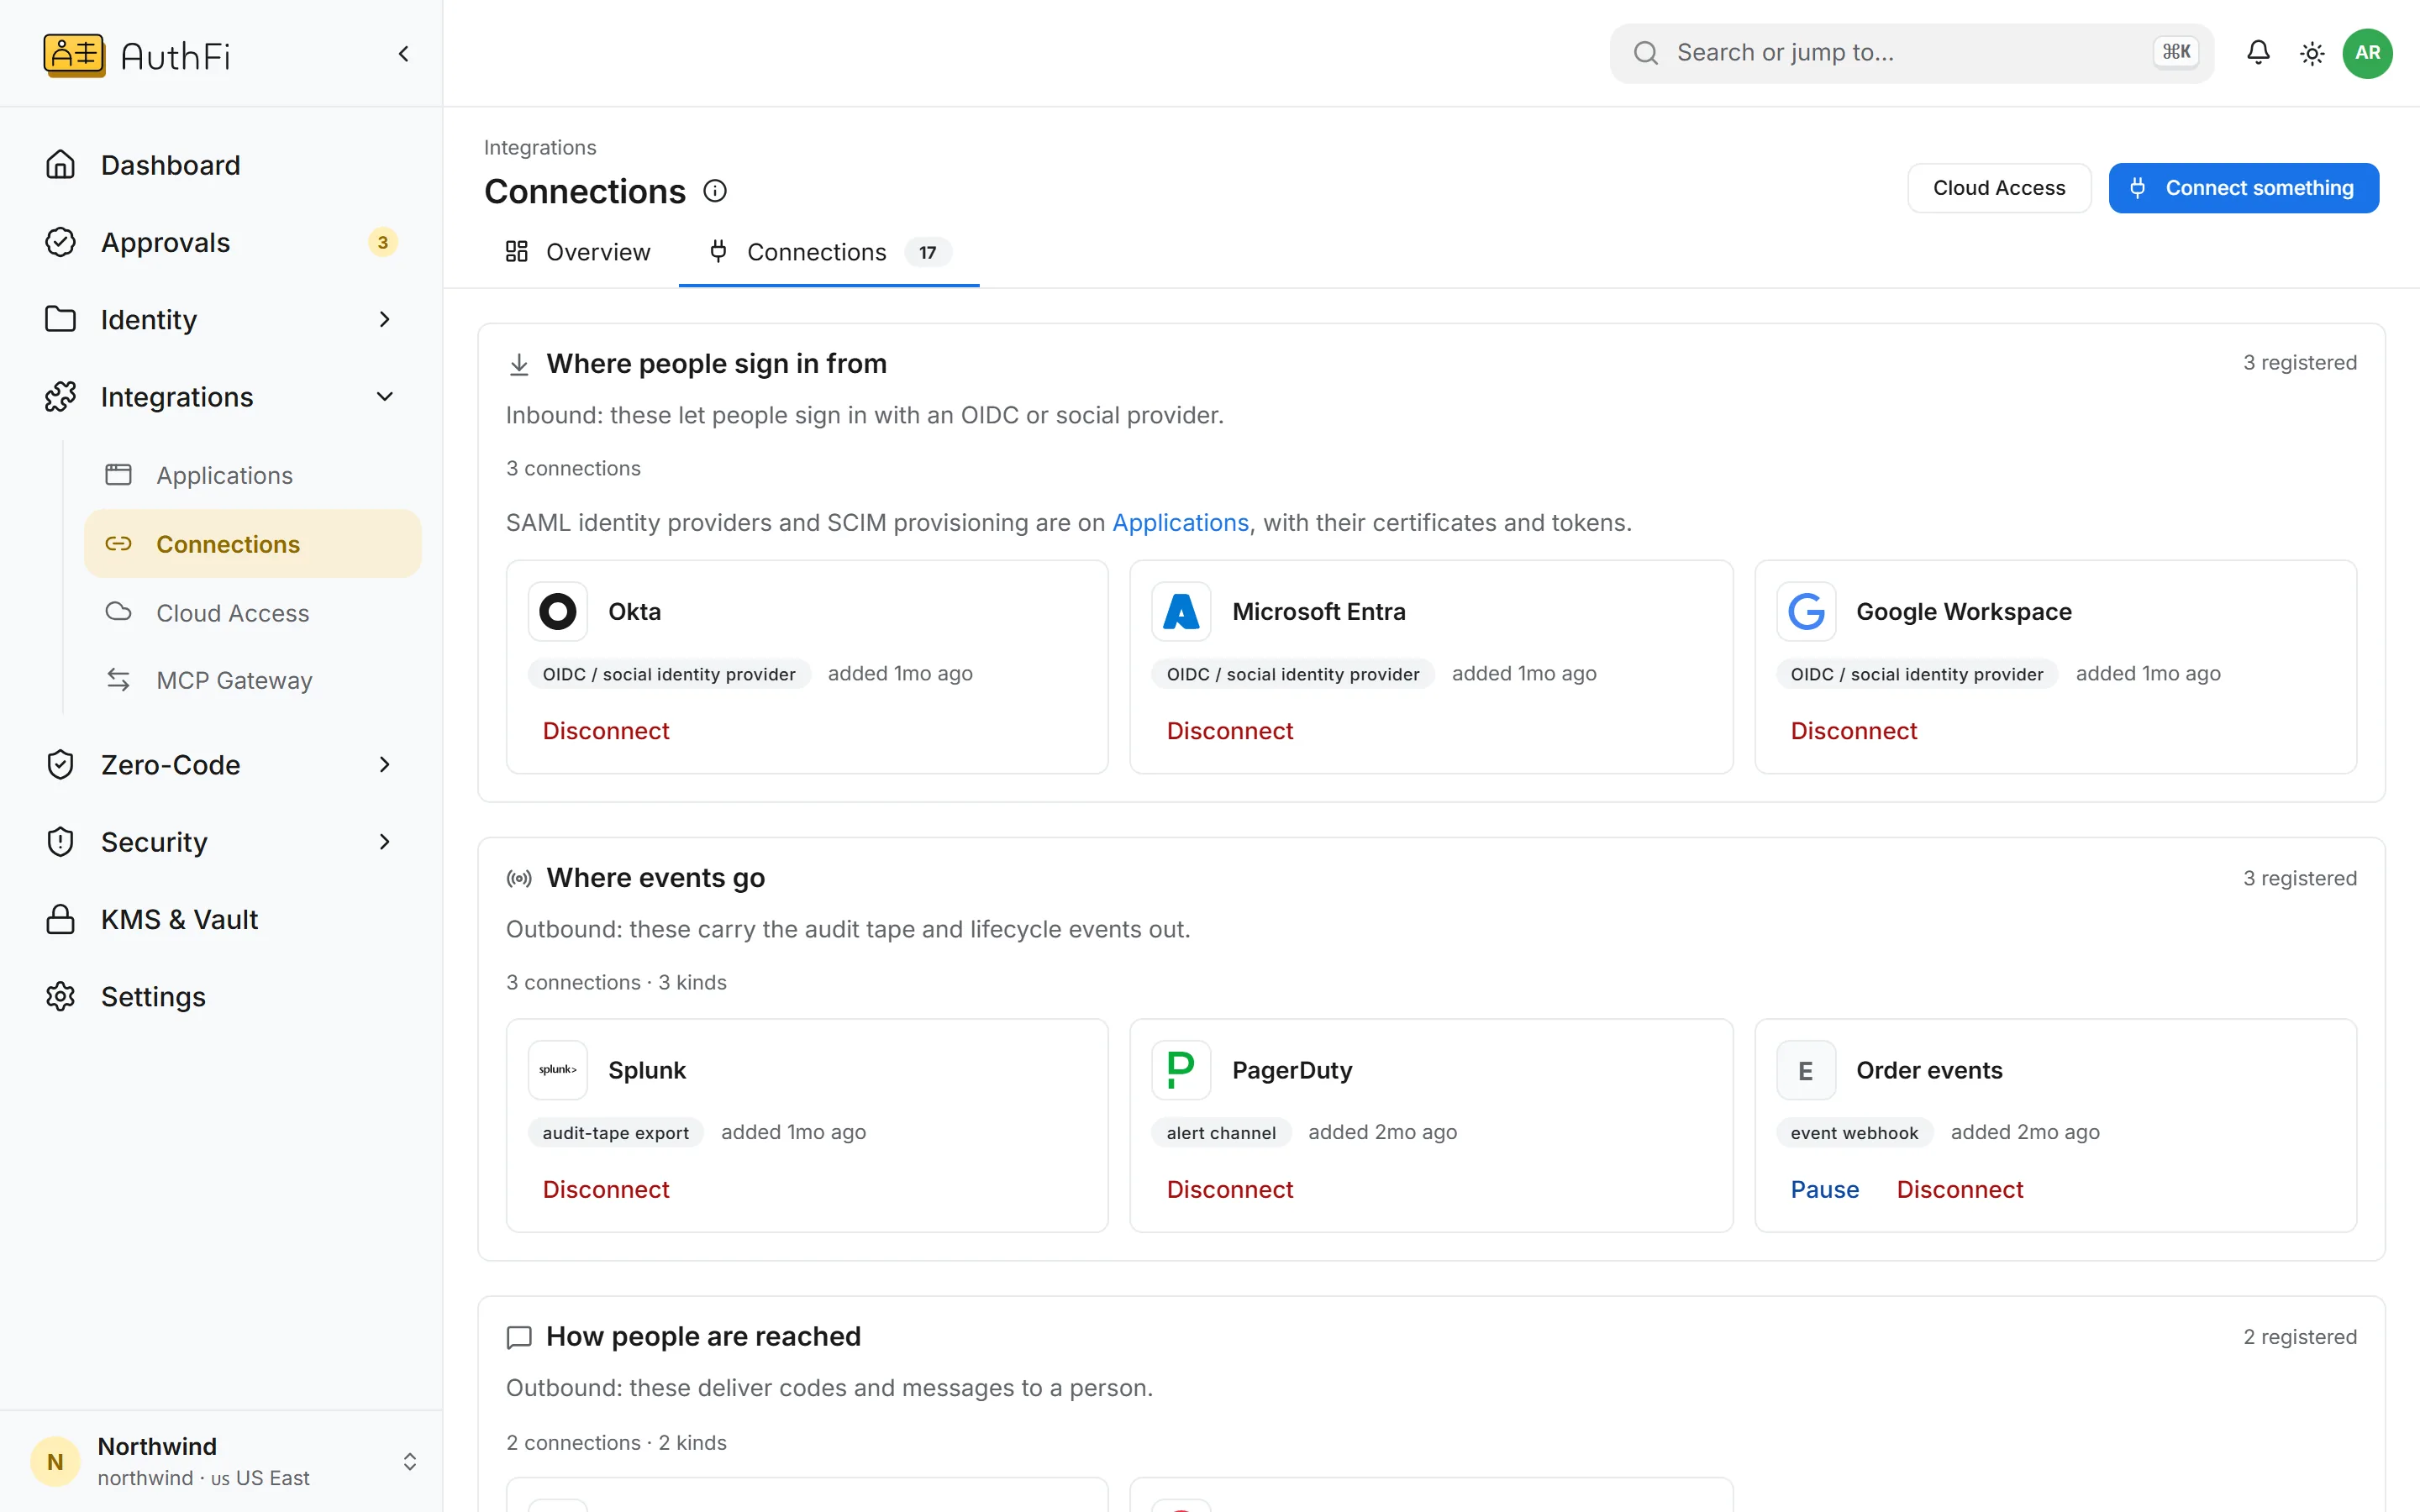
Export
Send it where your team already looks.
Connect the log and alerting tools you use and the record is delivered to them as it is written.
Your log tools and your own webhooks
Alerts to the channels you use
Yours to keep for as long as you need
Read on
The parts of the product behind this.
Security and audit
The record, the rules and the findings
OpenRules in force
Which of your rules actually refuse
OpenFinancial services
What an auditor asks for
OpenMore in Security
Know which of your rules actually refuse
Every rule on the platform, and whether it refuses, only watches, or cannot bite.
See howProtect every account from takeover
Passkeys, a second step on every plan, lockout, breached-password checks and sessions you can end.
See howCatch an agent or workload behaving oddly
Findings when a workload runs something new and reaches out, or a sign-in looks wrong.
See how